It’s official: the lifespan of SSL/TLS certificates will be reduced to 47 days

It's official: the lifespan of SSL/TLS certificates will be reduced to 47 days

On 9 October 2024, Apple announced at the CA/B Forum (Certification Authority Browser Forum) its intention to reduce the maximum duration of public SSL/TLS certificates to 45 days by 2027, as well as to reduce the DCV challenge reuse period to 10 days by 2027.

This request was then discussed and amended six months later, again by Apple, which proposed a change to the initial schedule with a reduced certificate duration of 47 days for SSL/TLS certificates and a DCV challenge validation period of 10 days from 15 March 2028.

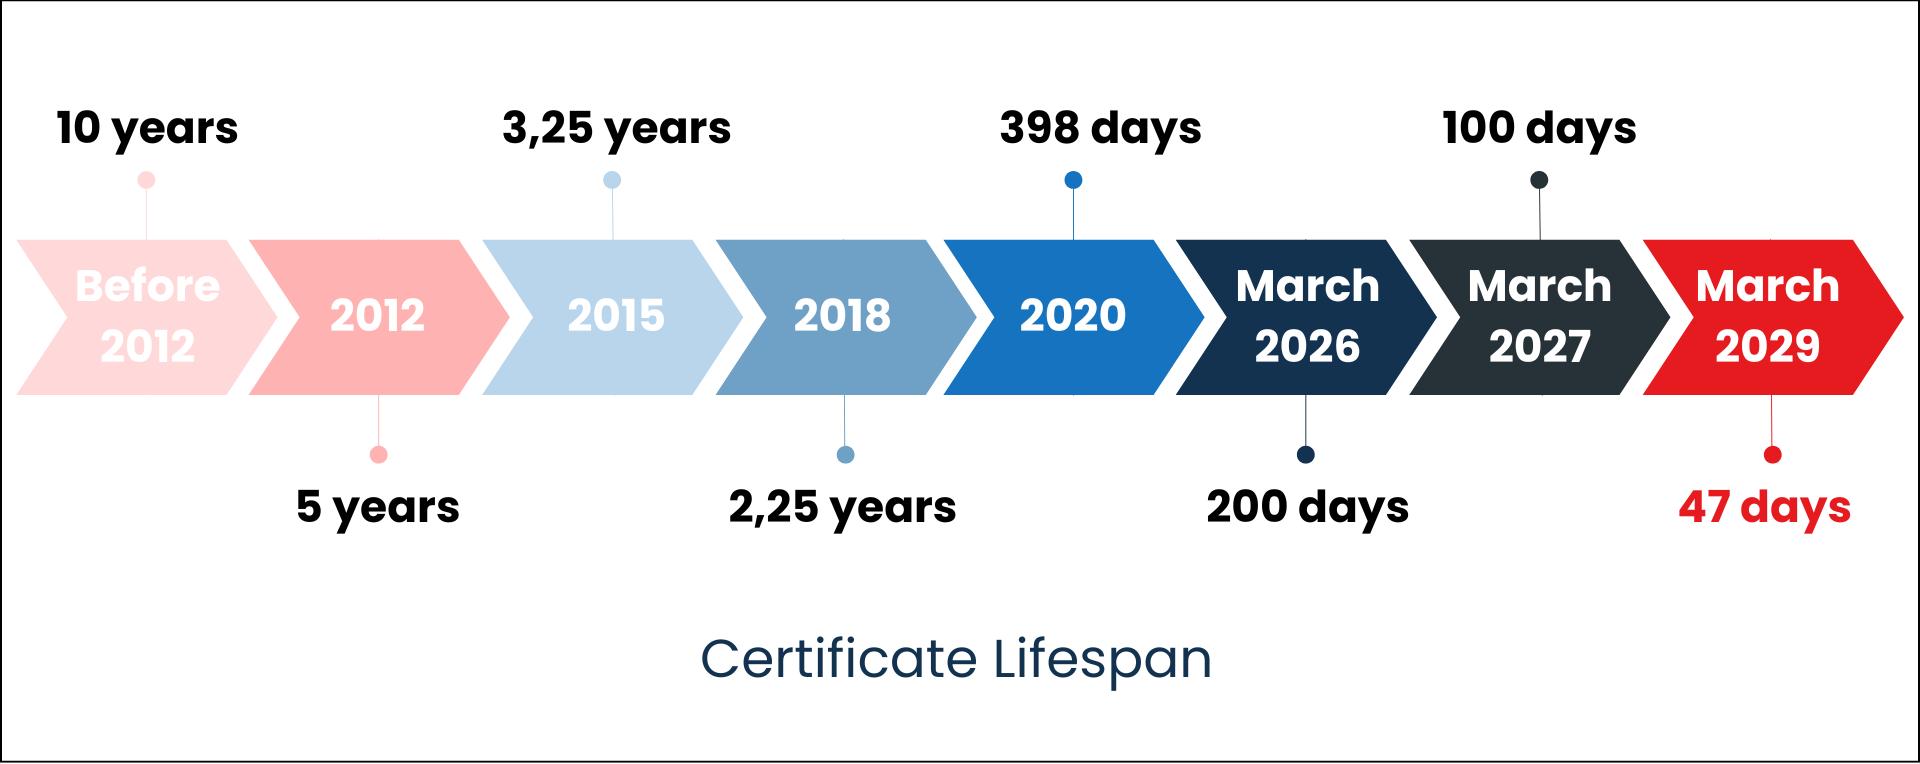
This measure officially comes into force following the CA/B Forum vote in April 2025, which adopted a new implementation schedule, officially reducing the validity of certificates to 47 days and thus promoting automation for the proper management of these certificates.

  • Until 15 March 2026, the maximum TLS certificate lifetime will remain at 398 days.
  • From 15 March 2026, the maximum TLS certificate lifetime will be 200 days.
  • From 15 March 2027, it will be reduced to 100 days.
  • And from 15 March 2029, the maximum TLS certificate lifetime will be reduced to 47 days.
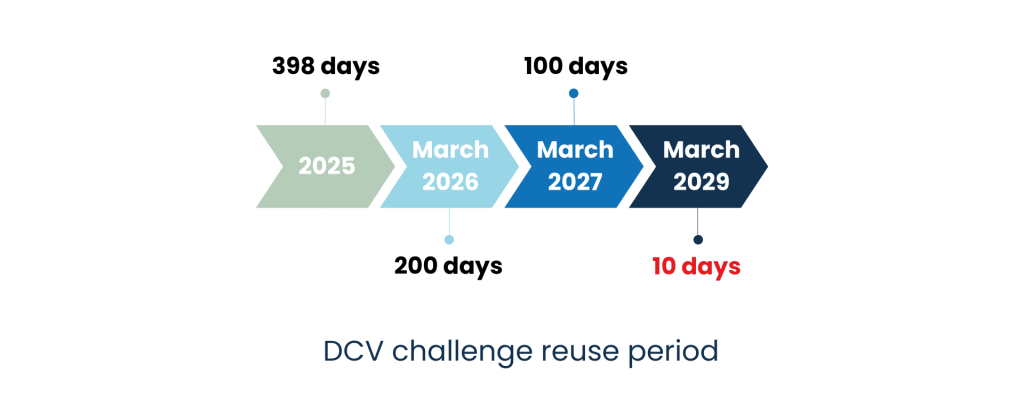
At the same time, the reuse periods for Domain Control Validation (DCV challenge), which involve intervening in the domain name zone listed in the certificate to validate it, will be aligned with the certificate schedule, reaching 10 days in 2029.

  • Until 15 March 2026, the maximum period during which domain validation information can be reused is 398 days.
  • From 15 March 2026 onwards, the maximum period during which domain validation information can be reused is 200 days.
  • From 15 March 2027 onwards, the maximum period during which domain validation information can be reused is 100 days.
  • From 15 March 2029 onwards, the maximum period during which domain validation information can be reused is 10 days.
Faced with these major changes coming in 2026, it is essential for businesses to prepare

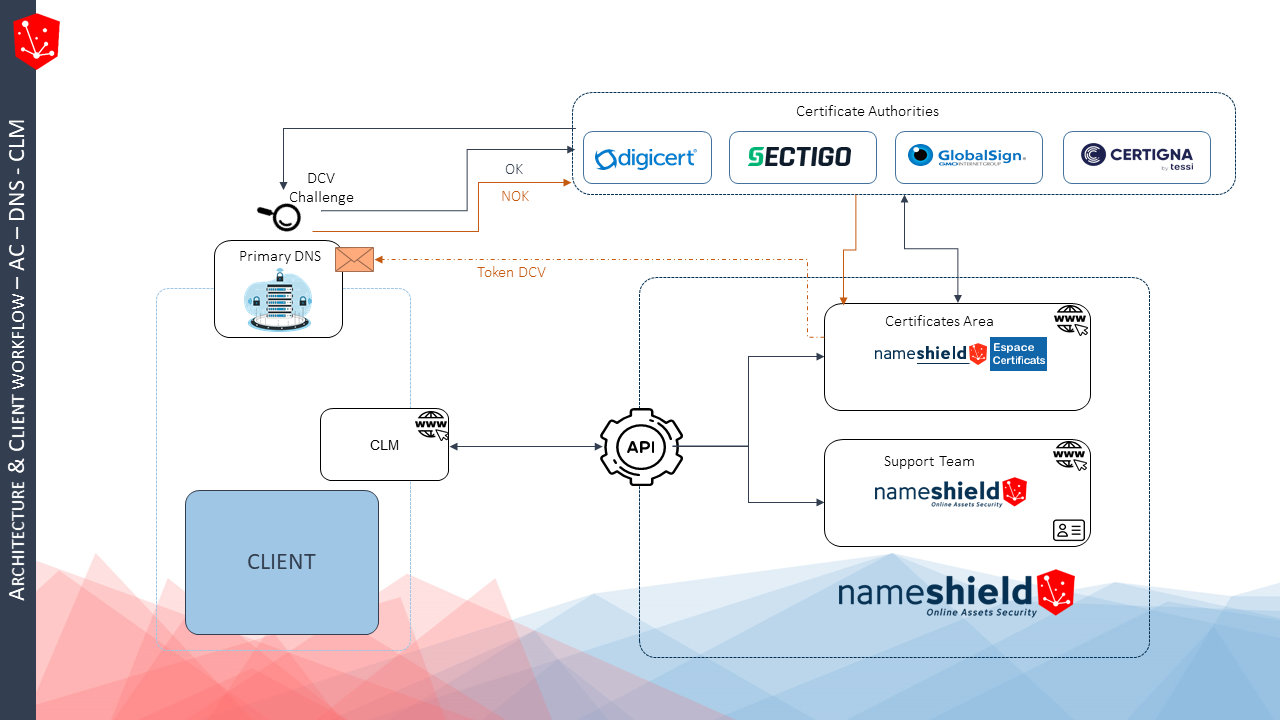
The CA/B Forum’s initiative will gradually transform the digital certificate security landscape. The validity period of SSL/TLS certificates will be reduced, accompanied by stricter DCV challenge validation rules. The key to effective certificate management in the future will therefore lie in automation. With certificates valid for 47 days in 2029, that means nine interventions per year per certificate, making manual management unfeasible. It will therefore be necessary to rely on the following services/software:

  • Certificate provider/Certification Authority (CA): a trusted partner who will assist you with organization and domain authentication issues. The level of service is key to effective management. A multi-CA partner is recommended to limit dependence on a single CA, as demonstrated by the recent difficulties experienced by Entrust.
  • Registrar/Primary DNS: controlling the primary DNS of the domain names listed in the certificates will become key to delivery. Each certificate issue will result in the installation of a TXT or CNAME on the zone(s) concerned. Having an interconnection between the CA and the DNS is essential.
  • CLM editor: the CLM is responsible for inventorying the certificate pool, defining pool management rules, and ensuring complete automation of the ordering process, from CSR generation to certificate deployment on servers. To function, it relies on connectors with CAs or certificate providers.

Preparing therefore means identifying the solutions that suit you best in these three areas and starting to think about the impact on processes, technology and budget, so that you are ideally prepared for the first half of 2026.

Nameshield, an ally to help you manage these changes

Nameshield occupies a unique position in the market as both a registrar and a provider of multi-CA certificates. For over 10 years and on a daily basis, we have been managing all issues related to organization and domain authentication linked to certificates, thanks to our privileged relationship with the largest CAs on the market (Digicert, Sectigo, GlobalSign) and our expertise in DNS for DCV challenge validation. As a result, we issue public certificates almost instantly. Finally, regarding the CLM component, Nameshield has connectors with the largest players on the market to enable you to ensure a complete connection between the various components related to certificate management. We therefore support you in anticipating all the issues mentioned above.

If you have any further questions, you can contact Nameshield directly here.
ICANN82: Stability, security and unity in opposition to current upheavals

The 2025 season of ICANN meetings on Internet governance kicked off in March in the Emerald City of Seattle in the United States of America. 2025, a year of ‘exceptional times’, as Tripti Sinha, the Chair of the Board of Directors, described it. At a time when the world is being turned upside down by geopolitical and technological developments such as AI and quantum computing, ICANN wants above all to look at ‘what can be controlled’ and at opportunities, with the preparation of the next series of new generic extensions and the fresh look of its President Kurt Erik ‘Kurtis’ Lindqvist, who took up his position 91 days before ICANN82.

The right time for an examination of conscience

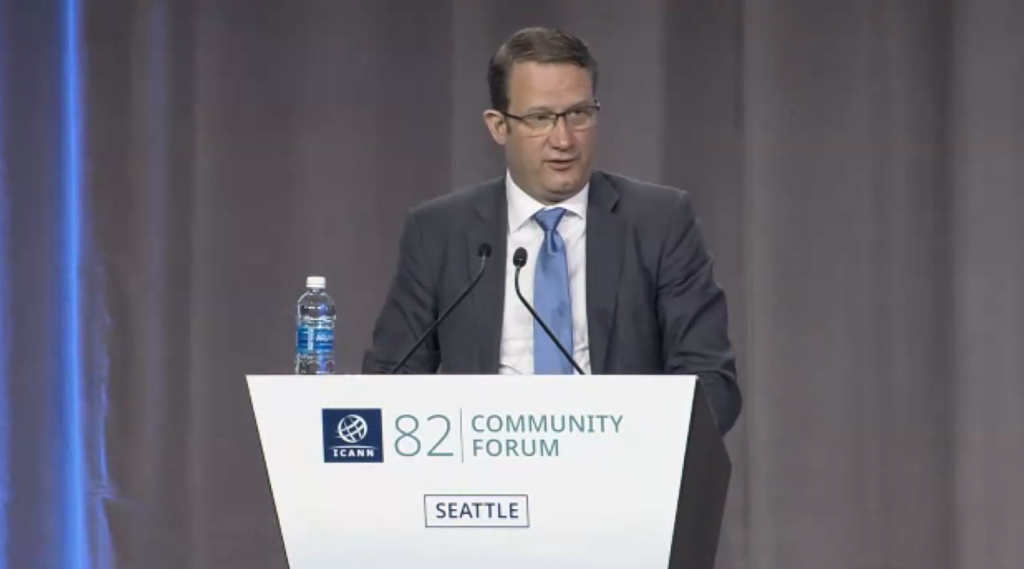
On the occasion of his first summit as current ICANN President, Kurt Erik Lindqvist said he had been well received by the community. He hopes that the identification of problems will be anticipated in order to make ICANN’s processes more fluid and the organisation’s approach to become more agile. For the next series of new generic extensions, which is a crucial issue for the organisation, he stated that everything necessary is being done ‘to keep to the timetable’.

On the subject of financial sustainability, another central issue, Tripti Sinha recalled that ICANN was completing its 2026-2030 strategic plan to anticipate future needs. A plan that should promote a multi-stakeholder and inclusive approach, continue the culture of continuous improvement, focus attention with stakeholders on emerging technologies and strengthen the security and stability of the Internet. On a more serious note, she pointed out that we are in a world that has become ‘unpredictable’. She said that in ‘extraordinary times’, ‘the human spirit seeks stability, security and unity that are embodied in ICANN’s mission statements’ and that ‘ICANN must remain a reliable and stable institution.’

Kurt Erik Lindqvist now acting as CEO of ICANN

The opening ceremony was followed by a session led by Sally Costerton, who is now the President’s advisor on community engagement. She led a session on community feedback on the operation of the annual meetings organised by ICANN. While 1,828 people were registered for ICANN82 when it was launched, participants learned that the costs of the summits have increased by 31% between 2018 and 2024, currently representing a budget of USD 2.3 million per meeting. Various options were discussed, such as charging for attendance at summits or, more likely, reducing the number of face-to-face meetings or their duration.

The next series of new generic extensions is becoming clearer and clearer

While up until now we have heard talk of April 2026 as the opening date for submitting applications for new top level domains, the date of 25 April is now considered to be D Day. The cost of the next round is also known, with the application fee set at USD 227,000, as announced in former articles. This amount is based on a projection of 1,000 applications, which would enable a financial break-even point to be reached. The applicant support programme, which aims to support less favoured geographical areas, is also on track and is already accepting applications. At ICANN82 we learned that 13 applications had been initiated in the programme. On the other hand, the implementation of all the recommendations of the Subpro policy development process is still in progress. The current focus of work in progress includes the formulation of the new Registry agreement to be signed by future registry operators and the long awaited Applicant Guidebook.

Thirteen years after the previous series of new generic extensions, a session was also devoted to the ICANN Grant programme. The aim of this programme is to redistribute, through financial support, part of the reserve fund resulting from the auctions linked to multiple applications at the previous round. The auctions generated a reserve fund of 240 million dollars. For the 2024 cycle, an endowment of $10 million was earmarked for projects that had to meet a number of criteria. The programme was a victim of its own success, with 247 applications received from 64 countries for a total funding that would have amounted to 83 million US dollars.

ICANN policies under the shadow of cyber security legislations and new technologies

While the EU Member States are in the process of transposing the NIS2 cyber security directive into their national legislation, and in the United States the final arbitrations are underway for the latest version of the CIRCIA (Cyber Incident Reporting for Critical Infrastructure Act), a number of related issues continue to be discussed at ICANN. One of these is access to domain name registration data for legitimate purposes. At the instigation of the GAC (Governmental Advisory Committee), which represents governments, ways of authenticating law enforcement requestors are being considered to enable them to be specifically identified so that they can be prioritised when requests for access to data are made. This future mechanism is intended above all to respond to specific cases of imminent threats linked to the exploitation of children, attacks on the integrity of individuals or critical infrastructures.

On the subject of malicious use of the DNS, almost a year after the implementation of binding measures for registry operators and registrars, ICANN’s compliance department has stated that 46 investigations are currently underway into abuse of the DNS, with mitigation measures affecting more than 5,400 domain names.

Another trend observed: the median time taken to fully remediate an abuse report is 7.5 days in the case of phishing and malware. This has fallen since the ICANN measures were introduced. Another shadow hanging over ICANN82 was the change of administration in the United States. Although it has had no impact on ICANN so far, the unpredictability of the new administration has raised a lot of questions among participants.

AI was also discussed in a specific session. As it was exposed AI technology, like Doctor Jekyll and Mr Hyde, can bring benefits when used as a resource, for example to mitigate abuse, but can also be used for malicious purposes by perpetrating increasingly sophisticated abuses. The subject of a governance framework was raised. This is a subject on which the Internet Governance Forum and the WSIS+20 global forum organised by the International Telecommunication Union and the United Nations should be working.

In conclusion, ICANN82 was marked by the curiosity aroused by the arrival on the scene of its new CEO, whose public forum at the end of the summit showed that everything he said was scrutinised and analysed. ICANN82 was a summit that did not shy away from the highly unstable technological, legislative and geopolitical context in which we find ourselves. In the face of this instability, we can offer solutions that provide security, reliability and stability. Just as we tend to say that real estate is a solid investment, the acquisition of a brand extension, a dot brand, with a view to the next round next year is also a solid investment. It allows you to become the owner of a piece of the Internet, a naming space protected from attacks, where addresses can be created that are deemed reliable, so that your targets can find you and that you can address them in complete confidence over the long term. These are times that also call for consideration of the notions of sovereignty and proximity. In this respect, Nameshield has been an independent European player for over 30 years, and the management of .brand projects is one of our areas of expertise.

ICANN81: A summit at a crossroads between challenges and difficulties 

ICANN81: A summit at a crossroads between challenges and difficulties 

Thursday 14 November saw the close of the 81st ICANN Summit, the Internet’s governing body. The summit took place on the banks of the Bosphorus between Asia and Europe, in Istanbul, Turkey. This summit is the last meeting of the global Internet community for the year 2024 before turning to 2025.

Tripti Sinha, who has just been reappointed Chair of the ICANN Board of Directors, opened her remarks at the Opening Ceremony of the 81st ICANN Summit with the observation: ‘The past year (editor’s note: 2024) has been a complicated for ICANN’.

ICANN, an organisation challenged on several fronts

Tensions between Russia, China and the West have never been so high. A geopolitical context that is putting the multipartite model of a globalised Internet under pressure, as ICANN is an organisation governed by American law, even if it claims to be apolitical. The conflict in the Middle East is never far away either. In particular, it has resurfaced at previous ICANN summits this year. Challenged about its role and legitimacy, ICANN is also faced with the change of presidency in the White House with a second term for Donald Trump, which gave rise to some unusual questions at the public forum that closed the summit. One participant referred to the unpredictability of the future President of the United States, which ‘increases the risk of conflict’, going so far as to wonder whether ‘ICANN can take control of American military systems’. While the answer to this question is, of course, no, Tripti Sinha has also raised the issue of ICANN’s liability, with legal action being taken against ICANN, and financial challenges, speaking of ‘financial difficulties’. ICANN’s operating costs have risen significantly in recent years, partly as a result of inflation. Inflation has led to significant increases in domain name prices, which in turn have led to a downturn in the market. ICANN, which derives part of its resources from domain names in return for a tax on each generic domain name, has also been affected.

A transition of presidency at the head of the organisation

Erik Lindqvist, the new President of ICANN, will officially take office on 9 December 2024.

At the opening of the summit, Erik Lindqvist, the future President of ICANN, gave a short speech to introduce himself and talk about his career. He will officially take up his new post on 9 December, taking over from Sally Costerton, who was applauded for her successful interim role.

Among the tasks expected of the new President, who will be based in Geneva, Switzerland, is a review of the organisation’s financial situation. Avenues for savings and new sources of funding were discussed, and a number of clear-cut opinions emerged. For example, should attendance at summits be made fee-paying, or should the venues chosen for these international meetings be rationalised to generate savings? The interaction of the new President with the various bodies is also expected and acclaimed. Defending the multi-stakeholder governance model in the current difficult context and ICANN’s ethical policies are two other important issues raised by the contracting parties.

New series of new generic extensions confirmed for 2026

Among the difficulties, ICANN must also succeed with the new series of new generic extensions. First of all, this means meeting the April 2026 deadline for the application window, a date that has been hammered home for several summits. Reassuringly, the recommendations of the Subsequent Procedures (Subpro) policy development process are being implemented at a good pace. The future application guide is on schedule, with a final version due to be delivered within a year. The future registry contract for new registry operators is also being considered. Unlike the candidates for the 2012 round, this new contract should be a single document covering all types of TLDs: open, community, brand and internationalised (editor’s note: in native language). It will include fourteen specifications, compared with the current thirteen, with the fourteenth covering TLD variants for multilingual TLDs.

Other issues on which ICANN reached a decision, there should be no private auctions to decide between candidates for the same TLD in 2026. Like a symbol or perhaps a marker, at the very end of the summit, the ICANN Board adopted the applicant support program for future applicants, a program that will involve a communications campaign in disadvantaged geographical areas at the beginning of 2025.

Capitalising on experience feedback

A number of issues recently initiated by ICANN are currently being evaluated. These include abuse of the domain name system. In April 2024, specific obligations came into force to compel registries and registrars to take action in the event of clear abuse. ICANN81 provided an opportunity to take stock of these measures after an initial six-month implementation phase. ICANN Compliance reports that it has initiated 363 complaints, often involving several domain names. Unsurprisingly, the most common abuses involved phishing campaigns.

Another element being tested is the Registration Data Request Service (RDRS). This is a prototype designed to gauge interest in a standardised platform for submitting and processing requests for access to domain name registration data for legitimate purposes. Over the course of a year, the RDRS collected requests for 13,000 names, a volume that remains low compared to the 170 million generic names. A related issue is the depreciation of the Whois protocol for domain name registration databases. This protocol, which has been in use since the 1980s, is due to give way to the RDAP protocol for generic domain names at the end of January 2025. ICANN Org has pointed out, however, that this new protocol is very rarely correctly deployed at this stage.

The tense international context was largely reflected at this summit on an organisation that will be starting 2025 with a new president at its head and a change of administration in the White House. ICANN has made no secret of the fact that it is facing a number of difficulties. The success of the next series of new gTLDs, a series that will have taken fourteen years to complete between 2012 and 2026, will be decisive in helping the organisation to emerge from this turbulent period. The stakes are high, firstly because ICANN is committed to holding this series in April 2026. A postponement of the date would further damage its credibility.

This series is also important given the investment required to prepare and hold it. The significantly higher application fees than in 2012, with a base amount of USD 227,000, may act as a brake. Investors, for their part, may not appreciate the abolition of private auctions to decide between applicants for the same TLD, with ICANN seeking, on the contrary, to curb speculation.  Nameshield, for its part, is convinced of the merits of this new round and, in particular, of dot brand extensions, the benefits of which will more than offset the investment required if applicants are properly accompanied. Nameshield is ready to help future project owners by providing them with a complete solution for their entire project cycle. If you have an Internet extension project, contact our experts who will be delighted to support you.

SSL/TLS certificate duration reduced to 45 days by 2027:Apple takes the first step

On October 9, Apple revealed to the CA/Browser Forum that it had posted a draft ballot for comment on GitHub regarding two important SSL/TLS certificate lifetime events:

  • Gradually reduce the maximum duration of public SSL/TLS certificates to 45 days by 2027;
     
  • Gradually reduce the reuse period for DCV challenges to 10 days by 2027.

In March 2023, in its “Moving Forward, Together” roadmap, Google announced its intention to offer the CA/B Forum a reduction on the maximum possible validity period for public TLS certificates going  from 398 days to 90 days. Since this announcement, the market has been feverishly awaiting for Google’s confirmation but most of all, for the implementation’s timetable… without success. For its part, Mozilla announced, a few weeks ago, its intention to follow Google’s lead on its Firefox browser, without adding any further detail.

Apple ultimately took the first step last week, announcing on October 9th its intention to both reduce the lifetime of certificates to 45 days (when the entire market was expecting 90 days) and to limit the duration of the DCV challenge to 10 days, according to the schedule below. A true bombshell:

Sep-15-2025 => certificates and DCV validation times reduced to 200 days

Sep-15-2026 => certificates and DCV validation times reduced to 100 days

Apr-15-2027 => certificates and DCV validation times reduced to 45 days

Sep-15-2027 => DCV Validation time: 10 days

Information on the background and analysis of this announcement, the expected outcomes and how to prepare for them will undoubtedly be useful:

Context and Analysis:

At this stage, the publication is likely to be commented by market players prior to the formal drafting of the ballot within the CA/B Forum, which itself will be voted on by its members: the Internet browser publishers on the one hand (Google, Mozilla, Apple and Microsoft…) and the Certification Authorities on the other. Amendments are bound to be made, but the general idea remains and the machine is up and running.

Indeed, software publishers are all aligned on the need to reduce the lifetime of certificates, and among Certification Authorities, Sectigo, one of the major players in the certificate industry, is already supporting the initiative. It is likely that things will move rapidly from now on, with few comments and a ballot drafted in the coming weeks or months. We will then know more about the confirmation of the durations and timetable, and will of course make sure to keep you informed.

Expected Outcomes:

  • Certificate lifetime: whether 90 days, 45 days or even less, this reduction is no longer a surprise, and will have a major impact on public certificate portfolio. The certificates can no longer be managed manually. The market has begun its transition to automation, notably through CLMs (Certificate Lifecycle Managers). The issue at stake for companies and organizations will be to rely on partners who can offer as many interconnections as possible between Organizations, Certification Authorities and CLMs.
     
  • DCV challenge duration: Reducing the duration of the DCV challenge to 10 days, if validated, would have a considerable impact, perhaps even more so than reducing the lifetime of certificates. Up until now, the industry has pre-validated domain names for 398 days, using the DCV challenge only once. Apple’s announcement would thus force the use of a DCV challenge for virtually all orders, which would be a major paradigm shift and would involve interconnections with an additional brick in the ecosystem: the DNS. The DCV (Domain Control Validation) challenge involves intervening in the zone of the domain name(s) listed in the certificate, ideally instantaneously, to validate it.
     
  • Organization authentication duration: Apple has not announced anything on the subject of the validity period of organization authentication for OV certificates, which is currently 825 days. However, rumors are circulating that this may be reduced to 398 days or even 365 days.

How to be ready:

The key to successful certificates management lies in automation. A 45 days certificate lifetime represents 9 interventions per year per certificate. Manual management thus becomes utopian. We therefore need to rely on:

  1. Certificate Provider/Certification Authority (CA): a trusted partner who will support through your organizational and domain authentication issues. Service level is key to good management. A multi-CA partner is thus recommended to limit dependence on a single CA, as in the case of Entrust’s recent setbacks. 
     
  2. Registrar / Primary DNS: mastering the primary DNS of domain names listed in certificates will become the key to delivery. Each time a certificate is issued, a TXT or CNAME will be installed on the zone(s) in question. An interconnection between the CA and the DNS is vital.
     
  3. CLM editor: the CLM’s role is to inventory the certificate portfolio, to define certificate portfolio management rules and automate the entire process of orders, from the generation of CSRs to the deployment of certificates on servers. To function properly, the CLM relies on connectors with CAs or certificate suppliers.

Getting ready thus means identifying the most suitable solution, based on these three dimensions, and undertaking this analysis to understand the impacts in terms of process, technology, and budget – in an ideal world – before the end of the first half of 2025.

Nameshield’s approach:

Nameshield holds a unique position in the market as a registrar and supplier of multi-AC certificates. For over 10 years, we have been managing the day-to-day issues associated with authenticating organizations and domains using certificates. On the one hand, we have a privileged relationship with the biggest CAs on the market (Digicert, Sectigo, GlobalSign), and on the other, we master the DNS brick for DCV validation. As a result, we can issue public certificates almost instantaneously. Last but not least, Nameshield has connectors with the major players in the CLM market, allowing you to ensure a comprehensive connection between the various components involved in certificate management. This way, we can support you in anticipating all the issues mentioned above.

SSL/TLS certificate duration reduced to 45 days by 2027:Apple takes the first step

For more information, please contact our Sales team or our Certificates team.

Nameshield will be at the 38th Annual Marques Conference – From September 24 to 27, 2024 in Stockholm

Nameshield will be at the 38th Marques Annual Conference

Join the Nameshield team at the 2024 Annual Marques Conference, taking place from September 24 to 27, 2024 at the Radisson Blu Waterfront Hotel in Stockholm.

Nameshield is an ISO27001-certified software publisher and sovereign registrar, with 30 years of experience, that protects and defends its customers’ strategic domain names against cyber threats.

We consider that protecting online brands is more crucial than ever in the face of an increasing number of infringements, including:

  • Cybersquatting, which can damage brands’ reputations and mislead customers,
  • Fraud and scams, where similar domain names are used to create fraudulent websites, counterfeiting or fake shops,
  • Customer diversion, which redirects customers to competitors or malicious sites and trigger the loss of customers’ confidence in the brand, and in turn, the loss of revenue.

Nameshield has consequently developed a Brand Safety Chain (BSC) solution in order to shield brands’ safety, integrity, reputation and revenue in the digital ecosystem, with:

  • Continuous domain name monitoring and detection of fraudulent domain names,
  • Remediation services and support on the best action plan and procedures to implement.
  • Anti fake shop solutions, including detection, analysis reports and takedowns.

Come and meet us at stand 7.

Our team of trademark and intellectual property experts will be there to answer all of your questions.

For more information, please visit the event website : 2024 Marques Annual Conference.