Cyberthreats, digital sovereignty, AI, next ICANN round: topics at the center of attention in the German-speaking market during Domain Pulse

Domain Pulse 2026

Is the next round of new Internet extensions already behind us? Not quite. Fourteen years after the 2012 window, the new window opens on April 30 and is set to close on August 12 at 11:59 p.m. UTC. This is a rare event and THE hot topic in the domain name ecosystem at the start of 2026.

At Domain Pulse, the annual event where the national registries of Germany (Denic), Austria (Nic AT), and Switzerland (Switch) meet with players in the domain name industry since 2004, this topic was mainly discussed behind the scenes. The organizers of Domain Pulse, which took place this year in the pretty town of St. Gallen in Switzerland, wanted to focus attention on cyber threats, critical infrastructure, and the role of registries. During the two-day event, the emphasis was on collaboration, early detection of attacks, and digital sovereignty.

The key role of CERTs

Among the key mechanisms of human-centered security design and collaboration, Domain Pulse has focused particular attention on CERTs.

A CERT is defined by the European Union Agency for Cybersecurity (ENISA) as a specialized cybersecurity team responsible for:

  • receiving and processing reports related to IT security incidents;
  • analyzing incidents and vulnerabilities;
  • responding to incidents by assisting victims and coordinating resolution actions;
  • providing prevention and alert services, including advice, bulletins, and threat information;
  • facilitating coordination between actors (other CERTs, authorities, national and international organizations) for a more effective response.

It was pointed out that the three registries in the DACH region (Germany, Austria, and Switzerland) have been working closely together for a long time and that two of them have a CERT. In this regard, the Switch registry, which organized this 2026 edition, is one of the pioneers, having set up a CERT as early as 1994. The Austrian registry did the same about ten years later. As for Denic, the German registry, Thomas Keller pointed out that Denic is very active in the security of the .de infrastructure and that the registry works closely with other security structures of CTI (Cyber Threats Intelligence) and initiatives.

The most common attacks on these countries

Domain Pulse also provided an opportunity to review the most common attacks on these countries.

For Germany, whose .de domain managed by Denic is the second largest country extension in the world in terms of volume with 17.6 million domain names registered at the end of 2025, ENISA noted that 23.4% of Member States’ compensation claims related to ransomware and data breaches came from Germany in 2025.

In the case of Austria, where the .at registry, Nic AT, represents approximately 1.5 million registered domain names, the CERT operated by the registry noted that phishing and domain abuse for credential harvesting, particularly via pages imitating authentic services, remains the most commonly observed threat.

Finally, in Switzerland, where the Switch registry currently has around 2.5 million domain names under the .ch extension, the Quad 9 foundation and Switch have indicated that the three main threats identified in 2025 are ransomware, malvertising (editor’s note: a technique that involves injecting malicious code into legitimate advertising banners in order to infect Internet users and redirect them to fraudulent sites or steal their data), and malware.

This situation reminds these registries that there is still much to be done to combat malicious use of the DNS.

An international context pushing European sovereignty to the forefront

The current unpredictable geopolitical context, in which threats to the technical infrastructure of states and companies are increasing, was highlighted as a cause for concern. The current context encourages us to rethink “our relationship with technology,” as researcher Daria Höhener pointed out with regard to AI, inviting the audience to rethink our role in the age of AI.

Among the challenges posed by AI, she reiterated that we must ensure that this technology serves humanity, and not the opposite, and that it is therefore necessary for humans to remain its architects rather than becoming AI agents executors, and for trust to “remain the foundation of all connections.” The EU has adopted the “AI Act,” the world’s first legislative framework harmonizing rules on AI. The latter aims to reduce Europe’s regulatory dependence by giving it global influence over how AI is developed and used. The text will be fully applicable from August 2, 2026.

Alongside this legislative arsenal, to which the NIS2 cybersecurity directive currently being transposed in the Member States could be added, the Member States are showing that they finally have a common vision for strengthening the EU’s technological autonomy, competitiveness, and resilience in the face of external dependencies. The signing of the Declaration on European Digital Sovereignty last November in Berlin is an illustration of this.

In terms of European technical solutions that reflect this raising awareness, DNS4EU, the European resolver, was in the spotlight at Domain Pulse. Launched on June 9, 2025, this “sovereign” resolver is co-financed by the EU and supported by ENISA. It is guaranteed to be GDPR-compliant with a 100% European infrastructure. It is aimed at EU decision-makers but also seeks to offer an alternative to decision-makers who are not members of the EU DNS. 
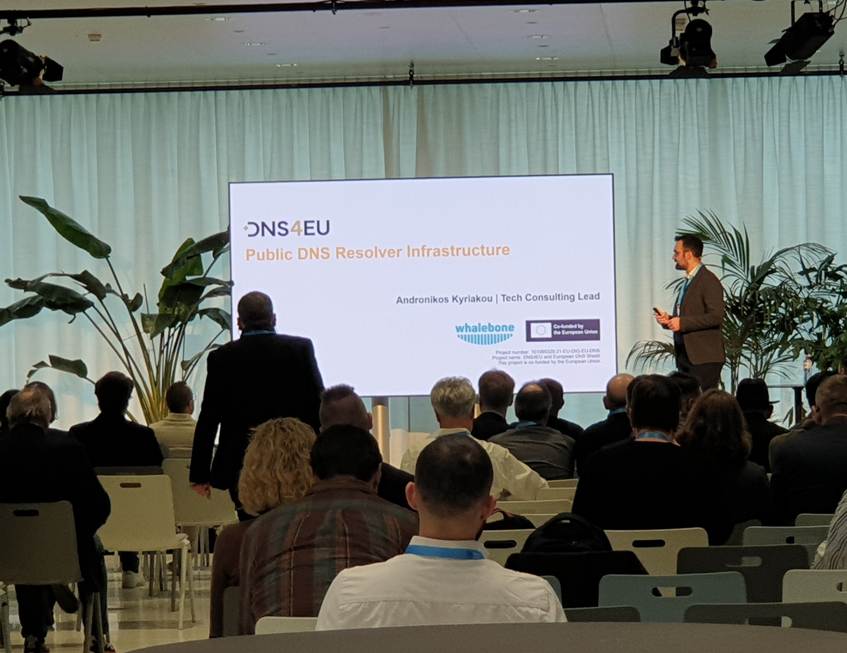
The DNS4EU initiative among the topics covered by Domain Pulse 2026

A variety of topics that reflect the diversity and richness of the information available, as well as the awareness that the Domain Pulse organizers wanted to instill in both DNS stakeholders and users. An event that reminds us that the Internet is nothing without security, and that security is nothing without collaboration and information sharing.

Nameshield, a sovereign European company, found a particular resonance between the topics covered by the Domain Pulse and its DNA, which places people at the center of its technical solutions for securing brands and DNS, and peer collaboration through its CERT. Although the next round of new extensions was less discussed, we are convinced that the new .brand TLDs that will be available to apply from April 2026 are a real opportunity for companies to equip themselves with a tool that will enhance their security, as they will have an exclusive, closed naming space that is therefore free from malicious domain names. In the context of increasing cyber threats, having a dedicated namespace that is easily identifiable and memorable for users will be a real asset. And this tool can be built with an operational sovereignty strategy with companies such as Nameshield.

The launch date for the next round of new generic extensions (.BRAND) has been announced, it will be April 30, 2026

The launch date for the next round of new generic extensions has been announced, it will be April 30, 2026

Among the unresolved questions surrounding the new application window for new generic extensions, many of us have been wondering when ICANN, the Internet’s governing body, would provide a specific date for the first day of submission of future applications.

The announcement was made public in an article published on the ICANN blog by Kurtis Linqvist, President and CEO of ICANN. He has stated that 2025 has been a year of significant progress in implementing the new generic extension program, moving toward the goal of opening a new application window, 14 years after the last one. One of the decisive steps was the publication of the applicant guide on December 16, 2025. It should be noted that the applicant guide, a reference document for future applications, was approved by the ICANN Board of Directors at the most recent public session of the ICANN84 summit in Dublin.

Kurtis Linqvist also states that efforts are now focused on the final stage of implementing the program: “We are now committed to opening the cycle on April 30, 2026.” The period for submitting complete applications will therefore begin on Thursday, April 30, and will last for 12 to 15 weeks, possibly until July or even early August. After that date, it will be too late to apply. Those who are undecided or late will have to wait for another opportunity, which could very well arise again in 14 years—who knows?

Among other notable events, at the end of 2025, the application period for candidates to apply to the Applicant Support Program ended on 19 December. This program aims to reduce economic and technical barriers to entry in order to broaden overall participation and diversity among candidates for new domain name extensions. Data provided by ICANN indicate that 75 applications were received from ICANN’s five regions:

  • 10 applications from Africa,
  • 38 from the Asia-Pacific region,
  • 1 from Latin America and the Caribbean,
  • 6 from Europe,
  • 20 from North America.

In 2012, this then new program had only received three applications. These initial indicators show that the Asia-Pacific region, which is currently the most dynamic in the domain name market, also appears to be very interested in the next series of new domain name extensions. In 2012, the 1,930 total applications submitted during the application window were distributed as follows:

  • North America: 911 applications,
  • Europe: 675 applications,
  • Asia-Pacific: 303 applications,
  • Latin America and the Caribbean: 24 applications,
  • Africa: 17 applications.

It is also estimated that around 34% of these applications were for brand extensions, or the “Brand TLDs”.

What will happen in 2026?  The answers will come next fall during ICANN’s “Reveal Day” and “String Confirmation Day”.

ICANN84: A summit to take stock six months before the opening of applications for new generic extensions

Due to instability in the Middle East, Muscat, Oman will have to wait another year to host an ICANN Summit, the Internet’s governing body. For its Annual General Meeting, ICANN played it safe by taking up residence at the prestigious Dublin Convention Center for six days of discussions, meetings, and work on policy issues. This was the organization’s last annual summit six months before the launch of the next series of new generic extensions.

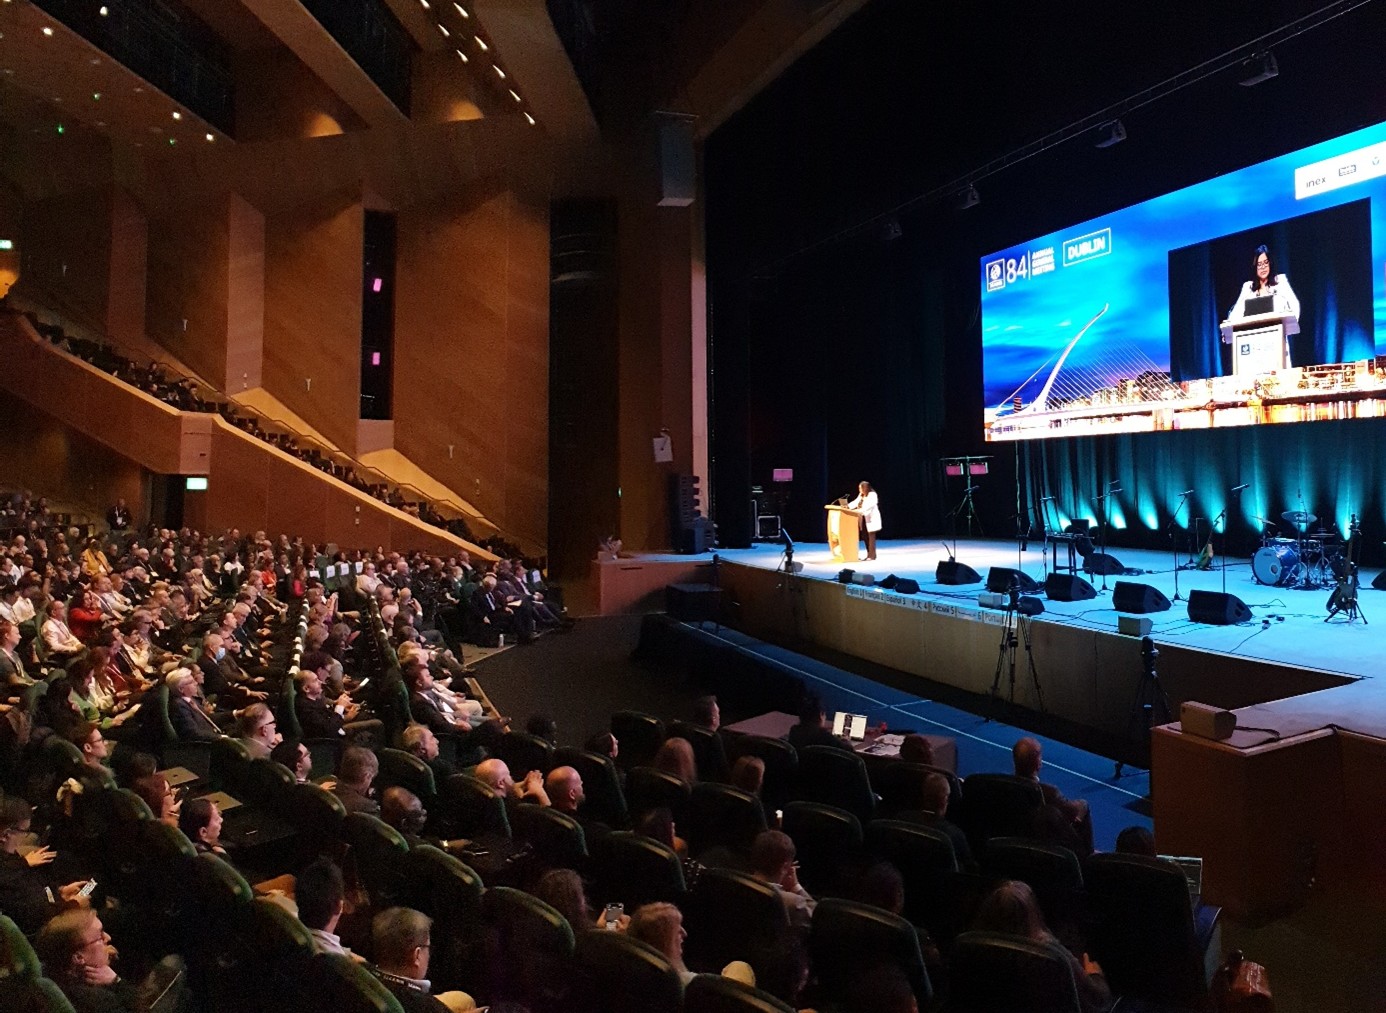
Tripti Sinha at the Welcome ceremony of ICANN84

An opening ceremony in the form of a review and a “Meitheal”

During the opening ceremony, Tripti Sinha, Chair of the ICANN Board of Directors, drew an analogy between the Irish concept of “Meitheal,” which refers to a group of people who serve the community by doing work “that no one can do alone,” and ICANN, whose mode of operation is similar. The Annual General Meeting is indeed a kind of harvest or review of results for ICANN. Among them, she cited:

– the approval of ICANN’s new strategic plan for the period 2026-2030,

– the prudent management of the organization, which has created bugetary margins,

– the ICANN Grant program, based on the 2012 auction reserve fund, with 23 projects set to receive funding,

– the launch of a holistic review of the organization,

– ICANN’s contributions to WSIS+20, the 20-year review of the World Summit on the Information Society initiated by the United Nations,

– and progress on the next round of new generic extensions, with the application window opening in just six months and the applicant support program already underway.

For Kurtis Linqvist, who is attending his third summit as ICANN CEO, “the year has been marked by complex issues such as problems affecting regional registries,” we are obviously thinking of the Afrinic regional registry “and the complexity of the world”, and even “local problems” affecting ICANN’s offices, such as the forest fires in Los Angeles during the summer and the earthquake in Istanbul, springing to mind. In this context, he welcomed the progress made on the various topics covered by ICANN. He concluded by setting out his priorities for the coming year: “listening,” “focusing on implementation” and “improving” the “way we work internally to avoid friction and slowing down implementation.” 

The difficult equation of reconciling expectations and rapid technological developments

The Geopolitical forum, which usually provides an overview of regulatory and legislative developments that may impact ICANN’s missions, focused this time on the WSIS+20. A decisive meeting will be held in mid-December in New York during the United Nations General Assembly to formalize a concluding text on the implementation of the WSIS outcomes. The session held during ICANN84 was an opportunity to advocate for an inclusive Internet and contents in users’ languages. With regard to AI the desires expressed for greater transparency on algorithms so that non-dominant languages are also taken into account, ensuring that these technologies are adapted for the widest possible audience, regardless of the language used and spoken. The widespread use of AI, particularly by the younger generation, and their appetite for centralized platforms and social networks were also raised during questions to the Board of Directors, as a reminder that the world and the uses of Internet are changing very quickly.

During the Public forum, ICANN’s role in universal acceptance was questioned, as it advocated a shift in focus toward expertise and implementation rather than awareness. The attention paid to diacritics, which are symbols that accompany a letter or grapheme to change its meaning or pronunciation, and ICANN’s lack of leadership in providing guidance on building bridges between Web 2 and Web 3 were also debatted. These multiple issues complicate the task of preventing the fragmentation of the Internet, but ICANN’s primary goal which was recalled by the Board is to “provide the best Internet space for Internet addressing.”

DNS abuse and urgent requests for access to registration data

To push for a more virtuous market, new Policy Development Processes aimed at consolidating measures already taken to combat DNS abuse have been outlined for the coming year.

On the law enforcement side, the issue of specific access to registration data continued to fuel numerous sessions. The entity representing governments, the GAC, is pushing for a delay, likely in calendar hours, to be added to domain name provider contracts.

Hot topic: the next round of new top-level domain extensions

It did not escape anyone’s notice that the hot topic at this year’s ICANN84 was the launch of a new application window for generic extensions, announced two years ago for April 2026. In fact, upon entering the Dublin Convention Center, two column trims displayed an announcement to this effect: “Ready to apply for a generic extension?” For those who had experienced the launch of the previous series in 2012, this communication seemed rather discreet.

In any case, the topic was present in a very large number of sessions. On the success side: the Applicant Support Program designed to help applicants who might not be able to apply due to financial or resource constraints. 115 applications have been received, of which 2 have been fully approved to date. The majority come from Asia, followed by North America. In 2012, while this program was new, more limited, and less widely publicized, only three applications were received by this program.

However, ICANN84 also showed that the program is experiencing delays, which were highlighted during the Public Forum. These delays include the registry services providers verification process and the provision of the registry contract for future registry operators, the final version of which may not be available until next March. 

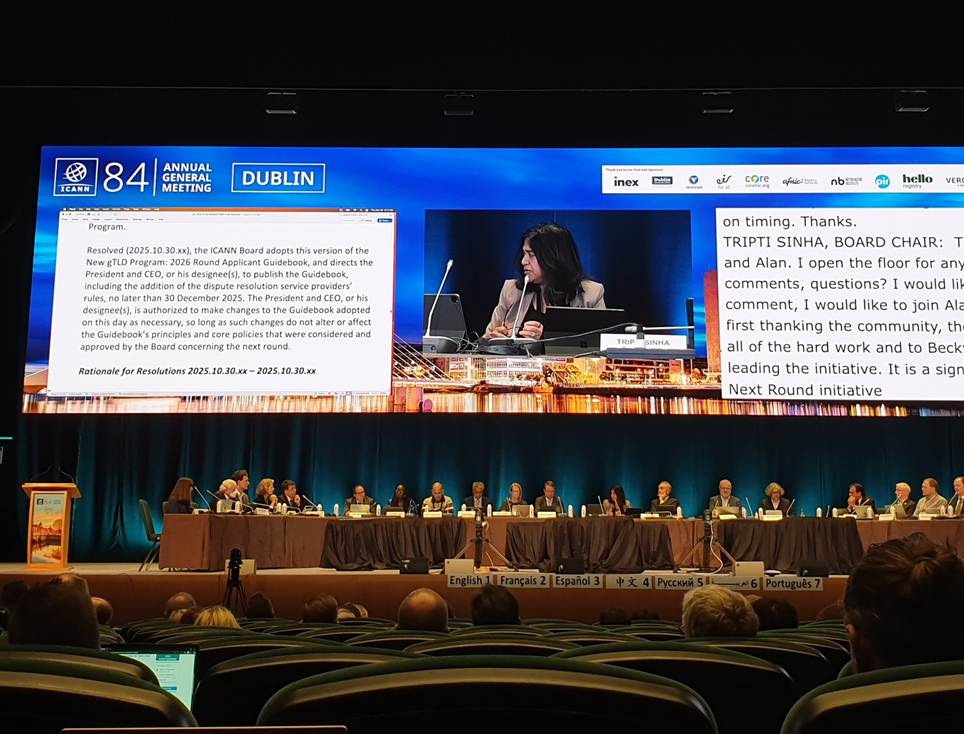
ICANN Board adopts the Application Guide Book for next round during the closing session of ICANN84

At the end of the week, however, participants welcomed the approval of the Application Guide Book during the public session held by a Board of Directors undergoing renewal. Although it is still subject to additions between now and the end of December, this essential document is now recognized as a reference. A final contribution from outgoing Board member Becky Burr reminded us that no fewer than 197 meetings were held by the implementation team to draft the nearly 400-page document, with no fewer than five phases of public comments. Also noteworthy were the departures of Maarten Botterman and Chris Chapman from the Board of Directors.

Our comment

ICANN has still not given an official date for the window for submitting applications for new generic extensions and therefore for .brand projects. It could be April 27, with a duration of 12 to 15 weeks, or perhaps longer if the issues mentioned in our article, such as the completion of the evaluation of technical operators or the publication of the final version of the registry contract, would occur too close to the opening date. In any case, ICANN has sought to reassure everyone that the April launch will go ahead. The final date for the next round should be made official in December.

As we can see, the deadline for this new opportunity is fast approaching. While it may not be obvious whether or not to take advantage of it, it is important for everyone to be aware of this new opportunity to create their own Internet extension and have a dedicated namespace, as it has not been possible since 2012. Getting started requires a well-defined project, identifying the right contacts in organizations, and anticipating the budgets to be invested. To succeed and make your project profitable, you need to choose the right partners to provide you with the support you need. Nameshield, a leading sovereign European provider, offers you expertise and tailored support throughout the entire life cycle of such a project. Let’s discuss this further together now.

ICANN83: Ten months to go until the application phase for the next round of new generic extensions

ICANN83

ICANN83, which has just taken place in the Czech capital, provided an opportunity to measure the progress made in setting up the next series of new generic top level domains, confirmed to start in April 2026. It was also an opportunity to continue the consultations begun at ICANN82 on developments to be considered to optimize the ICANN summits, and to focus attention on policy issues partly linked to the NIS2 cyber-security directive.

After registering online or on site, participants in the summits of ICANN, the Internet’s regulatory body, can view the agenda for the sessions scheduled during the summit. Prague hosted the 83rd ICANN Summit. For mid-year summits with no public forum and no opening ceremony, it’s always interesting to look at both ends of the agenda to identify the important topics of the moment.

The essential next round of new generic top level domains

It’s no surprise that participants of the first day of the summit were immersed in the Subpro process which concerns the introduction of a new round of new generic extensions promised for April 2026.

Indeed, ICANN83 was held just 10 months ahead of the next application window for all entities wishing to create their Internet extension. And this is a vital issue for the organization, firstly in financial terms, as ICANN has made major investments to strengthen and upgrade its infrastructures, and also to increase its workforce to manage the surge in activity as the window approaches. The stakes are also technical and legal, and in terms of reputation, as this process is highly engaging and impactful for all entities that will be taking the step of creating their own Internet extension in 2026.

On the implementation process and timeline, the good news is that the implementation schedule is on track. A first draft of the application guide book is open for public comments until July 23. The application submission window has been confirmed to last 12 to 15 weeks from April 2026.

If we look at the changes introduced in the next round compared to the one that took place in 2012, there is in particular the possibility of positioning oneself on a second choice of string. Once the requested strings have been revealed to the public – what ICANN refers to as the “Reveal Day” – applicants will have 14 calendar days to decide whether or not to position themselves on their second choice. This may make it possible to avoid an auction against entities that have positioned themselves on the same string. Private resolutions of disputes between candidates for the same string, authorized in 2012, will not be allowed in 2026.  This approach has been favored in order to divert the interest of entities interested in the next series for essentially speculative reasons.

The Applicant support program to help entities with funding or other resource issues is also more complete than it was in 2012, even if, as presented in Prague, there are only 22 applications in the draft stage at this stage.

ICANN also pointed out that the evaluation of technical operators has been partly automated and that, in terms of inclusiveness, more scripts will be taken into account in 2026: 33 in all. Indeed it will be possible to apply for internationalized Internet extensions, i.e. those written with diacritical characters, as required by many European languages, or characters from non-Latin scripts.

At the other end of the agenda was the future of ICANN meetings

Faced with engaging topics, the community of Internet users needs to exchange ideas and points of view and in this respect ICANN meetings are essential. Although since the covid pandemic in 2020, ICANN has opted for so-called “hybrid” formats, i.e. allowing participants to follow the sessions either face-to-face or remotely, ICANN has also had to cope with a significant increase in the costs of organizing these annual events. There are four in all, if we add a more operational summit to the three dedicated to domain name policy issues.

In Seattle, ICANN initiated a reflection on the future of these events in a community process called “How we meet”. In the equation for organizing these indispensable exchanges with the community, ICANN also indicated that it had to take into account the high demands of security, accessibility and inclusiveness.

At ICANN83, Sally Costerton, who is in charge of this topic, presented the results of a survey conducted among participants and stakeholder representatives, based on proposals for future meetings. Strongly supported proposals included prioritizing the location of meetings to venues offering economical travel deals, and establishing a policy to automatically transfer an ICANN meeting to an online format in the event of unforeseen circumstances requiring a meeting to be moved from a scheduled venue.

Still 72% in favor, the reduction by one day of the two Community Forums, which correspond to the first and third ICANN annual meetings, and the reorganization of the session agenda by moving the public forum and the forum on geopolitical aspects from the last to the first day of the Community Forum. The underlying idea here is to reduce the rental period for a plenary room to a single day instead of taking it for the whole meeting. There are no small savings.

On the other hand, the principle of converting one of the annual meetings into a purely remote format was widely rejected. The working group that has taken up this subject has recorded these elements in a report, and is now continuing its discussions with a view to reaching a decision.

The NIS2 cybersecurity directive is not far off

At the time of the ICANN83 Summit, 14 European Union countries had transposed the NIS2 cybersecurity directive into their national laws. These transpositions are of interest to ICANN, as several subjects are linked to the domain name component of the directive, as set out in Article 28.

Related topics include the accuracy of registration data, and access to domain name registration data for legitimate purposes through a Standardized System of Access to Registration Data (SSAD) outlined in 2020 with the ePDP Phase 2 policy development process. While the review of policy measures concerning the accuracy of registration data has been paused, the implementation of SSAD is still uncertain. A prototype called Registration Data Request Service (RDRS) has been tested for almost two years now, and ICANN is in the feedback stage.

The Governmental Advisory Committee, which represents governments, once again reiterated at the summit that requests for access to registration data, if urgent and linked to legal issues, must be processed within 24 hours. The new Registration Data Policy, which will come into full effect at the end of August 2025, has left this notion of timeframe somewhat vague. Behind this notion of urgent requests, it was recalled that these are requests that involve an imminent risk of threat to life, serious injury, damage to critical infrastructure or exploitation of children, in cases where disclosure of the data is necessary to combat or remedy this threat. The notion of critical infrastructure refers to physical and cyber systems considered essential by governments for the functioning of society and the economy, and deserving special protection for national security.

One of the central topics at ICANN83 was how to manage the authentication of entities that would benefit from prioritization.

Also related to NIS2 was the presentation of a study by the DNS Research Federation on the territorial impact of the NIS2 directive. The study, carried out on over 8 million domain names, shows that European registries have almost 70% of their name holders outside the EU, a proportion which drops to 29% for registrars. It also shows that for all EU-based entities, there is a large offshore customer base. This is particularly important for registries, but also for registrars and resellers. This difference is due in particular to increased market concentration.

Nameshield is historically a sovereign European corporate registrar, ISO27001 certified since 2017 and with its own CERT. Our expertise guarantees NIS2 compliance for your intangible assets.

Regarding the next series of new generic extensions arriving next year, Nameshield also reminds you that now is the time to ask yourself if you should position yourself on a .brand extension creation project. Indeed, as ICANN83 has shown with regard to the financial support scheme for applicants seeking financial support from ICANN, many entities simply don’t know whether they should participate, and if so, how they should go about it. While some will also delay in order not to reveal their intentions too early, the risk for these entities is to let the deadlines slip. Both the Applicant support program and the application window have start and end dates. The Applicant support program closes in November 2025, while the next application window should close between July and August 2026.

Let’s meet to discuss these issues together, because opportunities to create your own exclusive Internet extension based on your brand are few and far between.

It’s official: the lifespan of SSL/TLS certificates will be reduced to 47 days

It's official: the lifespan of SSL/TLS certificates will be reduced to 47 days

On 9 October 2024, Apple announced at the CA/B Forum (Certification Authority Browser Forum) its intention to reduce the maximum duration of public SSL/TLS certificates to 45 days by 2027, as well as to reduce the DCV challenge reuse period to 10 days by 2027.

This request was then discussed and amended six months later, again by Apple, which proposed a change to the initial schedule with a reduced certificate duration of 47 days for SSL/TLS certificates and a DCV challenge validation period of 10 days from 15 March 2028.

This measure officially comes into force following the CA/B Forum vote in April 2025, which adopted a new implementation schedule, officially reducing the validity of certificates to 47 days and thus promoting automation for the proper management of these certificates.

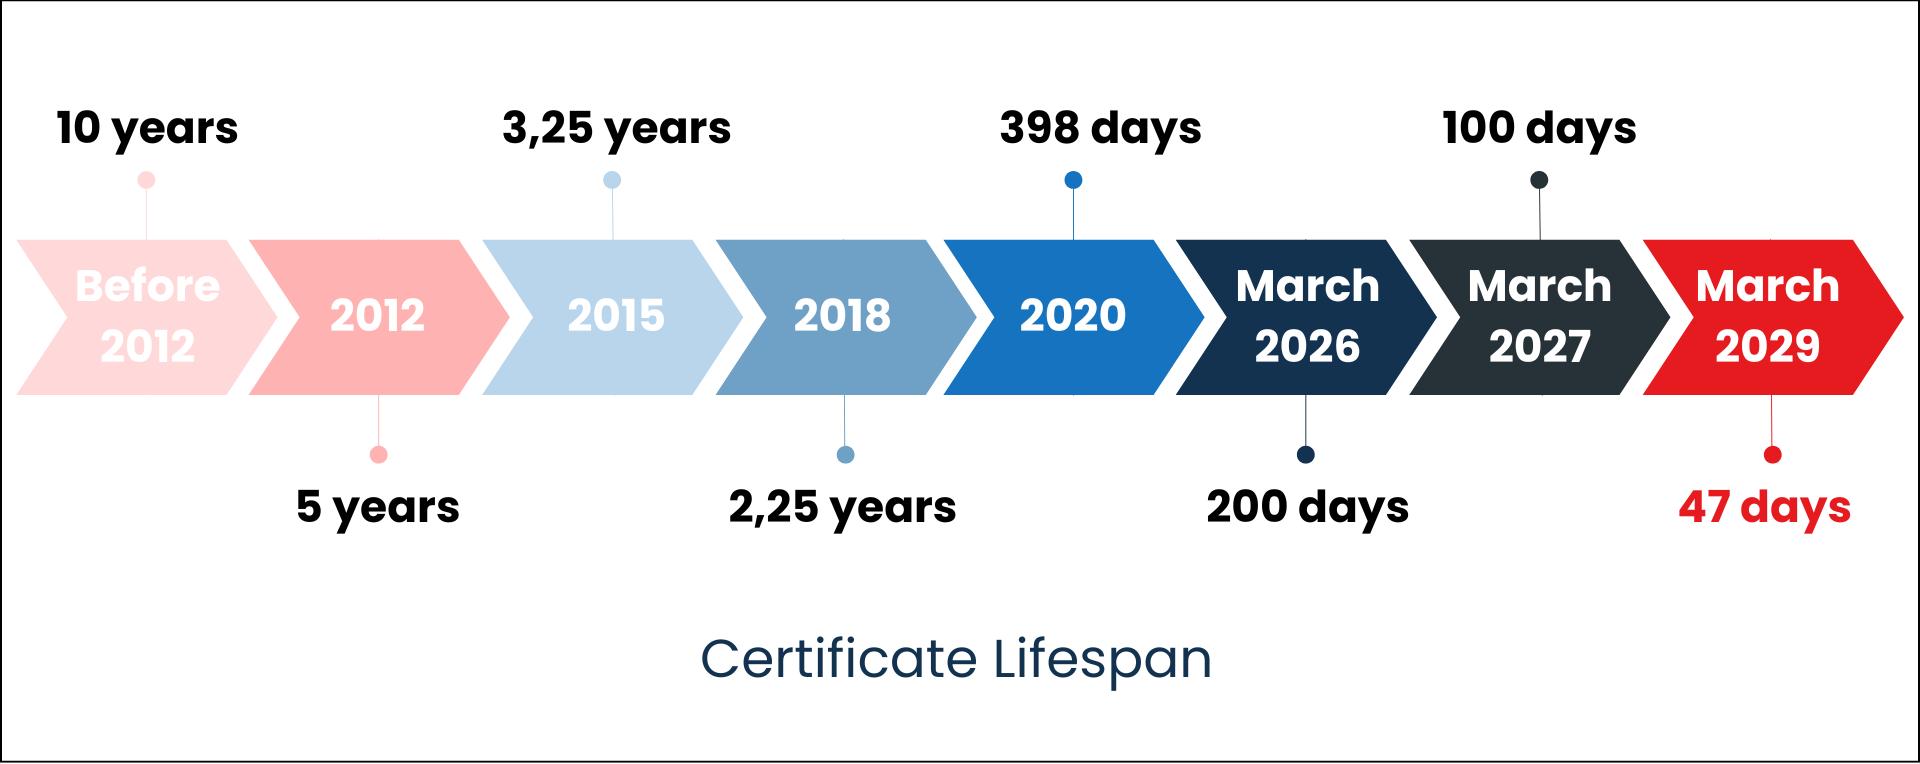
  • Until 15 March 2026, the maximum TLS certificate lifetime will remain at 398 days.
  • From 15 March 2026, the maximum TLS certificate lifetime will be 200 days.
  • From 15 March 2027, it will be reduced to 100 days.
  • And from 15 March 2029, the maximum TLS certificate lifetime will be reduced to 47 days.

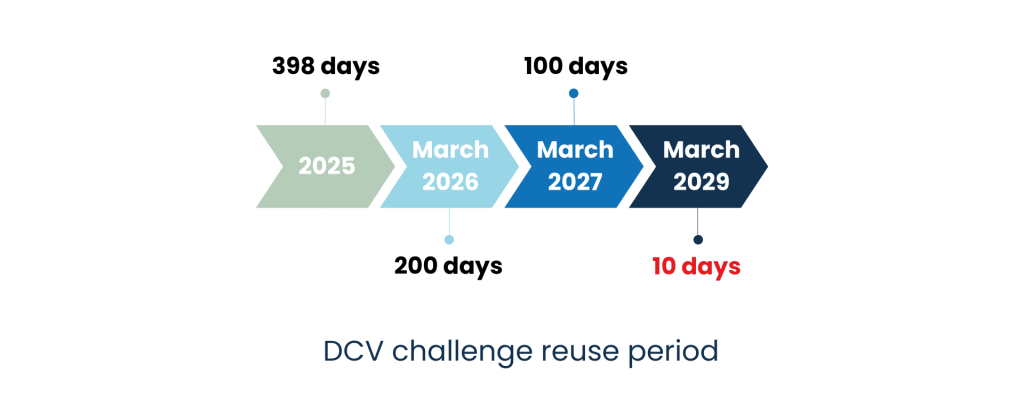
At the same time, the reuse periods for Domain Control Validation (DCV challenge), which involve intervening in the domain name zone listed in the certificate to validate it, will be aligned with the certificate schedule, reaching 10 days in 2029.

  • Until 15 March 2026, the maximum period during which domain validation information can be reused is 398 days.
  • From 15 March 2026 onwards, the maximum period during which domain validation information can be reused is 200 days.
  • From 15 March 2027 onwards, the maximum period during which domain validation information can be reused is 100 days.
  • From 15 March 2029 onwards, the maximum period during which domain validation information can be reused is 10 days.

Faced with these major changes coming in 2026, it is essential for businesses to prepare

The CA/B Forum’s initiative will gradually transform the digital certificate security landscape. The validity period of SSL/TLS certificates will be reduced, accompanied by stricter DCV challenge validation rules. The key to effective certificate management in the future will therefore lie in automation. With certificates valid for 47 days in 2029, that means nine interventions per year per certificate, making manual management unfeasible. It will therefore be necessary to rely on the following services/software:

  • Certificate provider/Certification Authority (CA): a trusted partner who will assist you with organization and domain authentication issues. The level of service is key to effective management. A multi-CA partner is recommended to limit dependence on a single CA, as demonstrated by the recent difficulties experienced by Entrust.
  • Registrar/Primary DNS: controlling the primary DNS of the domain names listed in the certificates will become key to delivery. Each certificate issue will result in the installation of a TXT or CNAME on the zone(s) concerned. Having an interconnection between the CA and the DNS is essential.
  • CLM editor: the CLM is responsible for inventorying the certificate pool, defining pool management rules, and ensuring complete automation of the ordering process, from CSR generation to certificate deployment on servers. To function, it relies on connectors with CAs or certificate providers.

Preparing therefore means identifying the solutions that suit you best in these three areas and starting to think about the impact on processes, technology and budget, so that you are ideally prepared for the first half of 2026.

Nameshield, an ally to help you manage these changes

Nameshield occupies a unique position in the market as both a registrar and a provider of multi-CA certificates. For over 10 years and on a daily basis, we have been managing all issues related to organization and domain authentication linked to certificates, thanks to our privileged relationship with the largest CAs on the market (Digicert, Sectigo, GlobalSign) and our expertise in DNS for DCV challenge validation. As a result, we issue public certificates almost instantly. Finally, regarding the CLM component, Nameshield has connectors with the largest players on the market to enable you to ensure a complete connection between the various components related to certificate management. We therefore support you in anticipating all the issues mentioned above.

If you have any further questions, you can contact Nameshield directly here.