Interview with our DMARC Consultant, Sébastien Fischer, with the CSA

A healthy mail environment doesn’t just happen on its own. It takes companies and people who are actively committed to keeping email an open, secure, and trustworthy communication channel. The Certified Senders Alliance (CSA) recognizes this commitment with its “Supporter Spotlight” series, and we are delighted to be part of it.

The Certified Senders Alliance (CSA) has been the European certification body for email senders since 2004 and, as a joint initiative of eco and DDV, acts as an intermediary between email service providers and senders. As a sponsor, together with our partner Merox, we’re contributing our DMARC expertise to the fight against phishing and identity theft.

We’re continuing this commitment beyond our sponsorship partnership: In December, we’re hosting a webinar on the topic of phishing.

Our conversation with the CSA shows just how important this topic is in practice: Sébastien Fischer, a DMARC consultant at Nameshield who has been an expert in email deliverability for 18 years, talks about his early days at Emailvision all the way to his current work with us in the field of domain security.

Here is the full interview.

CSA: What still fascinates you about email today?

To start off, let’s take a look back at his career: We wanted to know what has fascinated him about this field over the years.

SF: I took my first steps in email marketing—and specifically in the field of email deliverability—18 years ago at Emailvision. There, I discovered an incredible communication channel that is constantly evolving, which is what makes it so fascinating on so many levels:

  • Changes in marketing practices: Mass emails—which are still sent by some advertisers—have given way to more targeted emails with personalized content.
  • Changes in spam techniques: Spammers can be very skilled marketers and quickly adapt to new technologies to bypass anti-spam filters and deceive end users.
  • Advances in filtering techniques: Anti-spam filters use complex reputation systems based on various indicators, including technical configuration, authentication, historical reputation data for domains and IP addresses, content analysis, detection of suspicious behavior, and analysis of users’ email behavior.
  • Evolving standards: Over the past 20 years, numerous RFCs have been published, and some have evolved or will continue to evolve—I’m thinking in particular of DMARC and version 2 of DKIM.
  • Legal developments: The introduction of the GDPR a few years ago changed the rules of the game. All advertisers must adapt quickly to these changes if they want to continue reaching their users’ inboxes.

CSA: What is the challenge that Nameshield is particularly committed to addressing?

A key challenge for Nameshield is protecting brands from domain spoofing and phishing—through the targeted use of authentication protocols such as SPF, DKIM, and DMARC to secure companies’ digital identities.

SF: Nameshield is a global leader in domain management. It is important to us to be a one-stop shop for our customers when it comes to deploying state-of-the-art technologies to secure incoming and outgoing email traffic, while also serving as an advocate for these technologies to ensure a smooth transition for all our customers—so that this important communication channel remains as secure and reliable as possible.

CSA: What does it take to ensure that email remains a reliable channel?

SF: Email is a fantastic communication channel, but there are certain areas where it could still be significantly improved:

  • Greater security: The adoption of DMARC with a restrictive security policy remains too low—a godsend for any attacker who likes to use unprotected domains for their phishing emails.
  • More BIMI: The use of a VMC brand certificate with BIMI—to display the logo and a distinctive checkmark in the inboxes of certain providers—increases a brand’s visibility, much to the delight of marketing teams. It also lends greater legitimacy to emails sent to recipients’ inboxes, thereby helping to prevent confusion.
  • Greater cyber awareness among businesses and individuals: Recognizing phishing emails and helping to protect passwords to prevent account and data theft.

More members of the CSA (Certified Senders Alliance) and its certification program: To deliver the right message to the right person in their inbox at the right time.

CSA: Why is the CSA’s collaboration with Nameshield important to you?

SF: The CSA is a key European organization in the field of email deliverability and trust, particularly thanks to its email certification program. The CSA is not only a trusted third party for numerous local and international providers but also serves as a legal and technological authority—which gives it strong legitimacy and considerable prestige within the industry. The organization offers invaluable support to anyone looking to improve the quality of their email marketing—which is precisely why we are committed to supporting it.


Our conversation with Sébastien Fischer demonstrates once again that a secure and trustworthy email ecosystem is a collective effort. At Nameshield, we work every day—together with partners like the CSA—to further advance domain security and email deliverability.


Many thanks to the CSA for the insightful questions and the great collaboration!


Learn more about DMARC or contact us here.
Nameshield at the CSA Summit in Cologne – From April 22 to 24, 2024

Celebrate the 20th anniversary with us and be part of the discussion about the future of commercial emails.

For 20 years, the CSA (Certified Senders Alliance) has been committed to strengthening trust in email as a communication channel. Building bridges between email senders and email providers has been the central goal of the CSA from the very beginning – this year’s anniversary summit will examine the success factors of the future under the motto ‘Trust Fuels the Future’.

Nameshield is a Gold Sponsor of the event – our team would be delighted to meet you there. Gain market-leading expertise with CSA’s insights and evolving best practices. We are particularly looking forward to the discussion around the implementation of DMARC, which is becoming a new standard.

Join an international network of brands, agencies, email service providers and mailbox vendors for a dynamic exchange of information in the well-connected email ecosystem! The CSA Email Summit is not just an event, it’s your path to realising your full potential in the ever-evolving landscape of commercial email.

The CSA Email Summit is supported by various industry associations and provides a solid platform for conversations that offer valuable insights into the future of email marketing. Learn from industry experts in workshops, sessions, short talks and masterclasses to enhance your expertise.

Please contact the Nameshield team for more information and to make an appointment at the Summit!

Phishing, slamming and other fraudulent e-mails: Stay alert during the end-of-year holidays!

Phishing, slamming and other fraudulent e-mails: Stay alert during the end-of-year holidays!

The end-of-year holidays often announce the upsurge of fraudulent mass e-mails campaigns. Indeed, cybercriminals take advantage of this period, when vigilance can be particularly low, to launch phishing e-mails.

What are phishing and slamming?

Phishing is used by cybercriminals to obtain personal information in order to commit an identity theft.

In the world of phishing, slamming is a well-known variant that consists in encouraging domain names holders to renew their annuity with another registrar, by arguing the emergency and criticality of the concerned name’s loss. Concretely, this is an e-mail pushing its recipient to contract an unsolicited service and to proceed to the payment of this latter without delay.

Thus, the slamming may take the form of a fraudulent renewal invoice, usually associated with intimidating terms like “Expiration notice”. Under the pressure of such e-mail, generally well built, it happens that the recipient then proceeds to the payment and finds himself debited with an important amount for the so-called renewal.

In the same way, the slamming e-mail may also indicate that a “customer” of the sender, posing as a fake registrar, intends to register domain names identical or similar to your brand. Then the fraudster proposes to register them for you in order to protect you from these troublesome registrations, of course, in exchange for an urgent payment.

Another kind of attack, the suspicious e-mail attachment!

Be careful of fraudulent e-mails with infectious attachments: a single entry point is enough to destroy a network!

The aim of a trap and thus malicious attachment is to pose as a legitimate file (PDF, Word document, JPG image…), while hosting and hiding a malicious code: this is what we generally call Trojans.

Some simple rules to protect against them

  • Always stay alert when someone asks you your personal data;
  • Do not ever open an attachment from an unknown sender, or from one who is not entirely trustworthy;
  • Check the links by hovering the cursor over them (without clicking) to ensure that they link to trustworthy websites;
  • Never reply under the pressure of this kind of solicitation and of course do not proceed to any payment;
  • If there is any doubt, do not reply to the e-mail and contact the sender through another method who will confirm whether it really is a fraud attempt or not.

To remind you of this more often, you can find a wallpaper to download on the Nameshield website:

New e-mails authentication requirements from Google and Yahoo

New e-mails authentication requirements from Google and Yahoo - DMARC

Google and Yahoo recently announced significant changes to their e-mails authentication requirements. The aim of these adjustments is to strengthen the security of online communications, a major issue in the current context of cybercrime.

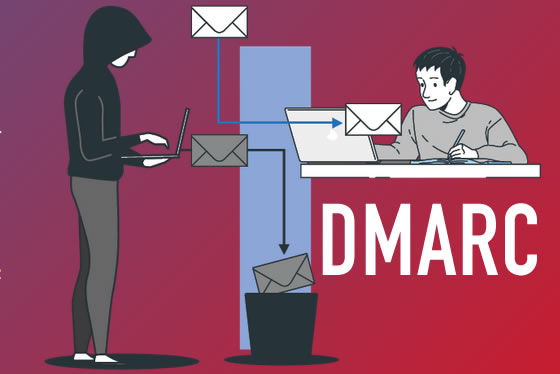
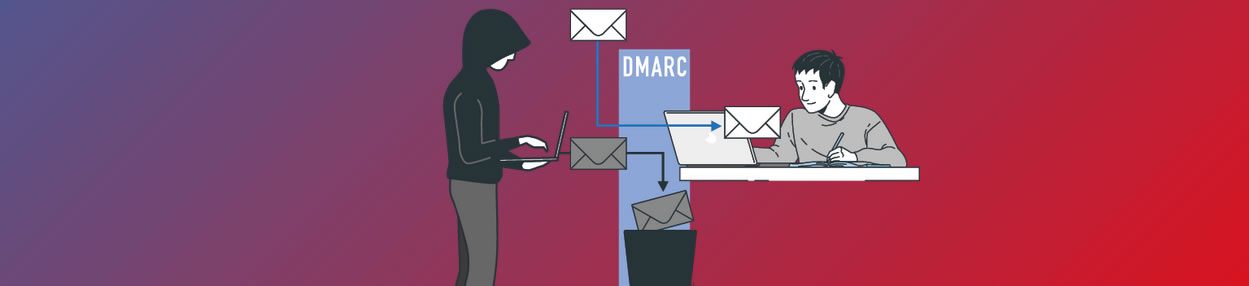
The two giants are emphasizing the adoption of advanced authentication protocols, in particular DMARC (Domain-based Message Authentication, Reporting, and Conformance). DMARC relies on the existing SPF and DKIM standards, providing a robust method for verifying e-mails’ authenticity and reducing the risk of identity theft and phishing.

To implement these new requirements, Google and Yahoo will adjust their algorithms to give priority to e-mails from domains that have correctly implemented DMARC. The aim of this measure is to improve the deliverability of authenticated e-mails, reinforcing users’ trust in the security of their e-mail inboxes.

The new guidelines will apply from February 1, 2024 to all senders who send more than 5,000 emails per day. They underline Google and Yahoo’s commitment to fight against online threats, in particular phishing, a common method used by cybercriminals to deceive users and gain access to their sensitive information. By adopting stricter e-mails authentication requirements, these companies are strengthening users’ protection against malicious attacks.

It is now essential for domains holders and players in the digital world to comply with these new guidelines, in order to contribute to the creation of a safer and more secure Internet for all.

Nameshield’s experts are at your disposal to assist you in deploying this protocol.

Phishing, slamming and other fraudulent e-mails: stay alert during the summer holidays!

Phishing, slamming and other fraudulent e-mails: stay alert during the summer holidays!

Every year, the summer holidays announce the upsurge of fraudulent e-mails mass campaigns. Indeed, cybercriminals try to profit from these periods when the vigilance is sometimes lowering, to launch phishing e-mails.

What are phishing and slamming?

Phishing is used by cybercriminals to obtain personal information in order to commit an identity theft.

In the world of phishing, slamming is a well-known variant that consists in encouraging domain names owners to renew their annuity with another registrar, by arguing the emergency and criticality of the concerned name’s loss. Concretely, this is an e-mail pushing its recipient to contract an unsolicited service and to proceed to the payment of this latter without delay.

Thus, the slamming can take the form of a fraudulent renewal bill, generally associated with intimidating terms like “Expiration notice”. Under the pressure of such e-mail, in general well built, it happens that the recipient then proceeds to the payment and is debited of an important amount for the so-called renewal.

In the same way, the slamming e-mail indicates that a “customer” of the sender posing as a fake registrar, wants to register domain names identical or similar to your brand. Then the fraudster proposes to register them for you in order to protect you from these troublesome registrations, of course, in exchange for an urgent payment.

Another kind of attack, the suspicious e-mail attachment!

Be careful of fraudulent e-mails with infectious attachments: a single entry point is enough to destroy a network!

The aim of a trap and thus malicious attachment is to pose as a legitimate file (PDF, Word document, JPG image…), while hosting and hiding a malicious code: this is what we generally call Trojans.

Some simple rules to protect against them

  • Always stay alert when someone asks you your personal data;
  • Do not ever open an attachment from an unknown sender, or from one who is not entirely trustworthy;
  • Check the links by hovering the cursor over them (without clicking) to ensure that they link to trustworthy websites;
  • Never reply under the pressure of this kind of solicitation and of course do not proceed to any payment;
  • If there is any doubt, do not reply to the e-mail and contact the sender through another method who will confirm whether it really is a fraud attempt or not.

Find on the Nameshield’s website a wallpaper to download to help you think about it more often.