Phishing, slamming and other fraudulent e-mails: Stay alert during the end-of-year holidays!

Phishing, slamming and other fraudulent e-mails: Stay alert during the end-of-year holidays!

The end-of-year holidays often announce the upsurge of fraudulent mass e-mails campaigns. Indeed, cybercriminals take advantage of this period, when vigilance can be particularly low, to launch phishing e-mails.

What are phishing and slamming?

Phishing is used by cybercriminals to obtain personal information in order to commit an identity theft.

In the world of phishing, slamming is a well-known variant that consists in encouraging domain names holders to renew their annuity with another registrar, by arguing the emergency and criticality of the concerned name’s loss. Concretely, this is an e-mail pushing its recipient to contract an unsolicited service and to proceed to the payment of this latter without delay.

Thus, the slamming may take the form of a fraudulent renewal invoice, usually associated with intimidating terms like “Expiration notice”. Under the pressure of such e-mail, generally well built, it happens that the recipient then proceeds to the payment and finds himself debited with an important amount for the so-called renewal.

In the same way, the slamming e-mail may also indicate that a “customer” of the sender, posing as a fake registrar, intends to register domain names identical or similar to your brand. Then the fraudster proposes to register them for you in order to protect you from these troublesome registrations, of course, in exchange for an urgent payment.

Another kind of attack, the suspicious e-mail attachment!

Be careful of fraudulent e-mails with infectious attachments: a single entry point is enough to destroy a network!

The aim of a trap and thus malicious attachment is to pose as a legitimate file (PDF, Word document, JPG image…), while hosting and hiding a malicious code: this is what we generally call Trojans.

Some simple rules to protect against them

  • Always stay alert when someone asks you your personal data;
  • Do not ever open an attachment from an unknown sender, or from one who is not entirely trustworthy;
  • Check the links by hovering the cursor over them (without clicking) to ensure that they link to trustworthy websites;
  • Never reply under the pressure of this kind of solicitation and of course do not proceed to any payment;
  • If there is any doubt, do not reply to the e-mail and contact the sender through another method who will confirm whether it really is a fraud attempt or not.

To remind you of this more often, you can find a wallpaper to download on the Nameshield website:

New e-mails authentication requirements from Google and Yahoo

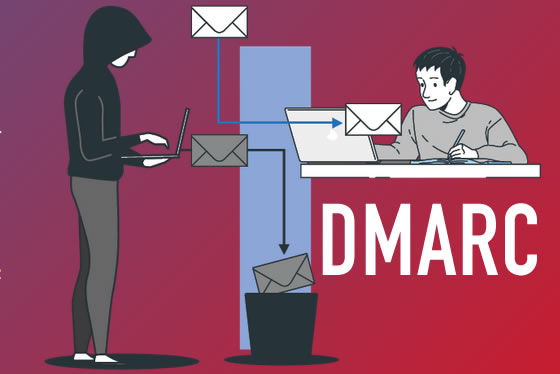
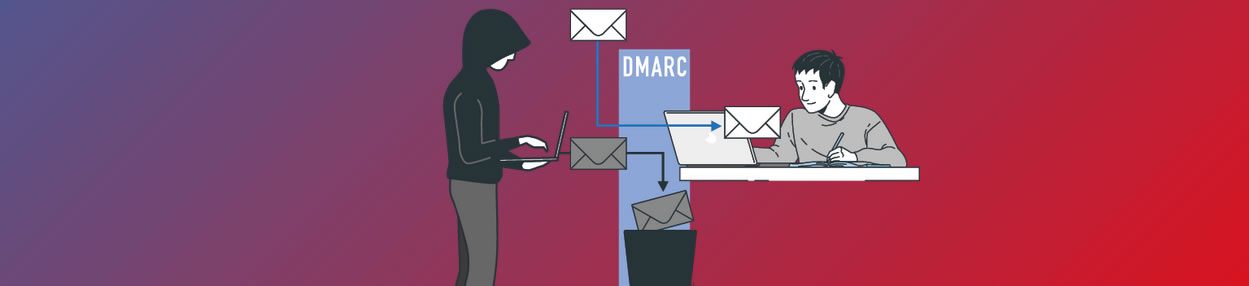
New e-mails authentication requirements from Google and Yahoo - DMARC

Google and Yahoo recently announced significant changes to their e-mails authentication requirements. The aim of these adjustments is to strengthen the security of online communications, a major issue in the current context of cybercrime.

The two giants are emphasizing the adoption of advanced authentication protocols, in particular DMARC (Domain-based Message Authentication, Reporting, and Conformance). DMARC relies on the existing SPF and DKIM standards, providing a robust method for verifying e-mails’ authenticity and reducing the risk of identity theft and phishing.

To implement these new requirements, Google and Yahoo will adjust their algorithms to give priority to e-mails from domains that have correctly implemented DMARC. The aim of this measure is to improve the deliverability of authenticated e-mails, reinforcing users’ trust in the security of their e-mail inboxes.

The new guidelines will apply from February 1, 2024 to all senders who send more than 5,000 emails per day. They underline Google and Yahoo’s commitment to fight against online threats, in particular phishing, a common method used by cybercriminals to deceive users and gain access to their sensitive information. By adopting stricter e-mails authentication requirements, these companies are strengthening users’ protection against malicious attacks.

It is now essential for domains holders and players in the digital world to comply with these new guidelines, in order to contribute to the creation of a safer and more secure Internet for all.

Nameshield’s experts are at your disposal to assist you in deploying this protocol.

Meet Nameshield on the it-sa from 10th to 12th October 2023 in Nuremberg, Germany

Meet Nameshield from 10th to 12th October in Nuremberg at a new edition of the it-sa, the absolutely must-attend meeting of the IT security sector!

As the “Home of IT Security“, it-sa stands for both a comprehensive range of information and networking and knowledge exchange on the topics of data protection and IT security.

The three-day programme includes talks, workshops, discussion panels, one-to-one meetings and opportunities for networking…

Meet us on site: Hall 7, Stand 7-214, in cooperation with eco, the Association of the Internet Industry.

Exchange with our team and discover our global solutions that satisfy the requirements of your DNS security. Discover our product for a high-availability of your strategic domains: “DNS Bastion“.

For more information, visit the event website: https://www.itsa365.de/

Nameshield’s DNS Premium labelled France Cybersecurity

The digital transformation of companies creates an increasing dependence on networks.

Websites, emails, VPN, applications… these company key services must remain accessible. An interruption would be dramatic.

DNS is the access point to all these services. It translates domain names into IP addresses and routes traffic to these services. It is increasingly exposed to attacks, yet remains poorly secured due to a lack of knowledge. With the increase in threats, maintaining its DNS infrastructure is becoming more and more complex.

Securing strategic domain names by hosting them on highly secure DNS offering permanent availability, to avoid any interruption to company key services, has become a necessity.

Nameshield, certified ISO 27001 on all its registrar activities, protects companies’ critical digital services against cyber threats, and proposes a DNS Premium solution that ensures high availability of online services.

Nameshield’s DNS Premium has been labelled France Cybersecurity since 2018. This label is a guarantee for users that Nameshield’s products and services present a level of quality in cybersecurity verified by an independent jury.

“Cybersecurity is at the heart of Nameshield’s DNA, through its CERT and ISO 27001 certification. In a sector dominated by American players, this label is the perfect way to highlight our sovereign solutions such as DNS Premium“, Christophe Gérard, Nameshield’s Products Director.

Phishing, slamming and other fraudulent e-mails: stay alert during the summer holidays!

Phishing, slamming and other fraudulent e-mails: stay alert during the summer holidays!

Every year, the summer holidays announce the upsurge of fraudulent e-mails mass campaigns. Indeed, cybercriminals try to profit from these periods when the vigilance is sometimes lowering, to launch phishing e-mails.

What are phishing and slamming?

Phishing is used by cybercriminals to obtain personal information in order to commit an identity theft.

In the world of phishing, slamming is a well-known variant that consists in encouraging domain names owners to renew their annuity with another registrar, by arguing the emergency and criticality of the concerned name’s loss. Concretely, this is an e-mail pushing its recipient to contract an unsolicited service and to proceed to the payment of this latter without delay.

Thus, the slamming can take the form of a fraudulent renewal bill, generally associated with intimidating terms like “Expiration notice”. Under the pressure of such e-mail, in general well built, it happens that the recipient then proceeds to the payment and is debited of an important amount for the so-called renewal.

In the same way, the slamming e-mail indicates that a “customer” of the sender posing as a fake registrar, wants to register domain names identical or similar to your brand. Then the fraudster proposes to register them for you in order to protect you from these troublesome registrations, of course, in exchange for an urgent payment.

Another kind of attack, the suspicious e-mail attachment!

Be careful of fraudulent e-mails with infectious attachments: a single entry point is enough to destroy a network!

The aim of a trap and thus malicious attachment is to pose as a legitimate file (PDF, Word document, JPG image…), while hosting and hiding a malicious code: this is what we generally call Trojans.

Some simple rules to protect against them

  • Always stay alert when someone asks you your personal data;
  • Do not ever open an attachment from an unknown sender, or from one who is not entirely trustworthy;
  • Check the links by hovering the cursor over them (without clicking) to ensure that they link to trustworthy websites;
  • Never reply under the pressure of this kind of solicitation and of course do not proceed to any payment;
  • If there is any doubt, do not reply to the e-mail and contact the sender through another method who will confirm whether it really is a fraud attempt or not.

Find on the Nameshield’s website a wallpaper to download to help you think about it more often.