New e-mails authentication requirements from Google and Yahoo

New e-mails authentication requirements from Google and Yahoo - DMARC

Google and Yahoo recently announced significant changes to their e-mails authentication requirements. The aim of these adjustments is to strengthen the security of online communications, a major issue in the current context of cybercrime.

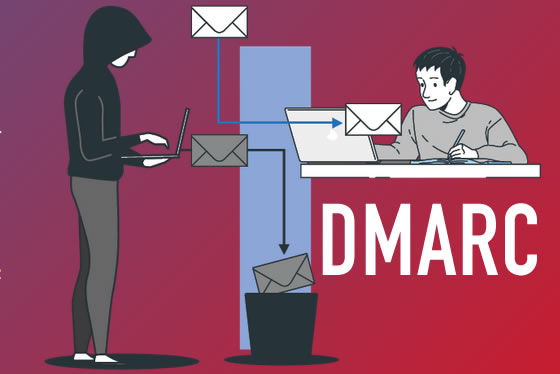
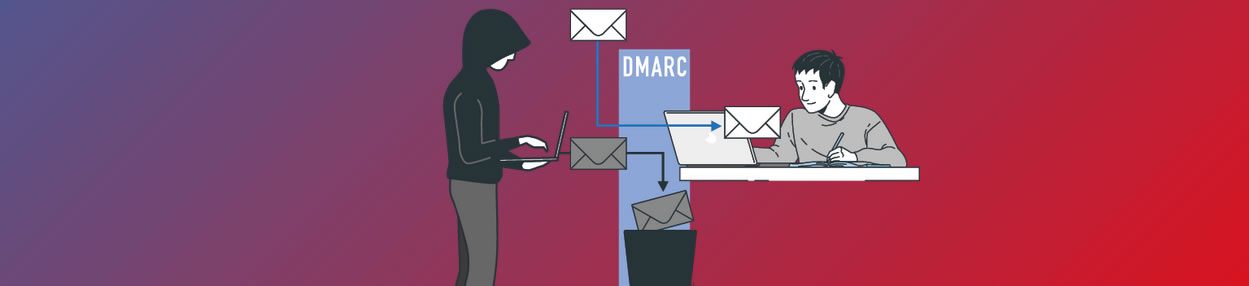
The two giants are emphasizing the adoption of advanced authentication protocols, in particular DMARC (Domain-based Message Authentication, Reporting, and Conformance). DMARC relies on the existing SPF and DKIM standards, providing a robust method for verifying e-mails’ authenticity and reducing the risk of identity theft and phishing.

To implement these new requirements, Google and Yahoo will adjust their algorithms to give priority to e-mails from domains that have correctly implemented DMARC. The aim of this measure is to improve the deliverability of authenticated e-mails, reinforcing users’ trust in the security of their e-mail inboxes.

The new guidelines will apply from February 1, 2024 to all senders who send more than 5,000 emails per day. They underline Google and Yahoo’s commitment to fight against online threats, in particular phishing, a common method used by cybercriminals to deceive users and gain access to their sensitive information. By adopting stricter e-mails authentication requirements, these companies are strengthening users’ protection against malicious attacks.

It is now essential for domains holders and players in the digital world to comply with these new guidelines, in order to contribute to the creation of a safer and more secure Internet for all.

Nameshield’s experts are at your disposal to assist you in deploying this protocol.
New document: 5 minutes to understand the SYRELI procedure

5 minutes to understand - Domain names - SYRELI procedure - Nameshield

Placed under the aegis of AFNIC (French Association for Internet Naming in Cooperation), the SYRELI procedure allows to sanction obvious and indisputable infringements of a trademarks right resulting from the registration by third parties of identical or similar domain names.

Find in this “5 minutes to understand” document, available for download on Nameshield’s website, in which cases the SYRELI procedure applies and what are the rules and conditions to respect.

New document: 5 minutes to understand UDRP procedure

5 minutes to understand - Domain names - UDRP procedure - Nameshield

Established on ICANN’s proposal, the UDRP (Uniform Domain-Name Dispute Resolution Policy) extra-judicial procedure allows to sanction obvious and indisputable infringements of a trademark right resulting from the registration of identical or similar domain names by third parties, a practice commonly referred as “cybersquatting “.


UDRP applies not only to generic extensions (gTLDs) in .aero, .biz, .com, .coop, .info, .jobs, .mobi, .museum, .name, .net, .org, .pro, .travel and new extensions (new gTLDs), but also to country code extensions (ccTLDs) of which the registry has accepted the UDRP principles.

New document : 5 minutes to understand SSL / TLS certificates

5 minutes to understand - SSL/TLS certificates - Nameshield

An SSL (Secure Socket Layer) or TLS (Transport Layer Security) certificate is a digital certificate that authenticates a server (most often a web server) and encrypts the data exchanged with it. The data is thus exchanged in confidence between two actors whose identity is known. The data exchanged cannot be spied on or altered by a third party: confidentiality and integrity.

Download this document “5 minutes to understand: SSL / TLS certificates” on Nameshield’s website.