Voice.com domain name sold for $30 million

Voice.com domain name sold for $30 million
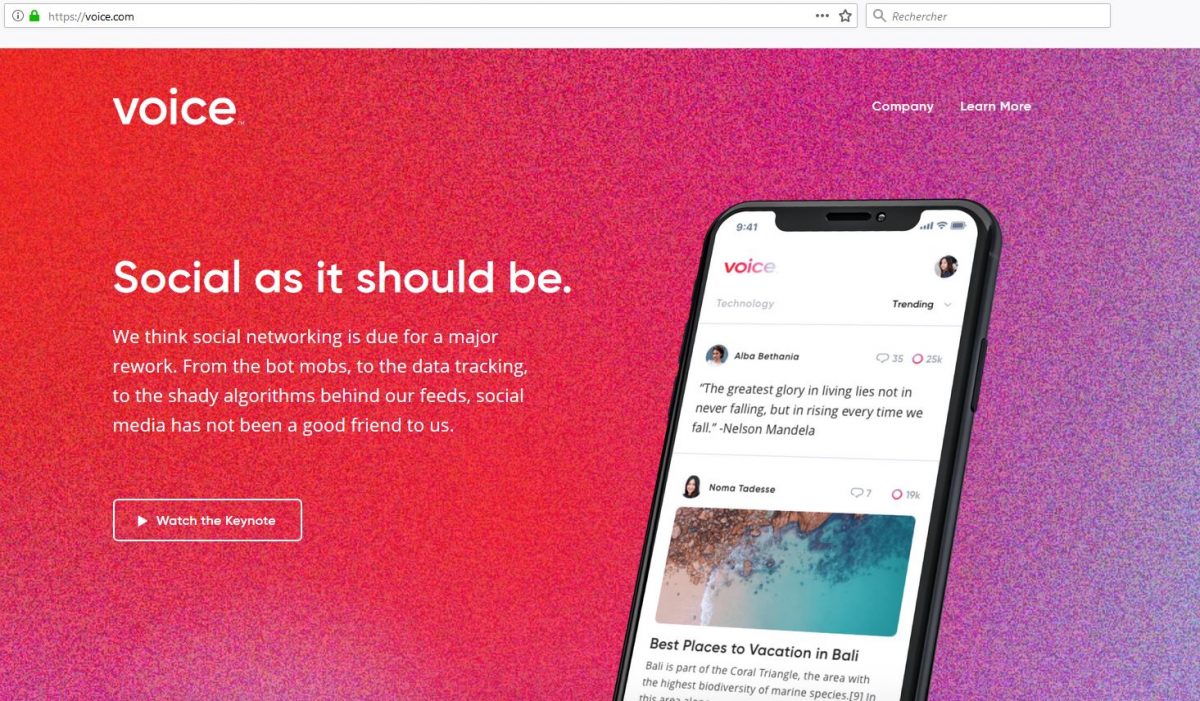
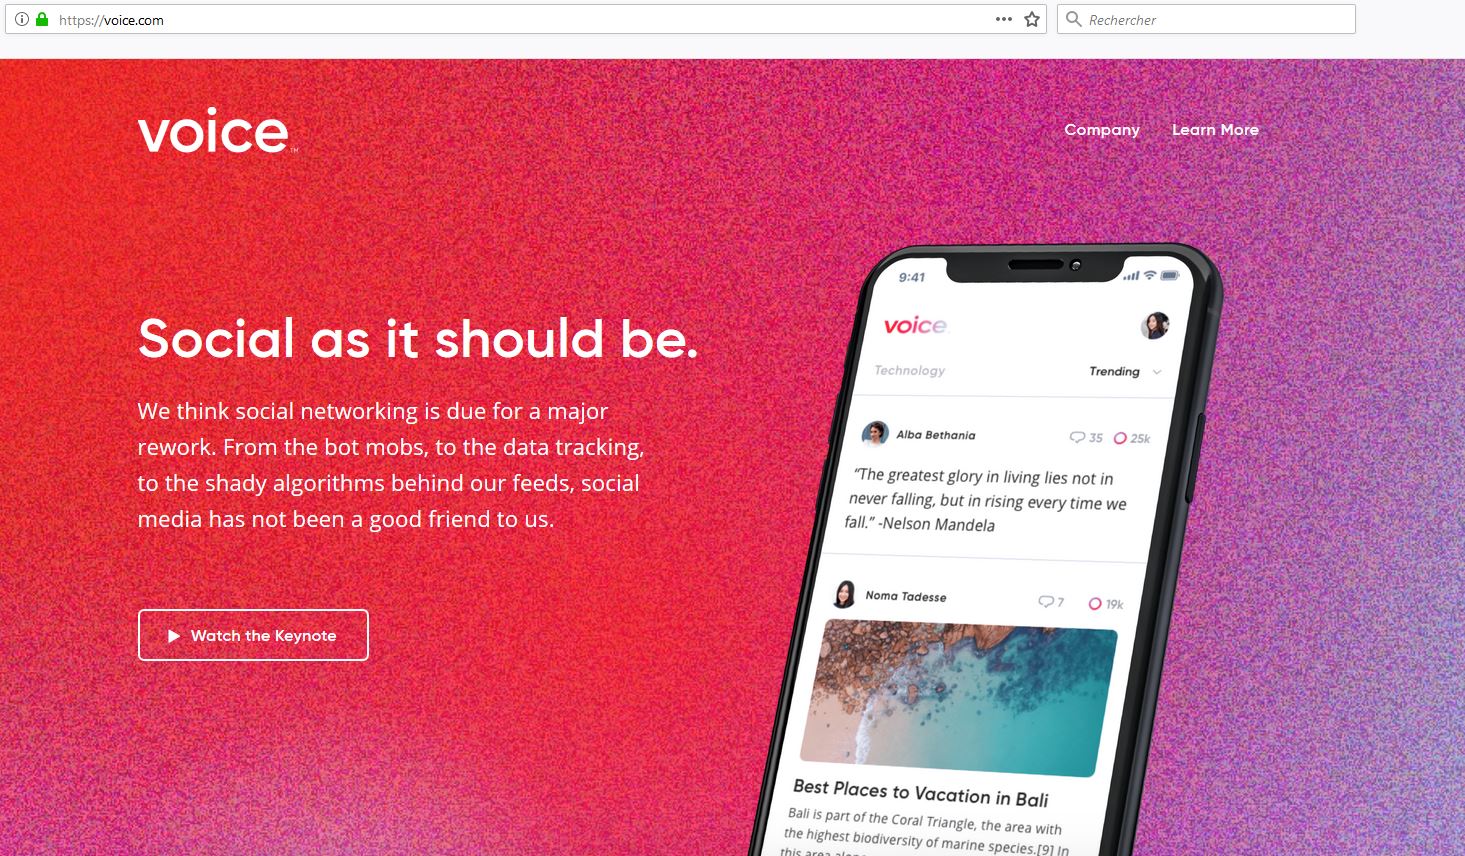
Voice.com website

Block.one (EOS), the startup behind the EOS cryptocurrency acquires the voice.com domain name for the amount of $30 million.

This is how the Chief Marketing Officer of MicroStrategy explains this acquiring at a high price: “Block.one has made a smart strategic decision in choosing Voice.com to be the internet domain name for its new social media platform. The word “voice” is simple and universally understood. It’s also ubiquitous ― as a search term […]. An ultra-premium domain name like Voice.com can help a company achieve instant brand recognition, ignite a business, and massively accelerate value creation”.

It places this sale in the top 5 of the biggest domain names’ sales:

Lasvegas.com $90 million in 2005.

CarInsurance.com $49.7 million in 2010.

Insurance.com $35.6 million in 2010.

PrivateJet.com $30.18 million in 2012.

Voice.com $30 million in 2019.

After having raised more than $4 billion through a fundraising in cryptocurrencies (ICO), the startup Block.one plans to use the domain name with the aim to compete with the social media platform Facebook.

The social media platform VOICE is opened since June, 1st 2019.

At a keynote, EOS’ CEO Brendan Blumer and Dan Larimer Block.one’s CTO, presented VOICE as an absolute alternative to everything that represents Facebook.

“Our content. Our data. Our attention. These are all incredibly valuable things. But right now, it’s the platform, not the user that reaps the reward. By design, they run by auctioning our information to advertisers, pocketing the profit, and flooding our feeds with hidden agendas dictated by the highest bidder. Voice changes that.”

In order to differentiate from Facebook, VOICE will function on the following basis:

  • VOICE will operate on EOS blockchain, which is upgrading to a faster version 2 for the occasion;
  • An anti-bot policy and other trolls will be implemented, without more details disclosed on the technology approach;
  • The blockchain will be public;
  • The arbiter of what must be seen or not, will not be the algorithm but the consensus;
  • Regarding security, a partnership with Yubico, makers of the Yubikey was announced. EOS seems to aim for an integration with WebAuthn, a standard for authentication without password recently approved by the W3C.

In other words, EOS wants to propose a model opposite to Facebook: the control by everyone of their personal data and their possible monetization.
NBA: Phishing doesn’t spare sports institutions

NBA: Phishing doesn’t spare sports institutions
Image source: mohamed_hassan via Pixabay

On last May 10th, in a press release, the Pacers Sports & Entertainment (PSE) organization, owner of the NBA’s basketball team the Indiana Pacers, revealed that they were the victim of a sophisticated phishing attack at the end of 2018.

For reminder, phishing is a technique used to obtain personal information in order to commit an identity theft.  This is a «social engineering» technique, i.e. consisting in exploiting not an IT flaw but a «human flaw» by deceiving web users through an e-mail seemingly coming from a trustworthy company, typically a bank or a business website.

Pacers Sports & Entertainment victim of a phishing attack

At the end of 2018, the company PSE has then been the target of a phishing emails campaign resulting in the unauthorized access to emails containing personal information related to a limited number of individuals.

This cyberattack affected a limited number of individuals but the amount of the stolen information is important: name, address, date of birth, passport number, driver’s license, state identification number, account number, credit/debit card number, digital signature, username and password and for some individuals, the Social Security number.

The American company has quickly implemented measures to secure the affected email accounts and investigate the incident with the assistance of forensic experts. This investigation then revealed that the hackers had access to the accounts of a limited number of persons between October 15th and December 4th, 2018. The press release doesn’t give any details regarding the identity of the targeted persons.

PSE individually notified each victim whose information has been stolen and assures that “to date, PSE has no evidence of actual or attempted misuse of any personal information”. The organization offered to the victims of the cyberattack an access to credit monitoring and identity protection services at no cost.

Some simple rules against phishing

Phishing attacks are increasing. Above all, they are becoming more and more sophisticated, and target all kinds of industries. Each and every one of us must be extra vigilant.

Lastly, for reminder, here are some simple rules to protect yourself against phishing attempts:

  • Do not reply when someone asks for your personal data by email;
  • Do not ever open an attachment from an unknown sender, or from one who is not entirely trustworthy;
  • Check the links by hovering the cursor over them (without clicking) to ensure that they link to trustworthy websites;
  • Do not trust the name of the mail’s sender. If there is any doubt, contact the sender through another method.

The Nameshield SSL interface has had a complete makeover

The Nameshield SSL interface has had a complete makeover

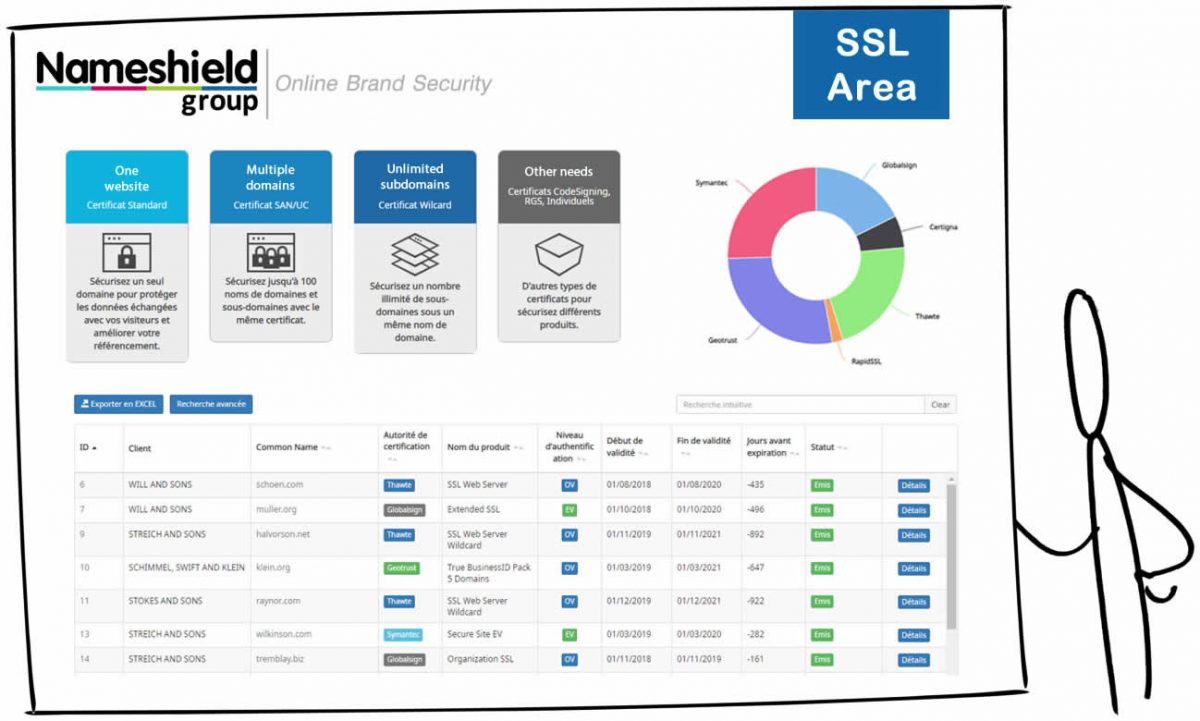
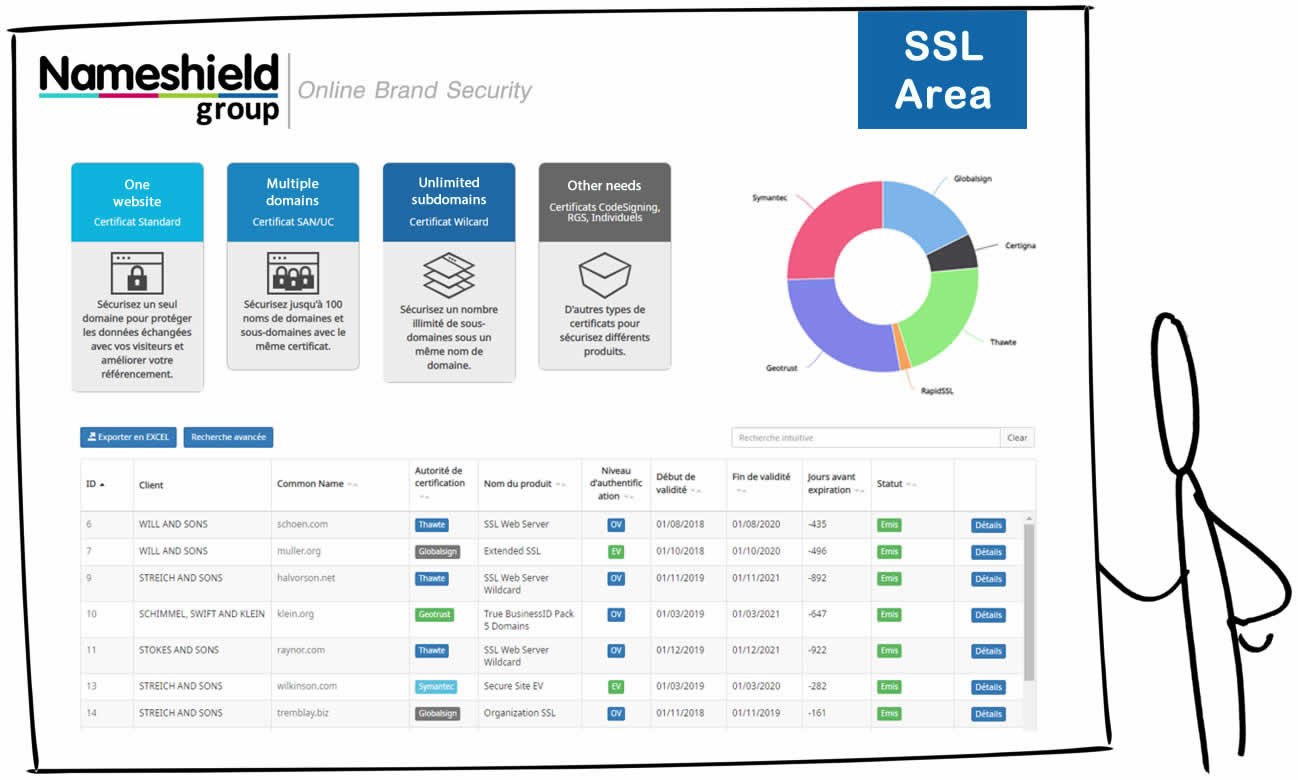
More user-friendly, more comprehensive, more attractive… our brand new and improved Nameshield SSL interface is being launched on Thursday, June 13th allowing you to manage all of your certificates.

You will now have access to key metrics on your certificate portfolio, to different certificate lookup views (such as complete portfolio, detailed overview, certificates nearing expiry, pending orders, expired or revoked certificates), to an Organization and Contact management tool and a redesigned ordering system.

Lastly, a decision support tool has been included in the interface to help you choose the certificate that’s right for your needs.

The certificate range has been updated to cover all types of certificates, SSL, RGS, Code Signing, Individual certificates and with all levels of authentication.

The SSL team remains at your disposal for a demonstration and a complete user guide is available covering all possible operations and actions.

Contact us directly at certificates@nameshield.net.

Europe decides to apply sanctions to transboundary cybercriminals

Europe decides to apply sanctions to transboundary cybercriminals
Image source: GregMontani via Pixabay

On Friday May 17th, 2019, the Council of Ministers of the European Union presented the creation of a blacklist identifying the perpetrators of cybercrimes located outside the EU.

Thus this is a new legal context which has been validated by the EU in order to try to reduce the continuously growing cyberattacks’ number. Now, the EU will indeed be able to sanction individuals or entities involved in the cyberattacks carried out from outside the EU.

Europe seeks through this measure to protect as far as possible the most critical infrastructures, regarding electoral or health systems for example, from cybercriminals, by abolishing the impunity which the international hackers seemingly enjoyed.

If there is no name on this famous list today, the situation could change soon.

Recently, the British Foreign Secretary, Jeremy Hunt declared that “for too long now, hostile actors have been threatening the EU’s security through disrupting critical infrastructure, attempting to undermine democracy and stealing commercial secrets and money running to billions of Euros. Hence, this decision was necessary.”

It’s now very clear that the cyberattacks carried out by nations, against nations or entities, tend to multiply. It’s important to note that these sanctions can be retroactive. To this day, the sanctions are not clearly defined: travel bans and assets freeze against those we know have been responsible for these actions? Several options are presently being studied.

Cyberattack: G7 and France organize a cyberattack simulation in the finance industry

Cyberattack: G7 and France organize a cyberattack simulation in the finance industry
Image source : TheDigitalArtist via Pixabay

Faced with the upsurge and the continually increasing strength of cyberattacks, a simulation exercise of a cyberattack in the finance industry will be organized by the members of the G7, the world’s major economic powers.

In the French presidency context, France will be the one that will run this test in which 24 financial authorities of the 7 members of the G7 will participate during 3 days.

Today it is no secret that the banking sector is one of the most targeted by cybercriminals [according to an IBM’s research, 19% of the attacks would aim banking institutions].

Thus, for the first time, the G7 countries organize a cyberattack cross-border simulation in early June 2019. This test is organized by the Banque de France (the central bank of France) and proposes the following scenario: a malware will be injected in a technical component widely used in the financial sector.

As indicated by Bruno Le Maire, the Minister of Economy and Finance of France “cyber threats are the proof that we need more multilateralism and cooperation between our countries”.

According to this argument, this same exercise will be conducted at the same time in the other countries, giving it a specific dimension. If other exercises of this kind have indeed already been done before, particularly by the Bank of England and the European Central Bank, none of these tests was done simultaneously.

What are the results sought in this joint exercise? Firmly establishing the risks of a cyberattack’s epidemic spread, in order to be able to enhance the infrastructures security and to ensure the reactivity in case of attack and prevent a wide contagion.