Recently, some Amazon users have been the victims of a quite sophisticated phishing attack.
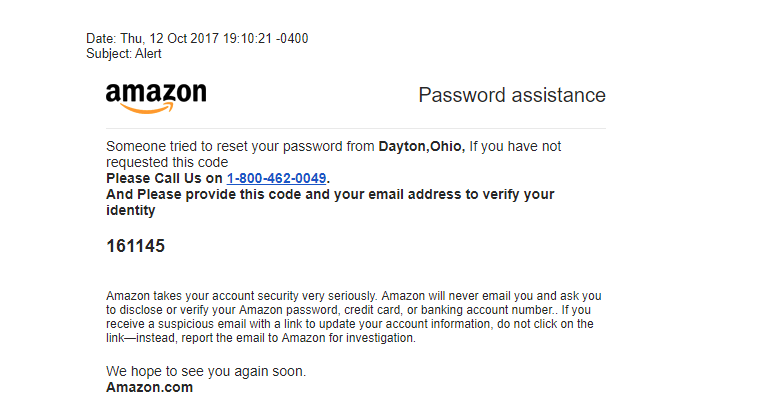
They received a fake e-mail from Amazon, alerting them that someone attempted to connect to their account by trying to change their password. A six digit code was transmitted with the instruction to call a number to verify the user’s identity. If the web users were not the source of these actions, they were invited to follow a specific procedure to secure their account. When they called the supposed Amazon number, they were directed to a Customers service department, located abroad. During the call, they had to go on a website and communicate the code to ensure the security of the account.
The copy of the phishing message:
Fortunately, many web users have detected this phishing attack and didn’t fall into the trap. But for the others, were they victims of a malware or a data theft?
All web users are hit by these phishing attempts. They are part of our daily lives, but many brands raise awareness among their customers against these actions (mostly the banking industry which is the privileged target of hackers).
The case of Ethereum foundation and the «.ETH » extension.
Ethereum is a foundation created during 2015, by Vitalik Buterin, a 21 years old Canadian. This foundation aims to promote the Ethereum blockchain technology, created by this young computer engineer, who proposes in addition to a virtual currency, like the Bitcoin blockchain, the possibility to create applications ensuring traceability, inviolability and sustainability of the transactions they manage. To allow to the greatest number of people to access to these applications, the Ethereum foundation has recently presented the ENS for «Ethereum Name Service», and its corollary, the «.ETH» extension.
Thus, if we take the example of the Bitcoin blockchain, the purpose was to create a virtual currency. The major interest consists in the absence of any central regulatory body, since it is controlled and managed by the community members, in a fully decentralized way. Any transaction done on the blockchain leads to an inscription in a block, published on a registry shared between the members. The transactions’ inscription in a block is carried out by « miners », who check, register and secure the transactions in the blockchain. This database hence lists all the transactions in blocks, creating a blocks chain supposed to be immutable and inviolable, due to the use of electronic signatures, and redistributed on the network, since it is decentralized.
Ethereum blockchain also has its currency, namely the Ether. But unlike Bitcoin, Ethereum didn’t create a virtual currency but has extended the use of the blockchain to other applications: the «smart contracts». Thus, Ether must not be considered as a currency but rather as a consumable allowing to exchange on the blockchain, use the applications it hosts.
The « smart contracts » concept
Ethereum proposes many possibilities of decentralized applications usable on its blockchain. These smart contracts are defined by the Blockchain France website as being « autonomous programs, which once started, automatically execute predefined conditions. They operate as any conditional instruction of « if – then » type (if such condition is verified, then such consequence is executed) ».
Concretely, this is a decentralized application, developed according to the Ethereum programming language (the Solidity), which automatically executes predefined instructions, on the conditions that the requirements are met, without the assistance of a third party, and ensuring that no modification is possible. These programs are executed on the Ethereum blockchain and controlled and certified by its members.
Thus, the promise is to delete intermediaries thanks to the total decentralization, managed by the processes automation.
For example, among possible applications, Ethereum foundation has announced on May 4th 2017, the creation of Ethereum Name Service, allowing domain names registration using «.ETH » extension.
Names’ registration in «.ETH »
The Ethereum Name Service, or ENS, corresponds to the Internet DNS, managed by ICANN, but unlike the latter, ENS is not based on root servers, but on the multitude of servers/machines, members of the Ethereum blockchain.
This is not a new registry having created another extension, but rather an alternative notion of the Internet.
Indeed, ENS is neither attached to the Global DNS, or to the IANA organization, nor to ICANN. ENS is a naming system specific to the Ethereum blockchain.
Domain name registration using «.ETH » is operating in a different way than classic domain name registration. This is a bidding system by anonymous deposit of a number of Ethers. In short, the name request opens a 72 hours period allowing other persons to bid. A second period of 48 hours then opens, during this period, each bidder must disclose their bid. The best bidder wins the name registration and is refund of their bid, minus the value corresponding to the difference of amounts between the two best bids. These funds are kept in a contract during 1 year minimum and can be removed at the end of this period, subject to release the name. If the name is the subject of one bid only, the bid’s winner is refund of the invested Ethers, except 0.01 Ether, corresponding to the minimum bid. This system should allow according to the ENS developers to prevent from speculation on domain names registration.
The system then doesn’t need an authority like ICANN, since the names ‘attribution is automated thanks to an IT program distributed and secured on the blockchain.
Nevertheless, if you type a domain name in «.ETH » in your browser search field, like Google Chrome, or Mozilla Firefox, an error page will be displayed. Indeed, the registered names in «.ETH » are not recognized by these browsers, since they aren’t part of the DNS network, they aren’t recognized as a domain name. Google Chrome extensions are proposed to create a bridge between the « web Ethereum » and the Internet that we know.
Hence, essentially, names currently registered in «.ETH » are only usable on the Ethereum blockchain, and therefore don’t affect the general public.
Lastly, the first use of ENS is, like the DNS, to allow the user to read and remember more easily an address by giving it a meaning. The DNS allows to translate an IP address in a legible address via the domain name.
Thus, ENS allows to translate an Ethereum user’s address (a user portfolio) of type «f14955b6f701a4bfd422dcc324cf1f4b5a466265 » in « myfirstname.eth ».
For example, when a user wishes to send Ether to another user, they only have to know their domain name and not their user address anymore. These domain names have a quite limited use, but may thereafter be used to access to future Ethereum applications.
The risks of the «.ETH » for brands owners
To this day, current web browsers don’t support these extensions, it seems that brands owners have no need to worry.
However, many French and international brands are « cybersquatted ». I.e. Ethereum users have won bids on brands names like « samsung.eth » or « volkswagen.eth ». They take over the name’s ownership for one year.
At the end of this first year of registration, the owners may release these names to retrieve the Ether stock associated to the name.
Risks should not be excluded in a near future if the «.ETH » are led to become more common and to offer interesting uses for the general public. Under this hypothesis, current web browsers could natively integrate «.ETH », in the same way as «.COM » or «.XYZ ».
Therefore, the owners of «.ETH » taking registered trademarks, for example may seek to benefit from this registration by using the reputation or identity of these protected brands, in order to divert the traffic to their own products or services. It may also be competitors seeking to tarnish their competitor’s brand image.
In the ICANN system, the rules enacted, in particular with UDRP procedures, propose to overcome these risks afterwards by allowing brands owners to try to recover a domain name using unjustly their brand. The restrictive nature of these rules, accepted and respected by registration offices, facilitates the application of the decision of Arbitration Center experts, and thus a domain name transfer to their rightful owner.
In the ENS system, there is no central authority which could enact these rules. Furthermore, domain names in «.ETH » have no real Whois file. To register such a domain name, they need to have Ethers and to create a portfolio. The identity is concealed behind a characters sequence, i.e. the digital impression of a cryptographic key. Therefore, it seems difficult to know the real identity of an owner in «.ETH ».
Furthermore, unlike the current system, it seems difficult to justify a territorial competence for «.ETH». The blockchain is not linked to any territory, it is distributed on all its members ‘machines, and thus all around the world.
The solution could eventually be developed by the Ethereum users themselves. It’s not to be excluded that an application is created in order to check the legitimacy of a domain name owner, on the basis of criteria defined in a program, like for example, the risk of confusion regarding a preexisting brand, and the good faith criteria in the use made of them. The constitution of a «popular jury » with voting materials would allow to decide on the issue as the result of a complaint from another member.
The American telecommunication company, Sorenson Communication, has forgotten to renew a domain name for only a few days in June 2016. The decision has fallen at the end of September 2017, Sorenson Communication has to pay a fine of 3 million dollars. Why such a high amount?
The domain name which has fallen back into public domain was carrying a critical service for some users! It was the “Video Relay System” which telecommunication companies must provide to deaf people and persons with vocal disabilities, so they can make video calls and contact the 911 USA emergency number, by using sign language. Utah residents with these disabilities were unable to reach 911 for 3 days!
Sorenson Communication indeed realized rather late its omission and ended up renewing the domain name only 3 days later.
But this kind of omission can be easily prevented, thanks to the “automatic renewal” option for all your domain names portfolio. Your critical domain names, carrying services, website and/or mailboxes, will not be interrupted by a simple renewal omission.
On the fine of $3 million, 252 000$ are transferred to “The Federal Communication Commission” and $2.7 million to the company of “Telecommunications Relay Services Fund”, which has found a temporary solution to rent its bandwidth during these 3 sensitive days.
October 3rd, 2017, Equifax’s ex CEO, Rick Smith, had to explain to the American Congress how the private data of almost one out of two Americans could be hacked.
March 9th, 2017: An Apache Struts flaw is detected. Less than a week after, the security patch is validated and planned, but the latter is not applied on all the servers.
March 15th, 2017: a scan is carried out but no vulnerability is detected.
April 2017: Hackers take advantage of this breach (the security patch which was not applied on all the servers) and steal the precious data.
July 31th, 2017: The ex CEO is informed of the information theft.
September 8th, 2017: Official communication on the hacking.
How can the ISO 27001 certification and the establishment of an associated ISMS (Information Security Management System) help to prevent this kind of incident?
The ISO 27001 standard is the reference regarding validation and constant improvement of an ISMS. It relies on 114 control points which scan all the domains for the establishment of an ISMS, including the implementation of procedures and the platforms update processes.
That includes the implementation and regular control of the risks management process aiming to ensure the data security. The main purpose of this management system is to carry out the appropriate measures in order to reduce, even eliminate threats impact on users or customers.
The ISMS is a wheel of constant improvement and in the case of Equifax, the processes of control established and tracked with an ISMS could have eventually helped to prevent this kind of incident.
This case demonstrates again the obligation to rethink the security strategy within companies and to implement necessary protocols to ensure the discovery of possible security flaws and the corrective action to apply.
Or how to benefit from it to implement a certification strategy specific to your company?
In January 2013, a new type of DNS Resource Record has appeared to improve the control chain in the SSL certificates issuing. This record, called CAA for Certificate Authority Authorization, allows to specify for a given domain name which Certification Authorities are authorized to issue certificates.
It’s an extremely interesting creation, in particular for big companies and groups, which technical teams are scattered in the World and for which it’s often difficult to require a global certification strategy. It’s not unusual for companies to accidentally discover the existence of certificates requested by teams not knowing the processes, by external consultants, issued by Certification Authorities with a bad image, or for certificates of low level of authentication (DV). The implementation of CAA record on your domain names is a good solution to control what the teams are doing and the news on SSL’s world will help you do that.
Indeed, if the CAA has been detailed in the RFC-6844 from 2013, it was not mandatory until today, for a Certification Authority to check if it was authorized or not to issue a certificate on a given domain name, hence a certain uselessness of this and a very low adoption.
September 8th, 2017 – The CAA checking becomes mandatory
We had to wait until March 2017, and a positive vote of the CAB/forum (ballot 187) to make this verification mandatory. Since the 8 September, the Certification Authorities have the duty to do this verification at the risk of sanctions from CAB/forum and browsers, the recent news regarding Google and Symantec has shown us how it’s not in their interests.
Three scenarios occur during this verification on a given domain name:
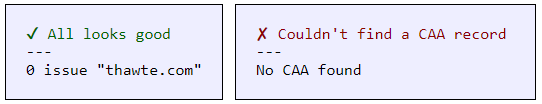
A CAA record is set and indicates the Certification Authority name, this one can issue the certificate.
A CAA record is set and indicates a Certification Authority’s name different, this one CANNOT issue the certificate.
No CAA record is set, any Certification Authority can issue a SSL certificate.
It’s important to note that for a given domain name, many CAA records can be declared. A simple tool (among many others) to test your domain name, is available online: https://caatest.co.uk/
How to benefit from CAA for my company?
If it’s not already done, the establishment of the CAA checking is the opportunity for your company to define a certification strategy and to be able to ensure that it is complied with.
Define one (or multiple) Certification Authority corresponding to your values and to your expectations in term of service quality is a first step.
It will require to put around the table the marketing stakeholders to validate the impact on websites display and the technical services to ensure of the chosen provider’s quality. It will then be necessary to declare these CAA records in the different zones of your domain names.
It’s then important to communicate with all the operational staff so they become aware of the rules imposed within the company, in order not to block them in obtaining a certificate.
Indeed, Nameshield’s experience shows that SSL certificates are often requested in a hurry; moreover the browser’s last versions are not kind towards certificates’ errors by ostensibly displaying “not secure”. In consequence, blocking the issuing of a certificate because the communication didn’t get through can be damaging.
Such strategy presents real advantages in the control of certificates, in marketing, technical, risks control and costs associated to certificates. It’s necessary to conduct it with full knowledge and in order to do it, our SSL experts’ team can assist you.
Nameshield uses cookies
Nameshield wishes to use cookies to ensure the proper functioning of the site and, with our partners, to measure its audience🍪.
Nameshield wishes to use cookies to ensure the proper performance of the website and, with our partners, to monitor its audience. More information in our Cookie Policy 🍪.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-advertisement
1 year
Set by the GDPR Cookie Consent plugin, this cookie is used to record the user consent for the cookies in the "Advertisement" category .
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
CookieLawInfoConsent
1 year
Records the default button state of the corresponding category & the status of CCPA. It works only in coordination with the primary cookie.
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Cookie
Duration
Description
_ga
2 years
The _ga cookie, installed by Google Analytics, calculates visitor, session and campaign data and also keeps track of site usage for the site's analytics report. The cookie stores information anonymously and assigns a randomly generated number to recognize unique visitors.
_gat_gtag_UA_25904574_14
1 minute
Set by Google to distinguish users.
_gid
1 day
Installed by Google Analytics, _gid cookie stores information on how visitors use a website, while also creating an analytics report of the website's performance. Some of the data that are collected include the number of visitors, their source, and the pages they visit anonymously.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Cookie
Duration
Description
NID
6 months
NID cookie, set by Google, is used for advertising purposes; to limit the number of times the user sees an ad, to mute unwanted ads, and to measure the effectiveness of ads.