Slamming: a scam still too common

Slamming: a scam still too common

The slamming is a fraud aiming to deceive companies in order to sell by emails unsolicited services for domain names.

These slamming attempts are easily recognizable and play on their contacts lack of knowledge in some cases. The slammers propose services that you didn’t solicit with your official registrar (registration, whois’update, owner or registrar transfer…) at high prices. These emails are sources of anxiety and lead you to take a quick decision.

For example, a standard slamming email would encourage you to register domain names in emergency because a third party would have done a domain names’ registration request using exactly your company name or your lead product, identically (as if by chance). They recommend you to register them without delay to prevent any cybersquatting. Obviously, the “fake registrar”, in its great magnanimity has put on standby the domain name registration order for the good of the company…

Warning, the slammer uses visual references and the right technical vocabulary, misleading that way the company. They can also make reference or put the logo of some registries or actors of the Internet environment in order to give credibility to their speech.

What to do if you have any doubts?

Forward your emails to Nameshield, which will confirm you if these mails are fraudulent.

We recommend a management of your domain names centralized and managed by a person informed of the operations associated to domain names. Don’t take any decision in a hurry. You can also make a whois to verify the sender’s identity and the existence of the “registrar” company. You will then notice that most of the domain names used for slamming campaigns have been recently registered and that the companies holding the names are unrelated to the registration office activity.

Be careful, your domain names are intangible assets to protect, secure and value.

Nameshield assists you on a daily basis, in the management of your domain names portfolio, your digital brands protection and the risks management on the web.
A bad phishing story

A bad phishing story

A victim of phishing from 2015, asked her bank for a refund of 3300€, which was the amount diverted by a fraud author. However, during the legal procedure, the Justice has cancelled the judgement of the local court of October 2017, which has requested to the bank of the victim to refund the corresponding amounts of the phishing operation.

The reason of this cancellation? The victim has deliberately communicated some confidential data regarding her credit card, by falling into the trap of a phishing email (the scammer has posed as the telephone operator of the victim).

This cancellation argument argues that indeed, the mail didn’t have any recipient nor sender name and that the reject or unpaid mention was inexact. Also the victim could have prevented the trap set and not communicate her banking information. Therefore, it was her responsibility, which indeed cancels the request for the stolen money refund by the bank.

The majority of phishing websites use domain names associated to an existing activity or referring to an activity, with the aim to deceive users, by inviting them to click on the links of legitimate websites. It allows to increase the likelihood of the attackers’ success.

The phishing concept is to retrieve personal data on Internet via identity theft, adapted to digital support.

If it is true that fraudulent payment online is directly caused by the victim’s negligence, yet, she didn’t communicate neither her credit card confidential code, nor the 6 digit 3D SECURE code, which was sent to her by SMS to validate the payment. The victim has blocked her credit card the same day, after the reception of two 3D secure messages.

However, in this case, the bank affirms that regularly, it has raised its customers ‘awareness and communicated with them, in order to alert them of phishing risks and warn them to never communicate their confidential banking data.

Thus, the Court of Cassation has judged that the victim acted carelessly and could have prevented to fall into the trap of the fraudster.

Cyber threats heavily rely on web users’ bad practices, as the SANS Institute confirms. The threats the most frequently encountered in companies are phishing (72% of the respondents), spywares (50%) and ransomwares (49%).

According to the American company Webroot, about 1.385.000 unique phishing websites are created each month, with an impressive peak of 2.3 million during May 2017.

Be aware that these phishing websites stay active during a very short period: between 4 and 8 hours maximum, to prevent to be followed or blacklisted.

Of course, this case reminds that vigilance remains crucial more than ever!

A phishing attack more and more sophisticated

A phishing attack more and more sophisticated

Recently, some Amazon users have been the victims of a quite sophisticated phishing attack.

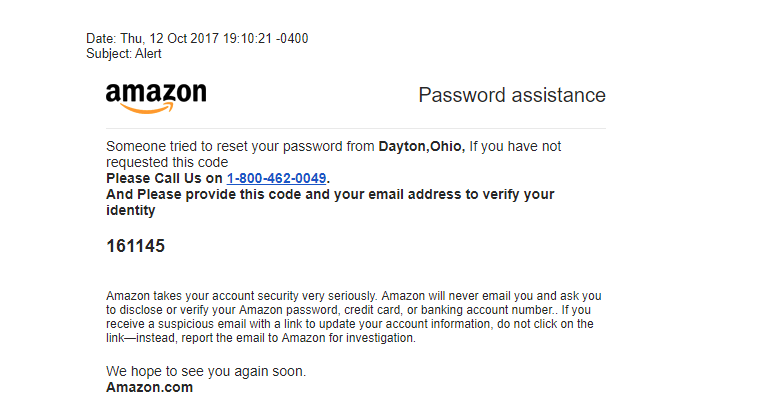
They received a fake e-mail from Amazon, alerting them that someone attempted to connect to their account by trying to change their password. A six digit code was transmitted with the instruction to call a number to verify the user’s identity. If the web users were not the source of these actions, they were invited to follow a specific procedure to secure their account. When they called the supposed Amazon number, they were directed to a Customers service department, located abroad. During the call, they had to go on a website and communicate the code to ensure the security of the account.

The copy of the phishing message:

A phishing attack more and more sophisticated

Fortunately, many web users have detected this phishing attack and didn’t fall into the trap. But for the others, were they victims of a malware or a data theft?

All web users are hit by these phishing attempts. They are part of our daily lives, but many brands raise awareness among their customers against these actions (mostly the banking industry which is the privileged target of hackers).

To be continued.

Disastrous consequences of a domain name non-renewal

Domain name - domain names renewal
Source of the image : SEO Link Building

The American telecommunication company, Sorenson Communication, has forgotten to renew a domain name for only a few days in June 2016. The decision has fallen at the end of September 2017, Sorenson Communication has to pay a fine of 3 million dollars. Why such a high amount?

The domain name which has fallen back into public domain was carrying a critical service for some users! It was the “Video Relay System” which telecommunication companies must provide to deaf people and persons with vocal disabilities, so they can make video calls and contact the 911 USA emergency number, by using sign language. Utah residents with these disabilities were unable to reach 911 for 3 days!

Sorenson Communication indeed realized rather late its omission and ended up renewing the domain name only 3 days later.

But this kind of omission can be easily prevented, thanks to the “automatic renewal” option for all your domain names portfolio. Your critical domain names, carrying services, website and/or mailboxes, will not be interrupted by a simple renewal omission.

On the fine of $3 million, 252 000$ are transferred to “The Federal Communication Commission” and $2.7 million to the company of “Telecommunications Relay Services Fund”, which has found a temporary solution to rent its bandwidth during these 3 sensitive days.

Equifax victim of a massive cyberattack

Equifax victim of a massive cyberattack

The American company Equifax, based in Atlanta, present in 24 countries, has been the prey of a particularly worrying cyberattack.

Equifax collects and analyzes personal data of customers soliciting a credit. At the beginning of September, the company revealed an intrusion in its database.

This IT hacking could have potentially concerned around 143 million American customers and many others customers soliciting a credit like Canada or Great Britain. The criminals have exploited a breakdown in a web application between mid-May and July. They have obtained names, social security numbers, birthdates, addresses and some driving license numbers. These data theft is really worrying.

This information will facilitate identity fraud and account hacking. In the United States, the social security number is necessary to work, open a bank account or obtain a driving license and usually to rent an apartment. Some data might even be already on sale on the Dark Web (part of the Web non-indexed by general search engines).

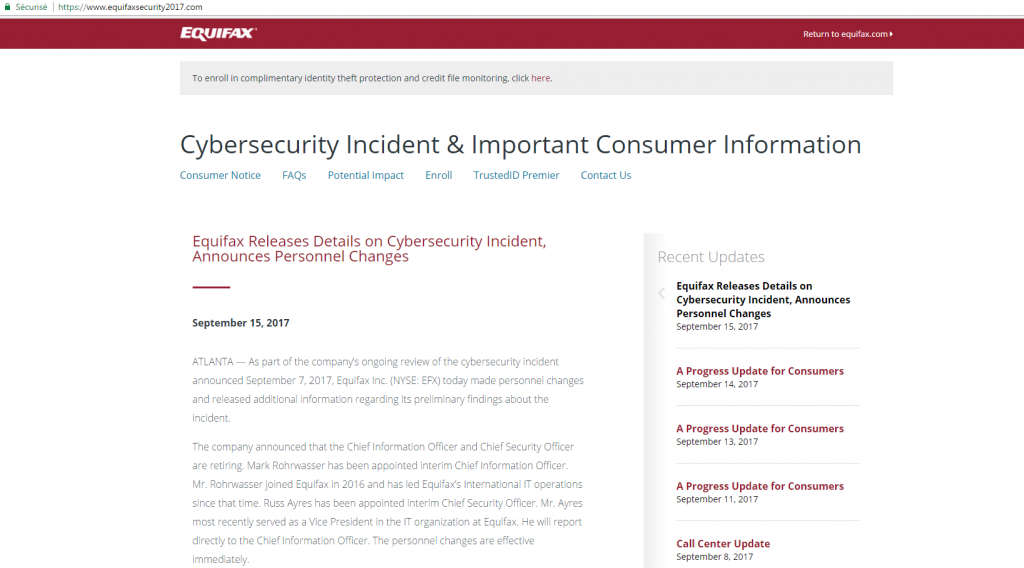
This attack directly touches the heart of Equifax’s identity and activity. The company has implemented a website (www.equifaxsecurity2017.com) and a phone number at the disposal of their customers and a security company to evaluate the damages.

Equifax victim of a massive cyberattack
Equifaxsecurity2017.com website

All companies should see this attack like a warning. This example is indeed the proof that companies can have difficulty in seeing what is happening inside their own computer networks. New attacks, each day more sophisticated, go more and more unnoticed.

Moreover, Equifax affirms to have discovered the attack on July the 29th. However, the communication done to the customers comes only at the beginning of September: an abnormal delay regarding data protection this sensitive. Today, those data have vanished into thin air.

This large scale hacking is far from being the first one. Last year, the Yahoo group has announced that one billion accounts have been hacked, while other American companies have also been the victims of hacking, like the Adult Friend Finder website, or Target, the distribution group. The thieves didn’t access to social insurance numbers, or driving licensing though.

This attack comes only to strengthen the necessity for companies to consider in their security strategy all the flaws likely to serve as entrance to cybercriminals.