The .CY registry announces the
registration of first level .cy domain names, i.e.domainname.cy
The owners of second level registered domain
names, can also apply for the same domain names with a first level extension .CY.
Please note that the 2019 Decree does not provide for commitment on any domain names and thus, all requests will be examined on First Come First Served basis.
To submit a request, don’t hesitate to contact our customer support.
With over 5 million mobile applications available today on the major apps stores like Google Play and App Store, over 2 000 new applications uploaded every day and almost 2 billion applications downloaded in France in 2018, mobile apps have rapidly grown over the last 10 years to become an essential element of the digital world.
According to a research done by FEVAD, the revenue from mobile commerce is estimated to 22 billion euros in France in 2018, i.e. ¼ of online sales. Thus, mobile applications represent a fast growing market.
Studies have shown that 68% of consumers identified as loyal to a specific brand have downloaded that brand’s app. Conversely, statistics indicate that 40% of users will go to a competitor after a bad mobile experience. Companies have then quickly come to realize that ensuring that their customers have a high quality and secured mobile experience when downloading and using their branded applications is the key to consumer loyalty.
The growth of fake mobile applications
As brands’ mobile applications have grown in popularity with consumers, the number of fake mobile applications being released into the market by malicious actors has also exploded. Fake mobile apps can be dangerous because they are associated with fraud attacks, and have become a growing threat to consumers. Indeed, they have increased by 191% from 2018 to 2019. The McAfee Mobile Threats report indicates that almost 65 000 new fake apps were detected in December 2018.
Despite the precautions taken by most major apps
platforms to mitigate the number of malicious applications uploaded on their
platform, cybercriminals continue to find ways to bypass these security
measures.
A recent example, the fake Samsung app which
has tricked 10 million Android users. This app named “Updates for Samsung”
promises firmware updates, but in reality is not affiliated to Samsung. Once
downloaded, the app proposes ads first and foremost. To download an update, the
user must pay a fee of $34.99. However, this operation is completely free of
charge since the firmware update is directly accessible from the smartphone’s
settings.
What to do against these fake mobile apps?
Given the importance and omnipresence of mobile
applications, it is absolutely essential for companies to incorporate into
their brand protection and security strategies, a mobile application protection
and a monitoring implementation of mobile apps present on the market.
Every second, a malicious application is active and poses a threat to brands and consumers. To face this, Nameshield proposes an online monitoring of mobile apps present on the applications stores, allowing to identify the ones that might be infringing your brands and assists you in the actions to implement.
The general availability of .MADRID, the geographical extension of Madrid, the capital city of Spain is near. Managed by the Comunidad de Madrid registry, this extension was launched last April following the calendar below:
Launching schedule
APL
period (Approved Launch Program): from 11/04/2019 to 06/06/2019
Sunrise
and LRP (Limited Registration Period) period: from 16/07/2019 to 10/12/2019
General availability: from
17/12/2019
Some requirements must be respected to register a .MADRID domain name. A .MADRID name’s registration is reserved to individuals or legal entities possessing a link with the Madrid Community:
Local
presence;
Professional,
personal, cultural or commercial activity in the Madrid Community;
Direct
or indirect link with the Madrid Community.
The date of the general availability planned for December 17 2019, is approaching, if you wish more information on your .MADRID registration, don’t hesitate to contact your Nameshield’s consultant.
Financial services companies are particularly affected by cyberattacks. They possess a wealth of information on the customers, protect their money and provide essential services which must be available day and night. They are a lucrative target. Among the favored lines of attacks: the DNS.
The Efficient IP’s Global DNS threat annual
report shows a constant growth of the DNS attacks’ number and the financial
impacts, with an average financial loss of 1.2 million euros in 2019. This
amount was estimated at 513 000€ in 2017 and 806 000€ in 2018.
If all the industries are affected by
cyberattacks, 82% of the companies surveyed have been affected and 63% have
suffered a traffic disruption, the financial industry pays a more important
price with 88% of impact. Conducted with 900 persons from nine countries of
North America, Europe and Asia, the study indicates that financial companies
suffered 10 attacks in average during the 12 last months, i.e. an increase of
37% compared to last year.
The increase of the costs is only one of the
DNS attacks’ consequences for the financial services industry. The most common
impacts are the cloud services’ downtime, experienced by 45% of financial
organizations, and internal applications downtime (68%). Furthermore, 47% of
financial companies have been the victims of frauds by phishing attacks aiming
the DNS.
The survey clearly shows the insufficient
security measures implemented for the DNS securing. The delay in applying security
patches is a major problem for the organizations of this industry. In 2018, 72%
of the interviewed companies admitted that a 3 days’ delay was necessary to
implement a security patch in their systems, 3 days during which they are
exposed to attacks.
Only 65% of the financial institutions use or
plan to integrate a trusted DNS architecture, they seem to be always late and not
to be sufficiently aware of the risks associated to this central point of their
infrastructure. The evolution of the threats on the DNS is constant, the attacks
are many and complex. It is essential to quickly react to better protect
yourself.
Industry, trade, media, telecom, health, education, government, service… many others sectors are affected by the attacks. Some solutions exist. ANSSI publishes every year the guide of good practices regarding the DNS resilience, which details many recommendations in order to be protected. Relying on an Anycast network; possessing a protection system against DDoS attacks; having a monitoring of DNS traffic and a team able to take action quickly; possessing an efficient security policy … As many measures essential to the resilience and efficiency of the DNS network against these damaging attacks in terms of financial and image impact.
Hoping to see at last better figures in the
2020 report.
During the first half of November, the 66th ICANN Summit was held in Montreal, Canada. This third and final annual summit devoted to policies applicable to Internet naming was eagerly awaited as the topics under discussion are numerous. At its closing, however, it left many participants a little bit disappointed.
A preview of the topics and postures during the weekend before the official launch of the Summit
The weekend
before the official opening of the Summit is usually an opportunity to get an
overview of the topics and postures involved. Not surprisingly, the expedited
Policy Development Process (ePDP) which aims to develop a consensus rule to
specify future conditions of access to personal data that are no longer
published in the WHOIS, the domain name search directory, due to GDPR, is one
of the major topics.
Among other
related topics, the replacement of the same WHOIS by the RDAP (Registration
Data Access Protocol) probably next year for generic domain names. This
replacement is not insignificant when we know that WHOIS has been in use for
nearly 35 years.
The body
representing governments, the GAC, has weighed up the issue of domain name abuse,
which has taken off considerably on the new generic extensions launched in
2012. When we know the rise of Internet practices aimed at weighing on
elections in certain countries and the economic impact of computer attacks and
hacking, we understand that this subject is being pushed by the GAC. While one
of ICANN’s topics is to clarify in their texts the notion of malicious uses, this
term refers to domains registered for phishing, malware, botnets and spam, the
other part concerns the means to stem them. The existence of abusive domains indeed
threatens the DNS infrastructure, impacts consumer safety and threatens the
critical assets of public and commercial entities. Finally, and not
surprisingly, the subject of a future round of new generic extensions has also
been on many lips.
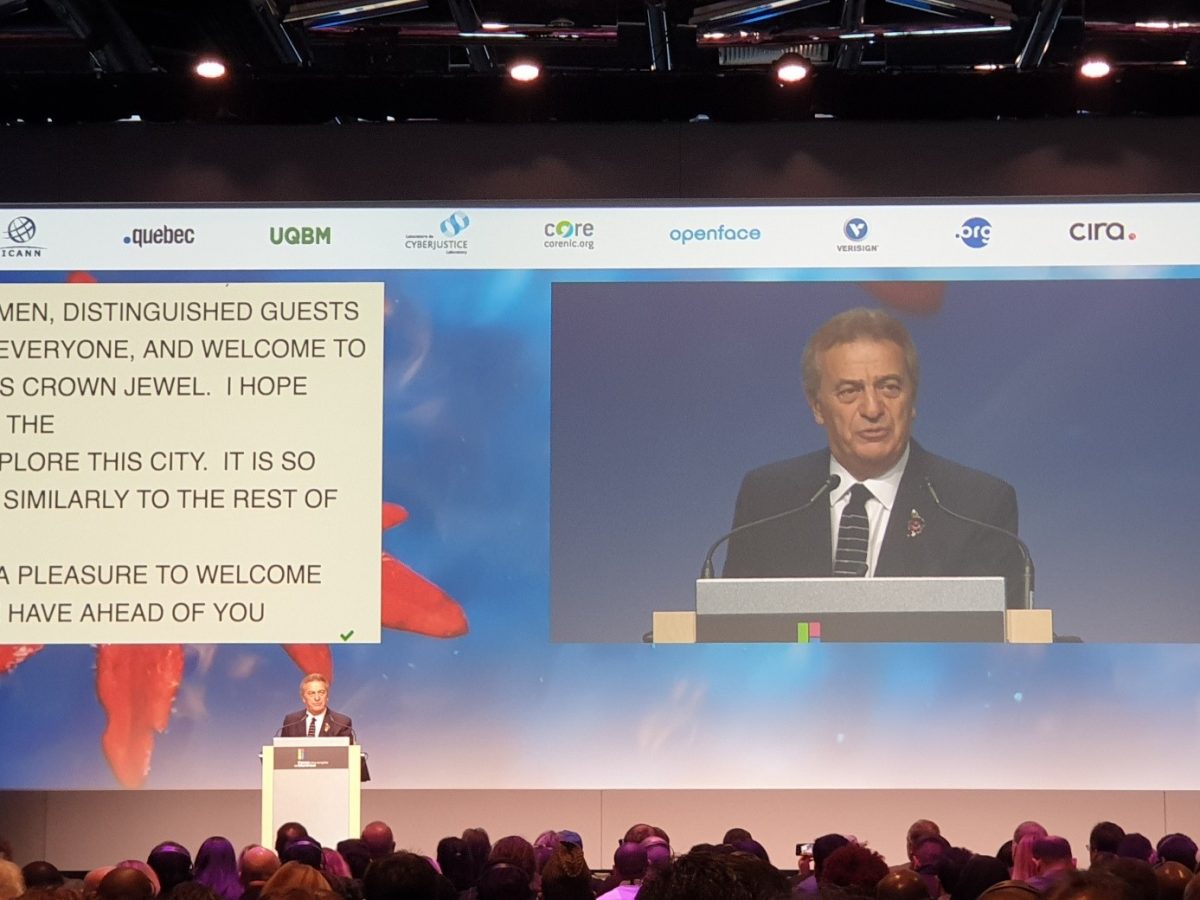
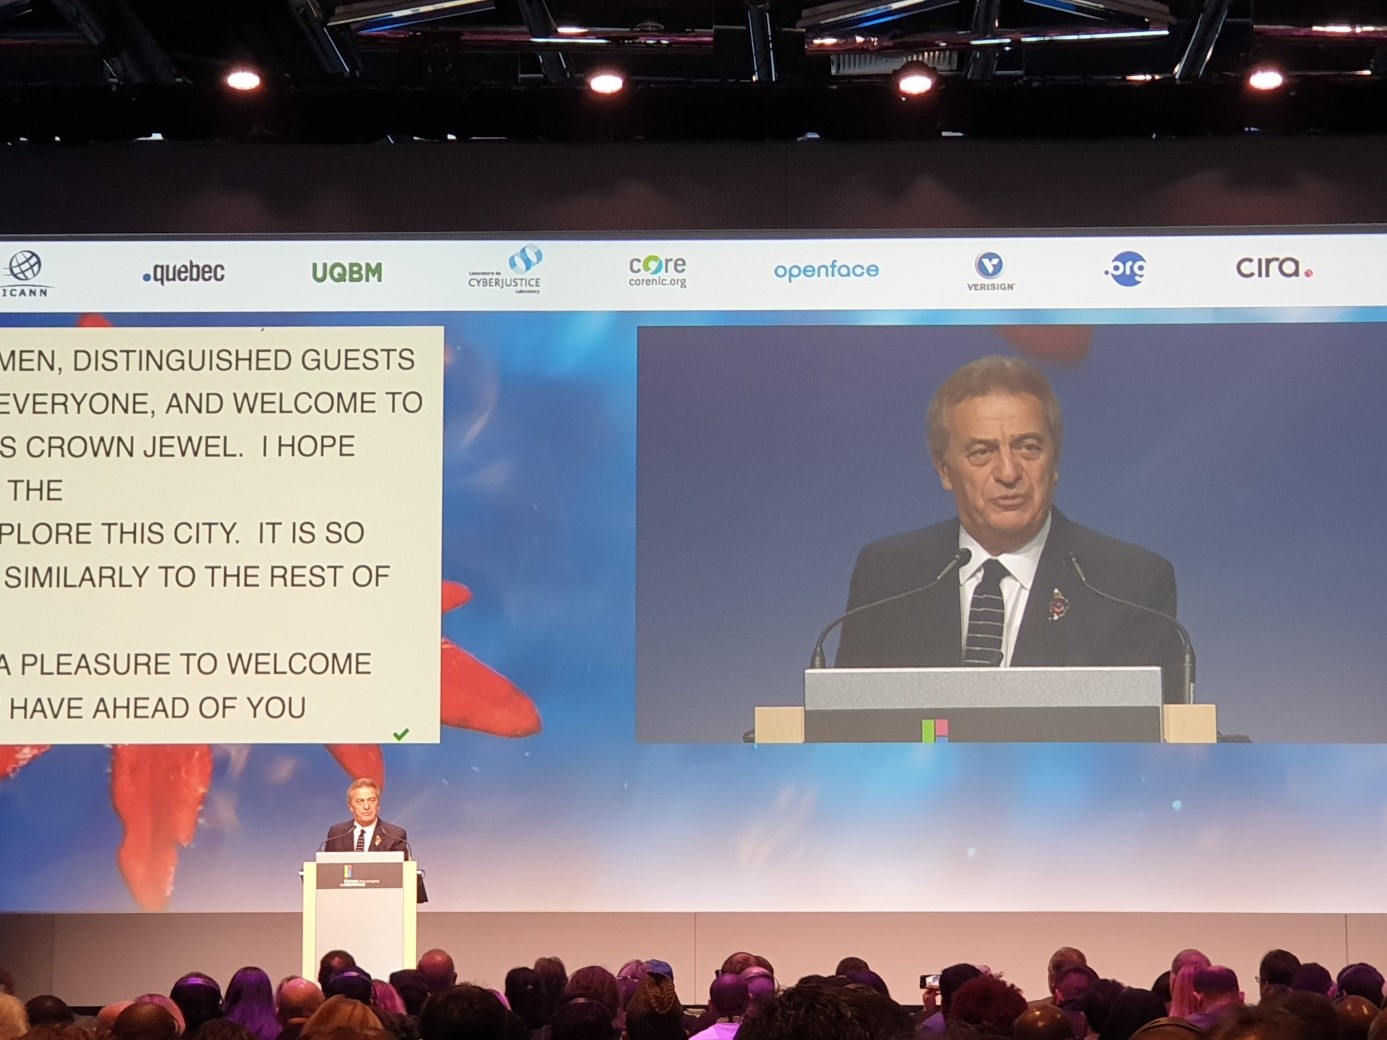
Cherine Chalaby at the ICANN Summit held in Montreal
“The best ICANN summit”, really?
During the traditional opening ceremony, which brings together all the guests for one hour (2500 according to Goran Marby, ICANN CEO) in a huge room to listen to various speakers, including Martin Aubé of the Quebec Government’s Ministry of Economy and Innovation, Cherine Chalaby, one of the ICANN Board members whose term ends at the end of the year, told his audience that ICANN66 would be the “Best ICANN summit”. It must be said, however, that at the end of the week of debates and meetings, which followed one another at a sustained pace, while the subjects under discussion are really numerous, the feeling regarding this assertion was more than mixed for many participants.
First, the
expeditious process for access to WHOIS non-public data is progressing with a
framework constrained by ICANN and the Personal Data Protection Authorities.
The outcome of this process is envisaged between April and June 2020 and it is
currently a centralized model where ICANN would allow the future lifting of
anonymity of data that are now masked due to GDPR which holds the line.
Then the subject that was probably
most often mentioned during this new summit week concerned abuses with domain
names. For ICANN, the subject is central because it is directly correlated to its
totem: the stability of the Internet for which they are the responsible. Since
February 2019, ICANN has been publishing some metrics on malicious practices
identified through DAAR, their Domain Abuse Activity Reporting.
Their latest report presented in
Montreal shows that 364 extensions (mainly new generic extensions from the 2012
round) revealed at least one threat posed by one of the domain names activated
on these extensions. More worryingly, new generic extensions would still account
for nearly 40% of malicious uses, compared to 60% for historical generic
extensions. This figure should be highlighted with the volume of these two
categories of extensions. Indeed, out of just over 200 million generic names,
new generic domains represent only 15% of the total number of registered names.
ICANN therefore wants this subject to be taken up by the entire community
present in Montreal.
Proposals were made by the various bodies present, some of which went so far as to request a policy development process (PDP). This last proposal, if it were to obtain ICANN’s approval, would have the unfortunate consequence of postponing the hypothetical schedule for a next round of new extensions, a subject that interested many of the guests present in Montreal. Indeed, for ICANN, the problem of the concentration of malicious practices in the new generic extensions must be solved before any future round, so that the PDP still in progress on the review of the last round of 2012 has gone almost unnoticed.
If the rules are slow to evolve on malicious uses, your Nameshield consultant can already provide you with adapted solutions to your needs on this key matter.
Nameshield uses cookies
Nameshield wishes to use cookies to ensure the proper functioning of the site and, with our partners, to measure its audience🍪.
Nameshield wishes to use cookies to ensure the proper performance of the website and, with our partners, to monitor its audience. More information in our Cookie Policy 🍪.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-advertisement
1 year
Set by the GDPR Cookie Consent plugin, this cookie is used to record the user consent for the cookies in the "Advertisement" category .
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
CookieLawInfoConsent
1 year
Records the default button state of the corresponding category & the status of CCPA. It works only in coordination with the primary cookie.
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Cookie
Duration
Description
_ga
2 years
The _ga cookie, installed by Google Analytics, calculates visitor, session and campaign data and also keeps track of site usage for the site's analytics report. The cookie stores information anonymously and assigns a randomly generated number to recognize unique visitors.
_gat_gtag_UA_25904574_14
1 minute
Set by Google to distinguish users.
_gid
1 day
Installed by Google Analytics, _gid cookie stores information on how visitors use a website, while also creating an analytics report of the website's performance. Some of the data that are collected include the number of visitors, their source, and the pages they visit anonymously.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Cookie
Duration
Description
NID
6 months
NID cookie, set by Google, is used for advertising purposes; to limit the number of times the user sees an ad, to mute unwanted ads, and to measure the effectiveness of ads.