On June 1970, one year after the Stonewall
Riots, which marked the birth of the LGBTQ rights movements, the first Gay
Pride parades took place in many US cities to claim liberty, equality and
denounce prejudice, persecution, bigotry and hate.
Fifty years later, with the launch of the new extension .GAY by the registry TOP LEVEL DESIGN, a new digital space is created for the LGBTQ community. This extension is thus intended for individuals, organizations, businesses supporting the LGBTQ community. It will increase their visibility and create a safe online space.
The launch of .GAY will follow the calendar below.
.GAY Launching Calendar
Sunrise
period: from 10/02/2020 to 06/05/2020
EAP
(Early Access Period): from 11/05/2020 to 18/05/2020
General
availability: from 20/05/2020
.GAY donations to LGBTQ nonprofit organizations
Note that for each new domain name registered, the .GAY donates 20% of registration revenue to LGBTQ nonprofit organizations like GLAAD and CenterLink which are currently the inaugural beneficiaries.
A .GAY domain name registration will become a way to express support to the LGBTQ community.
.GAY rights protections policy
The .GAY will give the possibility to create a safer space online for LGBTQ community. Indeed, the extension will be subject to a .GAY rights protections policy, which will allow to report any content that is harmful or harassing LGBTQ people, and to act against them by removing the content or suspending the site itself.
“The use
of .gay for anti-LGBTQ content or to malign or harm LGBTQ individuals or groups
is strictly prohibited and can result in immediate server-hold. Prohibited
behavior includes harassment, threats, and hate speech” highlights the
registry.
.GAY domain name registrations will be prohibited to parties that are, or are associated with, recognized hate groups inciting violence against the LGBTQ community.
For more information on the conditions for registration of your .GAY, don’t hesitate to contact a Nameshield’s consultant.
In November 2019, a press release announced that .ORG registry, Public Interest Registry (PIR), a non-profit organization managed by Internet Society, is going to be sold off to Ethos Capital, a private equity firm.
.ORG is the extension for non-profit organizations. The acquisition of PIR by Ethos has quickly concerned the organizations using .ORG, on the basis of the potential misuse of the extension by its new owner, which has, by its very nature, profit motives.
The concern? That the registrations and
renewals fees for .ORG domain names increase.
Yet, key figures of the Internet’s world, like
Andrew Sullivan (Internet Society CEO) are exited, seeing in this a strong
strategic partnership and a significant financial contribution allowing
Internet Society to advance its mission of a “more open, accessible and secure Internet for everyone”, as he
wrote in the press release about the acquisition of November 13, 2019.
It would seem that the fears created find their
origin in the “surprise” and lack of transparency around the deal, since the
transaction amount has not been disclosed.
These fears are, of course, the corollary of the removal on June 30, 2019, of the price caps imposed until now to .ORG fees (historically low) by ICANN, despite many reservations expressed by the community. Finally, the fact that Ethos has directly or indirectly a number of close connections to former ICANN members raises concerns to several voices of the industry.
The fear to see the increase of .ORG prices led Electronic Frontier Foundation (EFF) to launch the SaveDotOrg campaign, which aims to raise awareness about the potential impact of a .ORG price increase on the NGO’s budget constraints.
Also the possibility that Ethos Capital later
implements a principle of rights protections that could lead to a form of censorship,
as currently practiced in some countries wishing to silence NGOs.
In front of these protests, ICANN suspended the
acquisition operation last December and requests clarification from the
Internet Society.
More recently, in January 2020, a new candidate of the .ORG extension acquisition has appeared. It is a cooperative corporation (Cooperative Corporation of .ORG Registrants), gathering some web pioneer and former members of ICANN.
Browsers and Certification Authorities, the battle continues.
Image source : TheDigitalArtist via Pixabay
2019 was a busy year, with growing differences of opinion between browsers makers and Certification Authorities, an explosion in the number of phishing sites encrypted in HTTPS and significant progress on the depreciation of TLS v1.0.
Discussions on extended validation, more generally the visual display of certificates in browsers, and the reduction of the duration of certificates have taken a prominent place. None of these discussions are over, no consensus seems to be emerging, 2020 is looking like a busy year. Time to look ahead…
Will the fate of Extended Validation be determined?
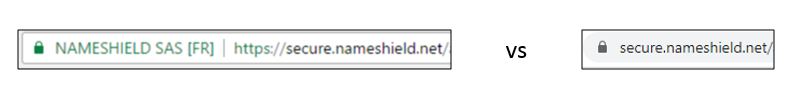
2019 saw the main browsers stop displaying the famous green address bar with the padlock and the name of the company, in favor of a classic and unique display, no longer taking into account the authentication level of the certificates:
However, discussions are still ongoing at the CA/B forum level, as well as within the CA Security Council. Both of these certificates regulatory bodies will be looking in 2020 for an intuitive way to display identity information of websites.
Historically approved by everyone, including the financial industry and websites with transactions, EV (the acronym for Extended Validation) was Google’s target in 2019. Other browsers, under the influence of Google, between Mozilla financed by Google and Microsoft and Opera based on Chromium open source, have followed in this direction. Only Apple continues to display EV.
For browsers, the question is whether or not TLS is the best way to present the authentication information of websites. It seems that it is not. Google assumes that it is not up to Certification Authorities to decide the legitimate content of a website and wants the use of certificates for encryption purposes only.
Of course, the Certification Authorities see things differently. One can certainly see a purely mercantile reaction, EV certificates are much more expensive. One can also wonder about the purpose of authentication beyond encryption. The answer seems to lie in the staggering statistics of phishing websites encrypted with HTTPS. Browsers have for the moment imposed an encrypted web indeed… but no longer authenticated!
2020 will therefore be the year of proposals from Certification Authorities: providing better authentication, including identification of legal entities, following the path of PSD2 in Europe… One thing is certain, identity has never been so important on the Internet and it is up to all interested parties to find a solution, including browsers to find a way to display strong authentication of websites. To be continued…
Certificates with a shorter duration: towards one-year certificates
825 days, or 27 months, or 2 years, the maximum duration currently allowed for SSL Certificates. However, since 2017 and a first attempt within the CA/B forum, the industry is moving towards a reduction of this duration to 13 months (1 additional month to cover the renewal period).
Google and browsers came back in 2019 with another vote submitted to the CA/B forum, again rejected but by a smaller majority. The market is on the move. Players like Let’sEncrypt propose certificates with a duration of 3 months, others want to keep long durations to avoid overloads of intervention on servers. One thing is certain, the market does not have the automation systems in place yet to make the management and installation of certificates easier, a delay of one or two more years would otherwise be preferable, or at least judicious.
But all this is without counting on Google threatening to act unilaterally if the regulator does not follow… certainly in 2020.
From TLS 1.0 to TLS 1.3: forced advance
Expected in January 2020, Microsoft, Apple, Mozilla, Google and Cloudflare have announced their intention to depreciate support for TLS 1.0 (a protocol created in 1999 to succeed SSL 3.0, which has become highly exposed) and TLS 1.1 (2006), both of which are currently suffering from too much exposure to security flaws.
While TLS 1.2 (2008) is still considered secure today, the market seems to be pushing for TLS 1.3, the most recent version of the standard, finally released in the summer of 2018. TLS 1.3 abandons support for weak algorithms (MD4, RC4, DSA or SHA-224), allows negotiation in fewer steps (faster), and reduces vulnerability to fallback attacks. Simply put, it is the most secure protocol.
A small problem, however, is that many websites are taking action. At the beginning of 2019, only 17% of the Alexa Top 100,000 websites supported TLS 1.3, while just under 23% (22,285) did not even support TLS 1.2 yet. If the decision to depreciate older versions of the protocol is a good one, the form adopted by the major web players can be criticized, in particular by its unilateral nature. In the meantime, get ready, we are heading there.
The threat of quantum computing
Companies are talking more and more about quantum computing, including Google. But the reality is, while quantum will impact our industry, it certainly won’t be in 2020, or for at least a decade. There are still many questions that need to be answered, such as: What is the best algorithm for quantum resistance? No one has that answer, and until there is a consensus in the industry, you are not going to see any quantum solutions in place.
IoT is growing, but the lack of security remains a problem
IoT is a success, but a number of deployments are being delayed due to a lack of security. In 2020, cloud service providers will provide or partner with security companies to provide a secure provisioning and management of devices, as well as an overall secure IoT ecosystem, for their customers.
The regulatory frameworks for IoT manufacturing and deployments will most certainly be led by the EU, although we will also see an increase in the US. Attacks, compromises and IoT hacking will, unfortunately, continue. In addition, security standards will not be met and we will not even come close to a higher percentage of secure devices. Why is that? Original Equipment Manufacturers (OEMs) are still not willing to pay the costs involved or pass them on to consumers for fear of losing sales.
China’s encryption laws will create a lot of uncertainty
In recent years, part of the digital transformation of the world has led to the codification of rights and restrictions on data in national laws and regional organizations. PSD2, GDPR, CCPA, PIPEDA… a real headache for international companies faced with regulatory standards and compliance.
On January 1, 2020, China’s encryption law was due to come into force. An additional data and… still unclear to those doing business in China. Clarification is still needed on several fronts. For example, commercial encryption for international companies must be approved and certified before it can be used in China – but this certification system has not yet been created. Similarly, there is uncertainty about the key escrow and the data that must be made available to the Chinese government. This has led to a wave of speculation, misinformation and, ultimately, overreaction. Given the opacity of parts of the new Regulation, many companies are opting for a wait-and-see approach. This is a wise tactic, assuming your organization does not have an experienced Chinese legal expert.
The .CY registry announces the
registration of first level .cy domain names, i.e.domainname.cy
The owners of second level registered domain
names, can also apply for the same domain names with a first level extension .CY.
Please note that the 2019 Decree does not provide for commitment on any domain names and thus, all requests will be examined on First Come First Served basis.
To submit a request, don’t hesitate to contact our customer support.
With over 5 million mobile applications available today on the major apps stores like Google Play and App Store, over 2 000 new applications uploaded every day and almost 2 billion applications downloaded in France in 2018, mobile apps have rapidly grown over the last 10 years to become an essential element of the digital world.
According to a research done by FEVAD, the revenue from mobile commerce is estimated to 22 billion euros in France in 2018, i.e. ¼ of online sales. Thus, mobile applications represent a fast growing market.
Studies have shown that 68% of consumers identified as loyal to a specific brand have downloaded that brand’s app. Conversely, statistics indicate that 40% of users will go to a competitor after a bad mobile experience. Companies have then quickly come to realize that ensuring that their customers have a high quality and secured mobile experience when downloading and using their branded applications is the key to consumer loyalty.
The growth of fake mobile applications
As brands’ mobile applications have grown in popularity with consumers, the number of fake mobile applications being released into the market by malicious actors has also exploded. Fake mobile apps can be dangerous because they are associated with fraud attacks, and have become a growing threat to consumers. Indeed, they have increased by 191% from 2018 to 2019. The McAfee Mobile Threats report indicates that almost 65 000 new fake apps were detected in December 2018.
Despite the precautions taken by most major apps
platforms to mitigate the number of malicious applications uploaded on their
platform, cybercriminals continue to find ways to bypass these security
measures.
A recent example, the fake Samsung app which
has tricked 10 million Android users. This app named “Updates for Samsung”
promises firmware updates, but in reality is not affiliated to Samsung. Once
downloaded, the app proposes ads first and foremost. To download an update, the
user must pay a fee of $34.99. However, this operation is completely free of
charge since the firmware update is directly accessible from the smartphone’s
settings.
What to do against these fake mobile apps?
Given the importance and omnipresence of mobile
applications, it is absolutely essential for companies to incorporate into
their brand protection and security strategies, a mobile application protection
and a monitoring implementation of mobile apps present on the market.
Every second, a malicious application is active and poses a threat to brands and consumers. To face this, Nameshield proposes an online monitoring of mobile apps present on the applications stores, allowing to identify the ones that might be infringing your brands and assists you in the actions to implement.
Nameshield wishes to use cookies to ensure the proper performance of the website and, with our partners, to monitor its audience. More information in our Cookie Policy 🍪.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-advertisement
1 year
Set by the GDPR Cookie Consent plugin, this cookie is used to record the user consent for the cookies in the "Advertisement" category .
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
CookieLawInfoConsent
1 year
Records the default button state of the corresponding category & the status of CCPA. It works only in coordination with the primary cookie.
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Cookie
Duration
Description
_ga
2 years
The _ga cookie, installed by Google Analytics, calculates visitor, session and campaign data and also keeps track of site usage for the site's analytics report. The cookie stores information anonymously and assigns a randomly generated number to recognize unique visitors.
_gat_gtag_UA_25904574_14
1 minute
Set by Google to distinguish users.
_gid
1 day
Installed by Google Analytics, _gid cookie stores information on how visitors use a website, while also creating an analytics report of the website's performance. Some of the data that are collected include the number of visitors, their source, and the pages they visit anonymously.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Cookie
Duration
Description
NID
6 months
NID cookie, set by Google, is used for advertising purposes; to limit the number of times the user sees an ad, to mute unwanted ads, and to measure the effectiveness of ads.