Nameshield signs up the Paris Call in order to actively contribute to the Internet’s stability

Paris Call - Nameshield

Just one year ago, in the context of the first Paris Peace Forum, the French President, Emmanuel Macron, launched the Paris Call for trust and security in cyberspace. This call is a political declaration aiming to express a mobilization on the stability in the cyberspace and strengthens the efforts of the international community and many actors involved in the digital security issues. This text reminds some principles that we think are fundamental, like the application of the international rights and the Human rights in the cyberspace. It also highlights the need of a multi actors’ approach, to create standards which will allow us to fully benefit, i.e. in a reliable and secure way, from opportunities provided by the digital revolution.

Lastly, the Paris Call promotes the strengthening of the digital products and services’ security that we use for example, in our daily lives. The text aims in that sense, to prevent cyberattacks perpetrated by malicious actors, which threaten all the users of the cyberspace.

Aware that our Society’s development, on the economic, cultural and democratic fronts, requires a strengthened trust of the information that flows through the Internet, Nameshield, which has worked for 25 years to protect the digital identity of its clients; companies, local collectivities and administrations through the use of their domain names, wished to join this initiative and sign the Paris Call.

Its job consists in ensuring the integrity and resilience of the identity of individuals and organizations on the Internet, represented today by the domain name. By highly protecting data on domain name identity cards (Whois) and by providing a high availability and high performance service through the associated Domain Name System (DNS), Nameshield contributes to a large extent to the second principle of the Paris Call: Protecting the Internet. To prevent activity that intentionally and substantially damages the general availability or integrity of the public core of the Internet.

Cornerstone of the Web, the Domain Name System (DNS) serves as the Internet directory. This protocol translates a domain name into an IP address, based on a database distributed on thousands of machines. If the DNS falls because of data corruption or a denial of service attack, all your websites and emails would become inaccessible, which is completely unthinkable nowadays! The DNS must be protected and must stay highly available.

Protocol created in the 1980’s, security flaws regarding the usual functioning of the DNS have been identified since its creation. That is why, a new secured protocol, DNSSEC, has thus been developed to ensure the authenticity of the exchanges through a certified signature. Other solutions can complete the resilience of your identity on the Internet: the registry lock, SSL certificates…

The security solutions proposed by Nameshield, an independent French company that stores its data in France and possesses its own anycast and resilient DNS infrastructure, certified ISO 27001 on all its domain names activity, are compliant with the ANSSI recommendations on the good practices regarding the domain names’ acquisition and exploitation.

In the context of the 2nd Paris Peace Forum, the Ministry of Foreign Affairs wished to illustrate the second principle of the Paris Call: Protect the Internet by highlighting the services proposed by Nameshield. The company is proud to be able to collaborate, at its level, with the actors implicated in digital security issues in order to make the Internet more reliable and thus contribute to the security of the cyberspace.
https://pariscall.international/en/principles

Advices on how to change the domain name without losing its referencing

Advices on how to change the domain name without losing its referencing
Image source: DiggityMarketing via Pixabay

During a rebranding for marketing purposes, in the context of a merger or an acquisition for example, a company can change its website’s domain name.

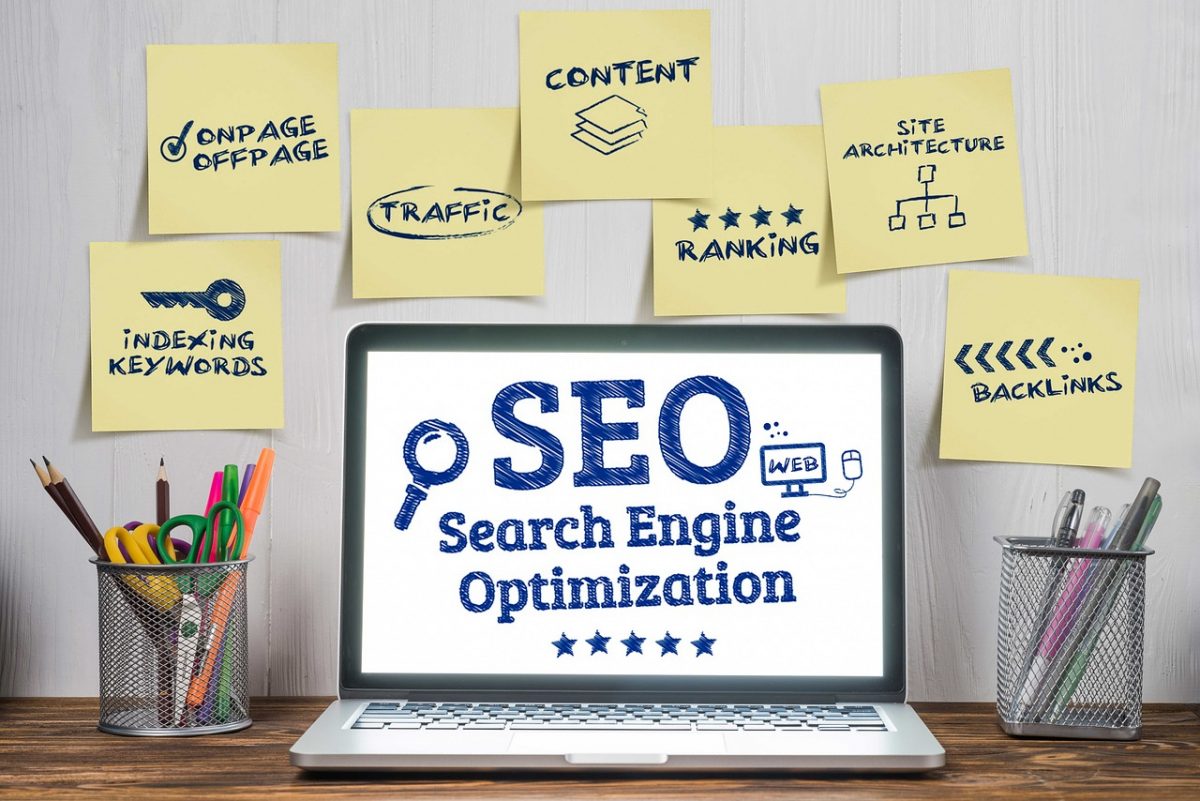
At the search engines’ level, it is all the pages that change, as if this was a brand new website. Therefore, how not to lose the work done on the SEO and make a successful transition, in particular if the website is old?

In the case of a rather old website with an optimal referencing on the existing domain name, transferring a website on a new name can ruin the time-consuming work that is the SEO. If the decrease of the traffic from organic search is normal (and temporary), some advises can help lessen the downturn, at least during the transition period.

Copy identically your website and implement 301 redirections

The first tip is to completely keep the website’s architecture, so that only the domain name changes in the URL.

Then, permanent redirections (301 redirections) must be created from each pages of the former website towards the corresponding page of the new website. Do not implement multiple redirections.

This process must be closely monitored to ensure that each 301 redirection is effective. The search engines will know that it’s not necessary to index the former name anymore but it’s the new one that must be indexed now. To ensure this, it is necessary to check that none of the former pages is accessible through the former domain name.

Have the backlinks updated

Google uses parameters linked to confidence indicators in its algorithm, thus to trusted websites, deemed as such by the search engine (indicators like the age of the website, the transparency of the legal notices, the ratio links number/words number per page, the links number pointing from other websites to this one, the extensions like .edu, .gov, the institutional websites, media websites, etc.) Hence, it can be interesting to quickly obtain the links from this kind of trusted websites at the time of the migration.

Along the same lines, reviewing your backlinks and requesting to the websites that refer to your website to update these links, so they link towards the new name, is an advantage. Of course, if you have many backlinks, concentrate on the more important backlinks regarding the referencing.

Inform Google

Lastly, it’s possible to directly inform Google of the changing through Google Search Console, the search engine will then update its index.

Register the sitemap

By submitting a sitemap file for the new website to the search engines, you will gain time in referencing by immediately giving to the engines the pages to index.

Keep the same holder for the new domain name

Make sure that the new domain name has the same proprietary information on its whois as the former domain name. Google may check these data.

Be patient

Do note that on Bing you will need an average of 2 months to get your referencing back, and about 6 to 7 months on Google.

[New gTLD] Launch of .NEW by Google

[New gTLD] Launch of .NEW by Google
Image source: 377053 via Pixabay

Following the launch of .APP, .PAGE, and .DEV among others, Google (Charleston Road Registry), launches the new extension .NEW in Sunrise period as of October 15, 2019.

Conditions for registration of a .NEW

  • All domains on .NEW must resolve to action generation or online creation flows. Once resolved, the web user should be able to ‘create’ something without any further navigation. For example, docs.new proposes a dedicated page proposing the direct use of Google online word-processing software allowing a new document creation page.
  • Any .NEW domain will need to be live within 100 days of registration.

If these conditions are not respected, the registry will consider the registration as non-compliant with the registration policy. In this case, the name will be placed on hold. The registrant will then be notified to correct and apply these conditions, if no action is taken, the domain will be blocked then deleted.

Launch calendar

  • Sunrise period: from October 15, 2019 to January 14,2020
  • LRP (Limited Registration Period): from January 14 to July 14, 2020
  • General availability: from July 21, 2020

For more information on the conditions for registration of your .NEW, don’t hesitate to contact us.

The alarming Kaspersky report: nine times more attacks aiming connected objects than in 2018

The alarming Kaspersky report: nine times more attacks aiming connected objects than in 2018
Image source: TheDigitalArtist via Pixabay

Last October 15, Kaspersky, the antivirus software company, published an edifying report about the volume of cyberattacks directly aiming connected objects.

Although the industry expected that this new generation of objects would be directly targeted by cyberattacks, the increase in the cyberattacks number is alarming and lets easily imagine the security flaws that the connected objects present.

According to the estimation presented by Kaspersky, between the beginning of 2018 until mid-2019, the attacks would have reached the record of 105 million, i.e. nine times more than the previous year as a whole.

In order to conduct this research, Kaspersky used the trap technique by deploying more than 50 honeypots across the world. A Honeypot is a program that imitates the connected objects’ signature specifically created to attract cybercriminals. It was then possible to detect attacks from pirates that fell into the trap set for them. According to Kaspersky, during this experience, more than 20 000 sessions would have been infected every 15 minutes. 105 million attacks from 276 000 unique IP addresses have then been detected (compared to 12 million in 2018).

Furthermore, the report indicates that both in 2018 and 2019, China and Brazil are vying for the top position of the countries that served as the origin of the attacks launched.

The main malwares that use the security flaws of connected objects are well known (Mirai for example) and identified.

While we are aware that IoT is a privileged playground for pirates, the first security measures are far from being systematically applied. It’s essential for example to change the password installed by default for each connected devices’ purchase. For reminder, although technologies of cyber malice are indeed more and more sophisticated, the first gateway for pirates remains the users’ lack of vigilance.

New eligibility criteria for .EU

New eligibility criteria for .EU
Image source: OpenClipart-Vectors via Pixabay

As of October 19, 2019, internationally-based EU citizens can now register .EU or .ею domain names.

The .EU is the country code top level domain for the European Union. More than 3.6 million registrations spread out across Europe make this TLD a popular extension. Initially, this extension is only reserved to companies and individuals residing within EU and EEA member states. However in order to meet the needs of an ever-changing digital environment, EURid, the .EU registry, changes this eligibility criteria to extend it to all EU citizens living around the world.

“We are excited to be able to extend the registration criteria to EU citizens around the world. The .eu domain is now closer to your ambitions, achievements and dreams. It is the bridge connecting you to your friends and family – even if you live outside the EU. It will always show your roots, your outlook, and your cultural values.” – Marc van Wesemael, EURid`s CEO.

For more information on the conditions for registration of your .EU, don’t hesitate to contact us.