Phishing is cybercriminals’ means of choice to hijack users‘ data, posing as a trusty company and then encouraging them to deliver personal information. We are often more inclined to think that this technique is reserved to hackers who try to steal banking or very sensitive information, and yet!
Source : mohamed_hassan via Pixabay
An American student of Ygnacio Valley High School, in California, had a great time reproducing identically the website on which his teachers connect to enter marks and comments. This same student then emailed his teachers to connect to the fake school’s interface, which looked exactly the same as the original one. Thus, he could retrieve their login ID and passwords, and used them in order to raise his grades but also to lower his classmates’ grades.
Arrested by the police, the student said that what he had done was “as easy as stealing a candy from a baby”. Expelled from school, he was identified thanks to his computer IP address.
Quite light in consequence, this data corruption attempt highlights the simplicity of access to this hacking means. Today, phishing is one of the most popular methods and the easiest to implement. Web users, while unaware and fooled by similarities, consequently provide personal, sometimes very sensitive data.
The good news just arrived, Webstresser.org, one of the websites most responsible of million DDoS attacks has been dismantled. This shutdown has been possible thanks to Europol’s active intervention.
For reminder, a DDoS is a cyberattack. The operating mode is to saturate queries servers so the websites hosted on these same servers cannot operate for web users anymore.
Many countries hand in hand to dismantle the network
According to the National Crime Agency’s research, Webstresser.org has been used by hackers for the launching of almost 4 million attacks around the world. Among its victims, there are many British banks.
To carry out this large scale operation, five countries, Croatia, Scotland, Canada, Netherlands and Serbia have combined their best policemen to lend a hand to Europol.
Although this is an operation of international concern, the German, Dutch and American authorities were in charge of closing the website definitely. Now, its operators can’t access it anymore and a message left by the American Ministry of Defense serves as the home page.
Heavy penalties for the hackers
The shutdown of webstresser.org also led to a wave of arrests in many countries like Scotland, Croatia and Serbia. According to the French law, a cyberattack is a criminal offence and the penalties are severe. Thus, if the attack aims individuals, the hacker or hackers can be sentenced to 5 years of imprisonment and a fine of 150 000 euros. If the attack touches the State or its institutions, the penalty can go up to 7 years of imprisonment and a fine of 300 000 euros.
Following this great haul, the Europol spokeswoman and operations coordinator, Claire Georges announced that measures will be taken against all users of the website around the world and that arrests will be expected.
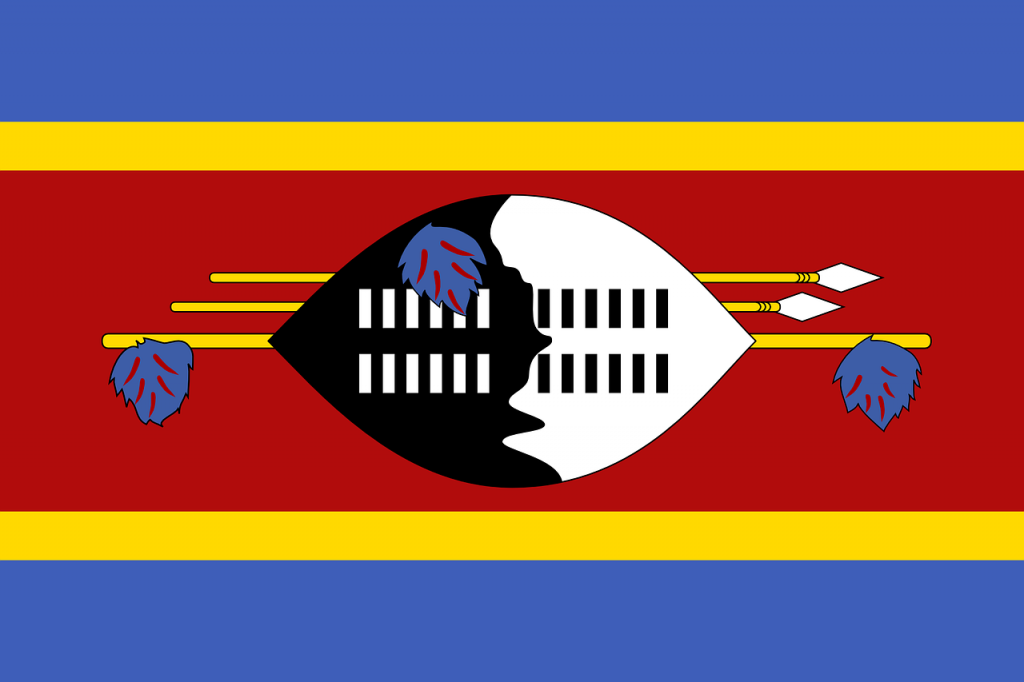
We have learned from the press that Swaziland will change its name at the will of its Monarch.
Indeed, this little South African territory has not changed its name after the decolonization, fifty years ago. It will soon be the case, with the term eSwatini, the country of Swazi. If this information is more of a geopolitical notion, it will have an impact on the country’s abbreviation within the ISO standard 3166-1 alpha 2, and its extension will then change; a similar situation to the one of Kazakhstan, already discussed on this blog.
A new example which highlights the importance of the country’s stability in the choice of an extension used for an active communication.
In a recent article in this blog, we mentioned the arrival of Chrome 68 in July 2018 and the fact that HTTP will be considered “not secure” from then on. Well, this is not the only weapon that Google is planning to use to encourage large-scale adoption of encrypted websites. You may not be aware, but Google has submitted a number of applications to ICANN as part of the new TLD program, and as a registry, they have secured the management of 45 top-level domains*. Just as the .bank and .insurance extensions have very strict security rules, Google has announced that they will apply HSTS implementation and pre-loading to their new TLDs therefore making HTTPS implementation mandatory.
What is HSTS?
HTTPS Strict Transport Security (HSTS) is a way in which browsers automatically enforce HTTPS-secured connections instead of unsafe HTTP. For example, if the website http://www.nameshield.net is on the list, a browser will never make insecure connections to the website, it will always be redirected to a URL that uses HTTPS and the site will be added to its list of sites that must always be accessed through HTTPS. From thereon, the browser will always use HTTPS for this site, whatever happens, whether the user has accessed the site via a Favorite, a link or simply by typing HTTP in the address bar, he has nothing more to do.
HSTS was first adopted by Chrome 4 in 2009, and has since been integrated in to all major browsers. The only flaw in the process is that browsers can still reach an unsafe HTTP URL the first time they connect to a site, opening a small window for attackers to intercept and carry out such attacks as Man-in-The-Middle attacks, misappropriation of cookies or the Poodle SSLv3 attack which was very much in the news in 2014.
A fully secured Top-Level Domain
HSTS pre-loading solves all this by pre-loading a list of HSTS domains into the browser itself, eliminating the threat of attacks. Even better, this pre-loading can be applied to entire TLDs, not just domains and subdomains, which means that it becomes automatic for anyone who registers a domain name ending in that TLD.
Adding an entire TLD to the HSTS pre-upload list is also more efficient because it secures all domains under this TLD without having to include all of the domains individually. Since HSTS pre-load lists can take months to update in browsers, TLD setup has the added benefit of making HSTS instant for newer websites that use them.
HTTPS deployment will be obligatory for .app and .dev extensions
Google is therefore planning to make HSTS mandatory for its 45 TLDs in the coming months. What does that mean? Millions of new sites registered under each TLD will now be HTTPS (and domain owners will need to configure their websites to switch to HTTPS or they will not work). In order to use a .dev, .app, .ads, .here, .meme, .ing, .rsvp, .fly … domain name, you will need to acquire an SSL certificate and deploy HTTPS.
Our team is at your disposal for any questions related to TLDs, domain names or SSL certificates.
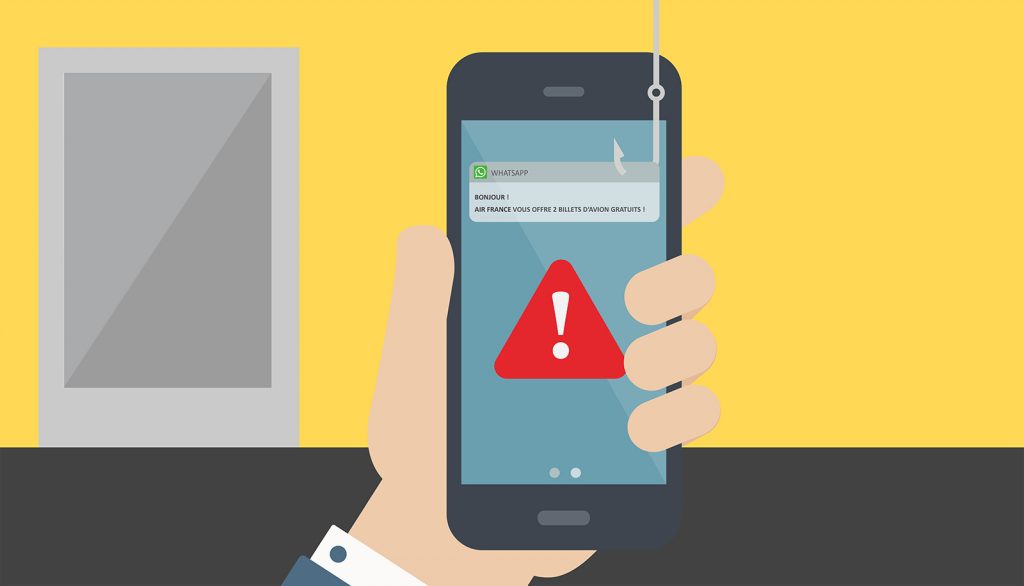
Recently, many frauds campaigns offering free Nike shoes here and IKEA vouchers of 500€ there have been going on. Last case in date, a fraudulent e-mails campaign announcing the winning of airline tickets with a nice value of 500€, graciously offered to the winners of a supposed contest proposed by Air France airline company. This scam has circulated around France and was shared on social networks, by e-mails and even relayed on WhatsApp.
A misleading typography: typosquatting
If we look at the e-mail in question, the link www.airfrạnce.com, inserted in the message, seemed to correspond to the official website address of Air France. Except for one little detail… The “a” of France is not a “a” of Latin alphabet but the “ạ” of Vietnamese alphabet. A single dot close then! Amazing case of typosquatting, a practice misleading web users by replacing, adding or deleting a letter in a domain name with the famous brand. Without enough vigilance, web users while thinking they are on a trusted website, could click on the link and find themselves redirected towards a page totally independent of the official website of the brand. On this page, a form to fill with their precious personal data in order to have a chance to win free tickets in this case. A confirmed scam.
The aim of these phishing and frauds campaigns is to collect as many personal information as possible. In other words, the identity thieves, the source of this kind of online attacks seek to obtain the e-mail, phone number and all interesting data of the tricked Internet user.
It was after the alert by Zataz website was sent, that Air France confirmed that it was indeed a fraud. It also encouraged web users to not consider this kind of message. It is also important to specify that the official website of the airline company is secured and authenticated by an SSL certificate, the browsers displaying the https://www.airfrance.fr
What to do in front of these attacks and how to prevent them
The first reaction to adopt is wariness on the user’s side. The more the offer and the benefit are attractive, the more cautious you should be. Don’t communicate your personal data via a form or by return of mail without checking beforehand the request’s authenticity.
Always check the final URL of the page on which you are redirected, be attentive to the typography. Generally, only the information on site are official. An SSL certificate presence and the proprietary data displaying are also good indicators.
On the brands owners’ side, a naming and defensive registration strategy allows to best protect its users. The efficient monitoring implementation will also allow to detect phishing attempts as soon as possible and to take action early in order to stop them.
Nameshield uses cookies
Nameshield wishes to use cookies to ensure the proper functioning of the site and, with our partners, to measure its audience🍪.
Nameshield wishes to use cookies to ensure the proper performance of the website and, with our partners, to monitor its audience. More information in our Cookie Policy 🍪.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-advertisement
1 year
Set by the GDPR Cookie Consent plugin, this cookie is used to record the user consent for the cookies in the "Advertisement" category .
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
CookieLawInfoConsent
1 year
Records the default button state of the corresponding category & the status of CCPA. It works only in coordination with the primary cookie.
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Cookie
Duration
Description
_ga
2 years
The _ga cookie, installed by Google Analytics, calculates visitor, session and campaign data and also keeps track of site usage for the site's analytics report. The cookie stores information anonymously and assigns a randomly generated number to recognize unique visitors.
_gat_gtag_UA_25904574_14
1 minute
Set by Google to distinguish users.
_gid
1 day
Installed by Google Analytics, _gid cookie stores information on how visitors use a website, while also creating an analytics report of the website's performance. Some of the data that are collected include the number of visitors, their source, and the pages they visit anonymously.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Cookie
Duration
Description
NID
6 months
NID cookie, set by Google, is used for advertising purposes; to limit the number of times the user sees an ad, to mute unwanted ads, and to measure the effectiveness of ads.