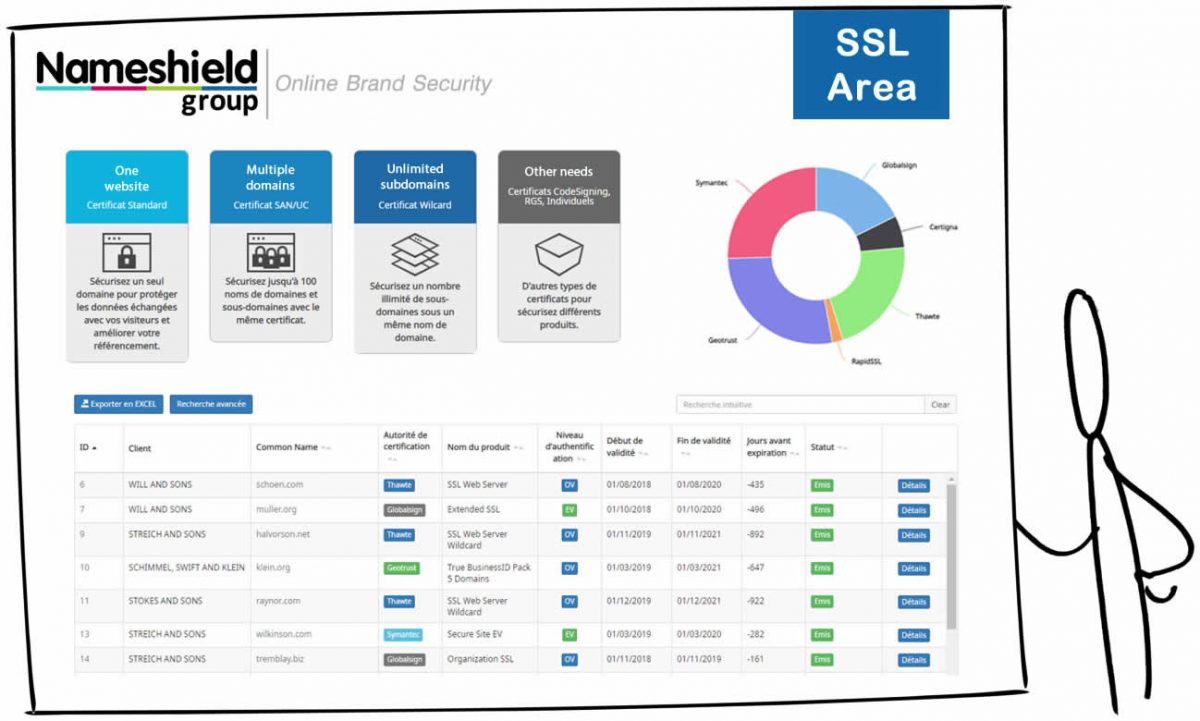
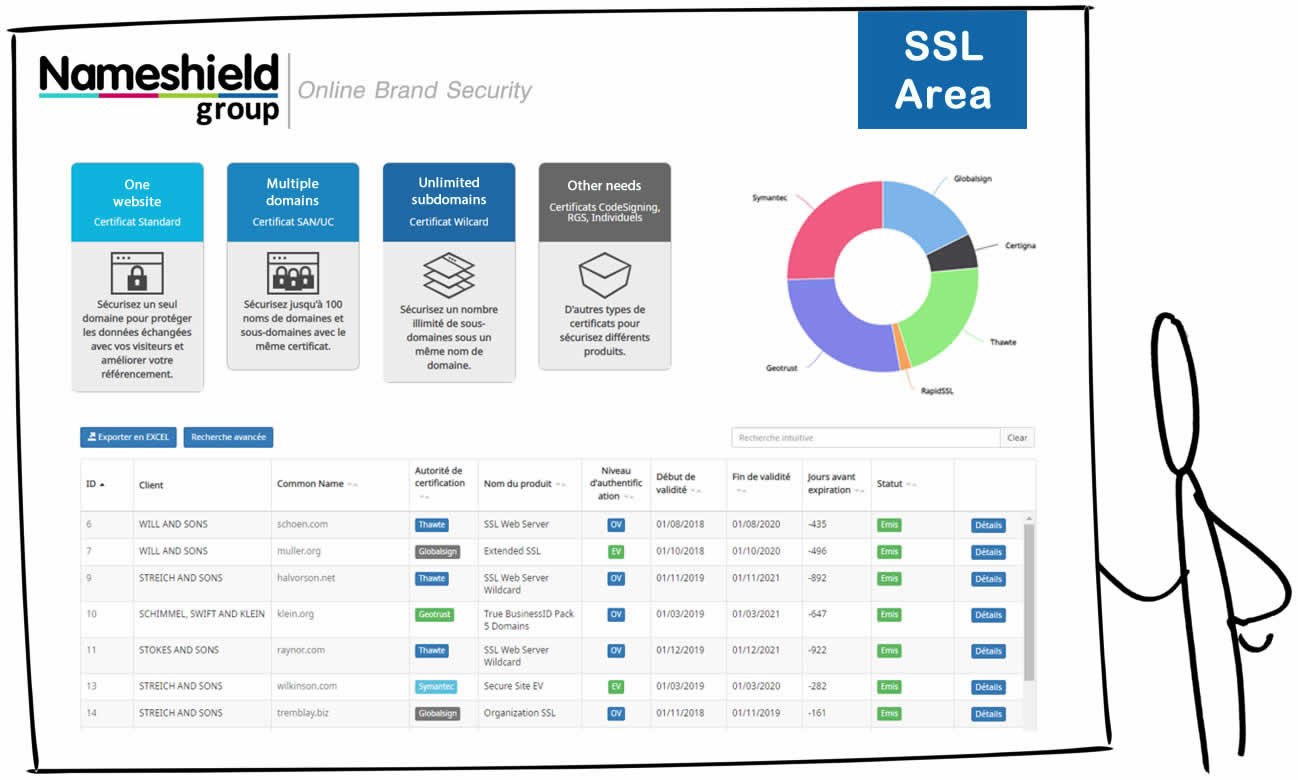
More user-friendly, more comprehensive, more
attractive… our brand new and improved
Nameshield SSL interface is being launched on Thursday, June 13th allowing
you to manage all of your certificates.
You will now have access to key metrics on your
certificate portfolio, to different certificate lookup views (such as complete
portfolio, detailed overview, certificates nearing expiry, pending orders,
expired or revoked certificates), to an Organization and Contact management
tool and a redesigned ordering system.
Lastly, a decision support tool has been
included in the interface to help you choose the certificate that’s right for
your needs.
The certificate range has been updated to cover
all types of certificates, SSL, RGS, Code Signing, Individual certificates and
with all levels of authentication.
The SSL team remains at your disposal for a
demonstration and a complete user guide is available covering all possible
operations and actions.
On Friday May 17th, 2019, the
Council of Ministers of the European Union presented the creation of a
blacklist identifying the perpetrators of cybercrimes located outside the EU.
Thus this is a new legal context which has been
validated by the EU in order to try to reduce the continuously growing
cyberattacks’ number. Now, the EU will indeed be able to sanction individuals
or entities involved in the cyberattacks carried out from outside the EU.
Europe seeks through this measure to protect as
far as possible the most critical infrastructures, regarding electoral or
health systems for example, from cybercriminals, by abolishing the impunity
which the international hackers seemingly enjoyed.
If there is no name on this famous list today,
the situation could change soon.
Recently, the British Foreign Secretary, Jeremy Hunt declared that “for too long now, hostile actors have been threatening the EU’s security through disrupting critical infrastructure, attempting to undermine democracy and stealing commercial secrets and money running to billions of Euros. Hence, this decision was necessary.”
It’s now very clear that the cyberattacks carried out by nations, against nations or entities, tend to multiply. It’s important to note that these sanctions can be retroactive. To this day, the sanctions are not clearly defined: travel bans and assets freeze against those we know have been responsible for these actions? Several options are presently being studied.
Faced with the upsurge and the continually increasing strength of cyberattacks, a simulation exercise of a cyberattack in the finance industry will be organized by the members of the G7, the world’s major economic powers.
In the French presidency context, France will
be the one that will run this test in which 24 financial authorities of the 7
members of the G7 will participate during 3 days.
Today it is no secret that the banking sector is
one of the most targeted by cybercriminals [according to an IBM’s research, 19%
of the attacks would aim banking institutions].
Thus, for the first time, the G7 countries organize a cyberattack cross-border simulation in early June 2019. This test is organized by the Banque de France (the central bank of France) and proposes the following scenario: a malware will be injected in a technical component widely used in the financial sector.
As indicated by Bruno Le Maire, the Minister of
Economy and Finance of France “cyber threats are the proof that we need more
multilateralism and cooperation between our countries”.
According to this argument, this same exercise
will be conducted at the same time in the other countries, giving it a specific
dimension. If other exercises of this kind have indeed already been done
before, particularly by the Bank of England and the European Central Bank, none
of these tests was done simultaneously.
What are the results sought in this joint exercise?
Firmly establishing the risks of a cyberattack’s epidemic spread, in order to
be able to enhance the infrastructures security and to ensure the reactivity in
case of attack and prevent a wide contagion.
The actors and utility providers invade the
connected world, benefiting from the innovations that the rest of the world
opportunely provides them. It wouldn’t be a problem if we didn’t live in an age
where hacking a power plant became possible.
In 2015 and 2016, hackers shut down power to
thousands of users in the middle of the Ukrainian winter. Since then, the
American government openly admitted that foreign powers tried every day to take
control of the energy grid control rooms of the United States. And this is
important because we are currently connecting decades old infrastructures in an
environment which is swimming with threats that it was never designed to
protect against.
Engineers have not always played well with
computer scientists. These disciplines are different, they are different
mindsets with different aims, different cultures and of course, different technologies.
Engineers can plan for accidents and failures, while cybersecurity
professionals plan for attacks. There are completely different industry
standards for each discipline and very few standards for the growing field of
the Internet of Things (IoT), which is increasingly weaving its way into
utility environments. Those two worlds are now colliding.
Much of the IT used in utilities infrastructure
was previously isolated, operating without fear of the hackers, with systems
built for availability and convenience, not for security. Their creators didn’t
consider how a user might have to authenticate to a network to prove that they
are a trusted actor. That might have been acceptable in the past, but now we
have a landscape littered with outdated machines weighed down with insecure
codes that are unequipped for modern IT threats. The upgrading of these systems
and the security afterward, won’t solve all those security problems and
replacing them entirely would be too expensive, difficult to envisage and
almost utopian for many. And today, this is a real problem to connect them in
an environment exposed to threats and adversaries searching for the next easy
target.
Today, the world tends to connect more and
more, particularly through Internet of Things (IoT), we talk about connected
cars, baby monitors connected to a parent’s smartphone and doorbells informing
homeowners who is at their doors, fridges, washing machines become connected…
and utilities follow the trends, naturally wanting to be part of this world’s
evolution towards the increasing computerisation of physical objects.
Exciting as these new innovations might sound, evidence
mounts every day of the IoT’s insecurity. Whether it’s hardcoded passwords, an
inability to authenticate its outward and inward connections or an inability to
update, there is little argument about their security. These products are often
rushed to market without a thought for this important factor.
Enterprises and governments are seizing the IoT
as a way to transform the way they do business, and utilities are doing the
same. Large infrastructures will increasingly be made up of IoT endpoints and
sensors – able to relay information to its operators and radically improve the
overall function of utilities.
Unfortunately, in the rush to innovation, eager
adopters often ignore the glaring security problems that shiny new inventions
often bring with them. In an industrial or utilities environment the IoT means
something that is similar at a descriptive level, but radically different in
real-world impact. A connected doll is one thing, a connected power plant is
another entirely!
The risks on utilities are real. There are
plenty of examples. Stuxnet, the virus which destroyed the Iranian nuclear
program is just one. The aforementioned attacks on the Ukrainian power grid
could be another. Furthermore Western governments, including France, now admit
that foreign actors are attempting to hack their utilities on a daily basis.
But if this is such a big problem, you might
ask, then why hasn’t it happened more often? Why haven’t we heard about such
potentially devastating attacks even more? Well, the fact is that many won’t
know they’ve already been hacked. Many organizations go for weeks, months and
often years without realizing that an attacker has been lurking within their
systems. The Ponemon Institute has found that the average time between an organization
being breached and the discovery of that fact is 191 days, nearly half a year.
This is especially true if one of those aged legacy systems has no way of
telling what is anomalous. Others may just hide their breach, as many
organizations do. Such attacks are often embarrassing, especially with the
regulatory implications and public backlash that a cyberattack on a utility
brings with it.
Furthermore, most attacks are often not
catastrophic events. They are commonly attempts to gain data or access to a
critical system. For most, that’s a valuable enough goal to pursue. Edging into
the more destructive possibilities of such an attack would essentially be an
act of war and not many cybercriminals want to earn the attention – or the ire
– of a nation state.
The theory of the
black swan –
theorized by Nassim Nicholas Taleb: a
situation that is hard to predict and seems wildly unlikely, but has
apocalyptic implications – fits perfectly here. We don’t know when, how or
if such an event might happen but we had better start preparing for it. Even if
the likelihood of such an event is small, the cost of waiting and not preparing
for it will be much higher. The IoT market, particularly in the utilities
sector need to start preparing for that black swan.
Public Key
Infrastructures (PKI) using certificates will allow utilities to overcome many of these
threats, providing unparalleled trust for an often hard to manage network.
It’s been built on interoperable and standardized protocols, which have been
protecting web-connected systems for decades. It offers the same for the IoT.
PKIs are highly scalable, making them a great
fit for industrial environments and utilities. The manner in which many
utilities will be seizing hold of the IoT is through the millions of sensors
that will feed data back to operators and streamline day-to-day operations,
making utilities more efficient. The sheer number of those connections and the
richness of the data flowing through them make them hard to manage, hard to
monitor and hard to secure.
A PKI ecosystem can secure the connections
between devices, the systems and those that use them. The same goes for older
systems, which have been designed for availability and convenience, but not for
the possibility of attack. Users, devices and systems will also be able to
mutually authenticate between each other, ensuring that behind each side of a
transaction is a trusted party.
The data that is constantly travelling back and
forth over those networks is encrypted under PKI using the latest cryptography.
Attackers that want to steal that data will find that their ill-gotten gains
are useless when they realize they can’t decrypt it.
Further ensuring the integrity of that data is
code signing. When devices need to update over the air, code signing lets you
know that the author of the updates is who they say they are and that their
code hasn’t been insecurely tampered with since they wrote it. Secure boot will
also prevent unauthorized code from loading when a device starts up. PKI will
only allow secure, trusted code to run on a device, hamstringing hackers and
ensuring the data integrity that utilities require.
The possibilities of an attack on a utility can
sometimes seem beyond the pale. Just a few years ago a hack on a power grid
seemed almost impossible. Today, news of IoT vulnerabilities regularly fills
headlines around the world. The full destructive implications of this new
situation have yet to be fully realized, but just because all we see are white
swans, it doesn’t mean a black one isn’t on its way.
Users will soon start demanding these security
provisions from companies. The Federal Energy Regulatory Commission (FERC) has
recently fined a utility company that was found guilty of 127 different
security violations $10 million. The company wasn’t named, but pressure groups
have recently mounted a campaign, filing a petition with FERC to publicly name
and shame it. Moreover, with the advent of the General Data Protection
Regulation and the NIS directive last year, utilities now have to look a lot
closer at the way they protect their data. All over the world, governments are
looking at how to secure the IoT, especially when it comes to the physical
safety risks involved. Utilities security matters because utilities hold a
critical role in the functioning of society. It is just as important that they
be dragged into the 21st century, as they are protected from it. PKIs can offer
a way to do just that.
Mike Ahmadi, DigiCert VP of Industrial IoT
Security, works closely with automotive, industrial control and healthcare
industry standards bodies, leading device manufacturers and enterprises to
advance cybersecurity best practices and solutions to protecting against
evolving threats.
This article on the publication of Mike Ahmadi, is from an article of Intersec website.
In a previous article of Lucie Loos dated of the 21st of last February, the study by the Duma, the lower Chamber of the Russian Parliament, of a draft legislation with the aim to create a “sovereign Internet” in Russia was mentioned. With this law, the country would be able to function in total independence if Russia was cut from the major global servers, by creating Russia’s internal DNS system, which would ensure the link between web address and IP address of the corresponding web servers, without relying on the root servers of the global Internet.
On Wednesday, the 1st
of May 2019, Vladimir Putin signed a bill to create Russia’s “Sovereign
Internet” into law, its entry into force is planned for November 2019.
Sovereign Internet: IT security or control of Internet?
The bill thus plans to create an “infrastructure
allowing to ensure the functioning of the Russian Internet resources in case of
the impossibility for the Russian operators to connect to the foreign sources
Internet servers”.
The Russian Internet service providers will
have to implement technical means allowing a “centralized control of the
traffic” on their networks in order to face potential cyberattacks from foreign
powerful countries. A control that will be done by Roskomnadzor, the agency in
charge of the monitoring of the Russian Telecom and Medias, which has been often
accused of arbitrarily blocking web content, and by the Russian Federal
Security Service (FSB).
Officially, the “sovereign Internet” was
created for the purpose of IT security, but according to many experts, this
might be an excuse. This bill is criticized and deemed by many militants as an
attempt to control web contents and progressively isolate the Russian Internet
in an environment of increasing pressure from the authorities regarding the
freedom of expression on Internet.
Many rallies against this bill were organized in Moscow and gathered thousands of Russians last March. Several weeks later, in a joint statement, many international human rights and freedom of expression organizations, of which Reporters without borders and Human Rights Watch, had called on Vladimir Putin not to sign the bill that is “against Moscow’s international commitments in terms of respect for Human rights and particularly poses a threat to media freedom and the rights to freedom of information for people in Russia”. Despite this, the Russian president chose to ignore it and thus the bill was signed on the 1st of May 2019, and will enter into force starting this coming November.
Nameshield uses cookies
Nameshield wishes to use cookies to ensure the proper functioning of the site and, with our partners, to measure its audience🍪.
Nameshield wishes to use cookies to ensure the proper performance of the website and, with our partners, to monitor its audience. More information in our Cookie Policy 🍪.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-advertisement
1 year
Set by the GDPR Cookie Consent plugin, this cookie is used to record the user consent for the cookies in the "Advertisement" category .
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
CookieLawInfoConsent
1 year
Records the default button state of the corresponding category & the status of CCPA. It works only in coordination with the primary cookie.
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Cookie
Duration
Description
_ga
2 years
The _ga cookie, installed by Google Analytics, calculates visitor, session and campaign data and also keeps track of site usage for the site's analytics report. The cookie stores information anonymously and assigns a randomly generated number to recognize unique visitors.
_gat_gtag_UA_25904574_14
1 minute
Set by Google to distinguish users.
_gid
1 day
Installed by Google Analytics, _gid cookie stores information on how visitors use a website, while also creating an analytics report of the website's performance. Some of the data that are collected include the number of visitors, their source, and the pages they visit anonymously.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Cookie
Duration
Description
NID
6 months
NID cookie, set by Google, is used for advertising purposes; to limit the number of times the user sees an ad, to mute unwanted ads, and to measure the effectiveness of ads.