PyeongChang Olympic Games: Cyberattack

PyeongChang 2018 Olympic Games: Cyberattack

It’s during the opening ceremony of the PyeongChang Winter Olympic Games that a cyberattack has aimed at the host infrastructure IT department.

Around 45 minutes before the start of the event, the servers and WI-FI network have been hit by an attack, which fortunately has not impacted the ceremony. However, in the Olympic Village, the press zone has been deprived of Internet connection and television. Furthermore, the official website of the PyeongChang 2018 Olympic Games has been unreachable for hours, hindering web users to print their tickets to access to the event. 12 hours were needed to completely restore the services.

The CIO didn’t wish to communicate on this attack origin, but PyeongChang 2018’s spokesperson points that “there was a cyberattack, the server has been updated yesterday (Sunday February 11), and we know the cause of the problem. We know what happened, this is a usual thing during Olympic Games. We will not reveal the source.” The CIO’s communication director, has assured “We refuse for now to reveal the details of our investigation, but we will do it.”

A cyberattack with destructive aim

Talos Security company’s two researchers have analyzed the attack though and observed that the purpose was not to retrieve sensitive or personal data contained on the organization server, but clearly to interfere with the games ‘running.

The virus samples’ analysis allowed to highlight its main purpose: the destructive aspect. Concretely, the effects caused by this cyberattack, were to delete the events of the calendar and the documents, and above all, to make the affected machine inoperable.

PyeongChang Games, victims once again

At a global scale and ensuring a visibility of choice for cybercriminals, this is not the first cyberattack suffered by the PyeongChang Olympic Games. At the end of December 2017, the infrastructure was hit by an attack mainly consisting of the sending of emails to the event organizers. According to the McAfee company, those mails contained Word files infected by a virus.

Russia, North Korea: the different leads considered

The potential attack’s perpetrators could be Russia, of which the delegation has been denied of the Games for doping reasons: before the Games, McAfee declared to have information indicating that hackers located in Russia had planned attacks in retaliation.

A possible North Korean involvement was also mentioned, despite the rapprochement that could be observed by the viewers during the opening ceremony.

An attack that shows, once again, the IT infrastructures ‘vulnerability despite the means implemented.
FIC 2018: Nameshield’s DNS Premium solution labelled France Cybersecurity

FIC 2018: Nameshield’s DNS Premium solution labelled France CybersecurityThese 23 and 24 January, has taken place in Lille, the 10th edition of the International Cybersecurity Forum (FIC). With 7000 participants, 240 partners and 60 represented nationalities, it is a major event in terms of cybersecurity and digital confidence, gathering all the actors in France and in Europe.
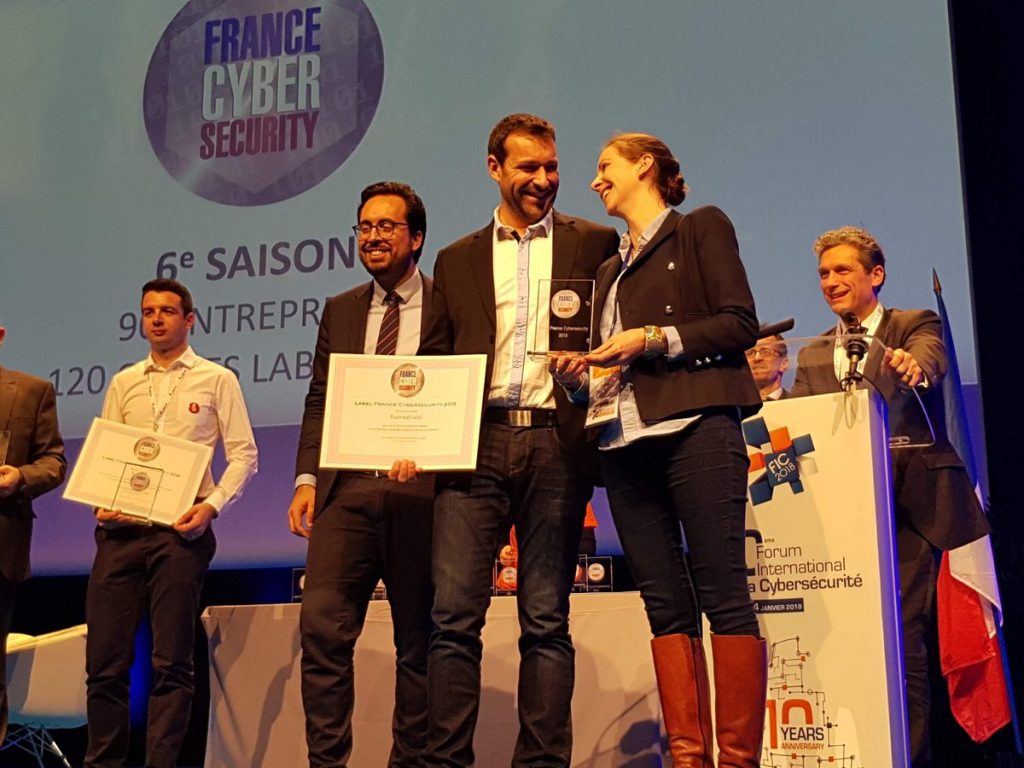
On this occasion, and for its first participation as a partner, Nameshield was given the France Cybersecurity label for its DNS Premium solution.

FIC 2018: Nameshield’s DNS Premium solution labelled France Cybersecurity
France Cybersecurity Label given by Mounir Mahjoubi, Secretary of State for Digital

The Nameshield’s labelled DNS Premium solution

The DNS is a well-known attack vector: DDoS, spoofing, Man in the Middle. The attacks are various and sophisticated. In front of the magnitude of these threats, maintaining its DNS infrastructure is complex.

Reliable and strong, the Nameshield’s highly secured DNS Premium is a DNS solution high availability, anycast and offers expert functionalities (anti-DDoS filter – Failover – GeoIP – DNSSEC – detailed statistics – etc.).

This solution labelled France Cybersecurity, thus allows to its users to protect their digital assets from any attack and ensures a high availability of their Internet services.

What is the France Cybersecurity label?

FIC 2018: Nameshield’s DNS Premium solution labelled France CybersecurityThe France Cybersecurity label is the guarantee for users that the Nameshield’s products and services are French and possess clear and well defined functionalities, with a certain level of quality in terms of cybersecurity, verified by an independent jury.

The France Cybersecurity Label answers to several needs and objectives:

  • Raise awareness among users and international ordering parties regarding the importance of the French origin of a Cybersecurity offer and its intrinsic qualities
  • Certify to users and ordering parties the quality and functionalities of labelled products and services
  • Promote French cybersecurity solutions and increase their international visibility
  • Certify to users and ordering parties the quality and functionalities of labelled products and services
  • Increase their overall use and the users’ security level

This label is governed by a committee composed of representatives gathered in 3 colleges:

  • College of officials: representatives from the Direction générale de l’armement (DGA, the French Government Defense procurement and technology agency), the Direction générale des entreprises (DGE, the French Directorate General for Enterprise within the Ministry of Economy, Industry and Digital), and the Agence nationale de la sécurité des systèmes d’information (ANSSI, the French National Cybersecurity Agency).
  • College of users: representatives from groups of users, such as: CIGREF, GITSIS, CESIN, CLUSIF ISSM space.
  • College of industrials: representatives from the “Alliance pour la Confiance Numérique” (ACN – Alliance for digital confidence) and HEXATRUST.

Nameshield certified ISO 27001 on all its registrar activity, was able to bring all the necessary guarantees to obtain the France Cybersecurity Label for its domain names securing offer, the DNS Premium and as highlighted by Gérard Gourjon, Nameshield’s Deputy Director-General: “Obtaining the France Cybersecurity Label illustrates our engagement to provide the best services and standards regarding cybersecurity to our customers. At Nameshield, we are proud to see our highly efficient and highly secured DNS infrastructure being labelled.”

For more information on our labelled solution DNS Premium: https://www.nameshield.com/en/cybersecurity/dns-premium/

For more information on the France Cybersecurity Label: https://www.francecybersecurity.fr/en/

SSL certificates reduction to 2 years maximum

SSL certificates reduction to 2 years maximum

The CAB forum, organization which defines the SSL certificates issuing and management rules approved the SSL certificates reduction to a duration of 2 years against 3 previously. Initiated by the browsers Chrome and Mozilla heading, this decision moves in the direction of an always more secured Internet by forcing the actors to renew more often their security keys and to stay on the last standards of the market.

This decision will be applicable to all Certification Authorities from March 1st 2018. In order to ensure a smooth transition, from February 1st 2018, Nameshield will not propose certificates with a 3 years duration anymore.

What impact for your certificates?

The new certificates will thus have a maximum duration of 825 days (2 years and 3 months to cover the possibility of 90 days early renewal). EV certificates were already under this scenario, so are concerned the DV and OV certificates in all their forms (standard, multi-sites or wildcard). Nothing in particular for these certificates.

For existing certificates, this new duration will have a consequence, since it will apply to all the certificates from March 1st. A 3 years certificate issued recently and which would need to be replaced beyond the 825 days deadline, will then have to be authenticated again. It is then important to know it to prevent urgent reissue, including for the simple SAN adding. You have to check beforehand if the certificate to replace may be impacted, this is the case of DV and OV certificates, the EV are also not concerned here.

Nameshield’s SSL team will inform you regarding the concerned certificates.

A bad phishing story

A bad phishing story

A victim of phishing from 2015, asked her bank for a refund of 3300€, which was the amount diverted by a fraud author. However, during the legal procedure, the Justice has cancelled the judgement of the local court of October 2017, which has requested to the bank of the victim to refund the corresponding amounts of the phishing operation.

The reason of this cancellation? The victim has deliberately communicated some confidential data regarding her credit card, by falling into the trap of a phishing email (the scammer has posed as the telephone operator of the victim).

This cancellation argument argues that indeed, the mail didn’t have any recipient nor sender name and that the reject or unpaid mention was inexact. Also the victim could have prevented the trap set and not communicate her banking information. Therefore, it was her responsibility, which indeed cancels the request for the stolen money refund by the bank.

The majority of phishing websites use domain names associated to an existing activity or referring to an activity, with the aim to deceive users, by inviting them to click on the links of legitimate websites. It allows to increase the likelihood of the attackers’ success.

The phishing concept is to retrieve personal data on Internet via identity theft, adapted to digital support.

If it is true that fraudulent payment online is directly caused by the victim’s negligence, yet, she didn’t communicate neither her credit card confidential code, nor the 6 digit 3D SECURE code, which was sent to her by SMS to validate the payment. The victim has blocked her credit card the same day, after the reception of two 3D secure messages.

However, in this case, the bank affirms that regularly, it has raised its customers ‘awareness and communicated with them, in order to alert them of phishing risks and warn them to never communicate their confidential banking data.

Thus, the Court of Cassation has judged that the victim acted carelessly and could have prevented to fall into the trap of the fraudster.

Cyber threats heavily rely on web users’ bad practices, as the SANS Institute confirms. The threats the most frequently encountered in companies are phishing (72% of the respondents), spywares (50%) and ransomwares (49%).

According to the American company Webroot, about 1.385.000 unique phishing websites are created each month, with an impressive peak of 2.3 million during May 2017.

Be aware that these phishing websites stay active during a very short period: between 4 and 8 hours maximum, to prevent to be followed or blacklisted.

Of course, this case reminds that vigilance remains crucial more than ever!

A phishing attack more and more sophisticated

A phishing attack more and more sophisticated

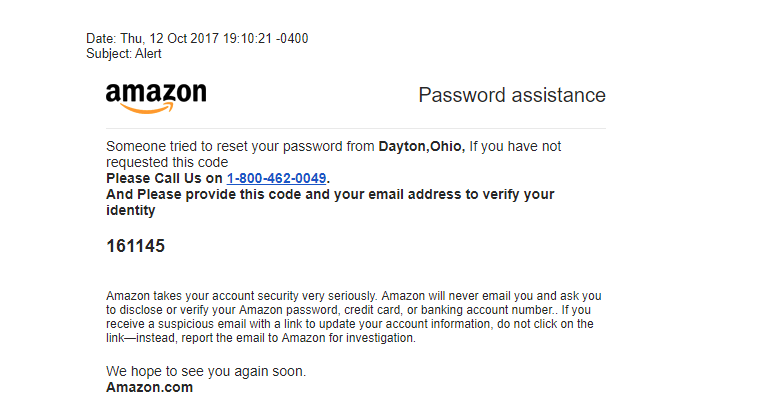
Recently, some Amazon users have been the victims of a quite sophisticated phishing attack.

They received a fake e-mail from Amazon, alerting them that someone attempted to connect to their account by trying to change their password. A six digit code was transmitted with the instruction to call a number to verify the user’s identity. If the web users were not the source of these actions, they were invited to follow a specific procedure to secure their account. When they called the supposed Amazon number, they were directed to a Customers service department, located abroad. During the call, they had to go on a website and communicate the code to ensure the security of the account.

The copy of the phishing message:

A phishing attack more and more sophisticated

Fortunately, many web users have detected this phishing attack and didn’t fall into the trap. But for the others, were they victims of a malware or a data theft?

All web users are hit by these phishing attempts. They are part of our daily lives, but many brands raise awareness among their customers against these actions (mostly the banking industry which is the privileged target of hackers).

To be continued.