DNS Belgium will now take offline fraudulent websites within 24 hours

DNS Belgium will now take offline fraudulent websites within 24 hours
Source of the picture: Kreutzfelder via Pixabay

In the context of the fight against insecurity on the web, DNS Belgium, the .BE registry, decided to intensify its action by cooperating with the FPS Economy [The FPS Economy, SMEs, Middle Classes and Energy is a Federal Public Service of Belgium which is responsible for contributing to the development, competitiveness and sustainability of the goods and services market in Belgium] in order to shut down fraudulent websites within 24 hours.

Philip Du Bois, general manager of DNS Belgium indicates: “This protocol will enable us to take even more targeted action, together with the FPS Economy, against possible abuses where .be domain names are involved. It underscores our ambition for a high quality and safe .be zone which serves as suitable environment for the further development of the Internet.”

The aim: to ensure consumers a completely safe Internet browsing on .BE websites.

This procedure will ensure a much higher reactivity. Indeed, until now, FPS Economy couldn’t request a blocking from the registry regarding the content, moreover fraudulent websites with correct identification data (at least of which the forgery couldn’t be proven), were untouchable. The blocking required a request from the Prosecution, i.e. a two weeks long procedure, which left plenty of time for the fraudulent website to create important damages to the consumers. Several hundreds of such websites per year were concerned!

From December, the 1st 2018, the protocol will then allow at the request of FPS Economy, the DNS Belgium registry to block .BE domain names which:

  • Are used for fraudulent websites
  • Host phishing websites

Of course, this procedure will be applied in the case of serious crimes.

The blocked domain name’s owner will have two weeks to react against the blocking. Without action of their part within 6 months, the blocked name will expire.

This still too rare initiative is to be welcomed in a context of the fierce fight against cybercriminality!
GDPR – What is the impact on your SSL certificates?

GDPR – What is the impact on your SSL certificates?
Source : mohamed_hassan via Pixabay

The European Data Protection Regulation (GDPR) came into effect on 25th May and its impact on the management of your SSL certificates portfolio is not neutral.

All Certification Authorities have previously always relied on the WHOIS of the domain name that needs to be certified in order to validate that the certificate applicant has the domain name technical operator’s agreement.

In order to validate an order, one of the authentication steps involved sending an email to one of the email addresses (admin or technical) found on the WHOIS.

However, the GDPR has left its mark and registrars no longer have the right to provide domain name owner personal data without the owner’s explicit consent. This means that the WHOIS database is unusable in terms of Certification Authorities being able to send out validation emails.

Faced with this situation, the Certification Authorities propose sending domain validation emails to one of the following generic addresses by default:

admin@domain.com
administrator@domain.com
postmaster@domain.com
webmaster@domain.com
hostmaster@domain.com

What if none of these addresses exist or is it too complicated to create?

There is an alternative solution. The Certification Authorities are able to validate that you have the domain name technical operator’s agreement through TXT record verification in the DNS zone of the domain name to be certified.

By verifying the presence of this TXT record, the Certification Authority is able to:

  • issue the certificate if it is a simple DV certificate (Domain validation)
  • continue to the next authentication steps if it is an OV (Organization Validation) or EV (Extended Validation) certificate.

Even with this in mind, the GDPR is changing the game and is having a significant impact on the SSL industry.
If the generic email validation method is not possible and we have to use TXT record verification method then we will indeed see an increase in certificate processing times.

What are the benefits of using Nameshield to manage your SSL certificates portfolio?

As a Registrar, Nameshield offers a unique market advantage for its SSL clients.
Nameshield carries out a pre-authentication process before each order reaches the Certificate Authority. This makes it possible to anticipate any blocking factors and if necessary to act quickly to resolve them:

  • Modification of a WHOIS
  • Edition of the zone to set up a TXT record (if the DNS are those of Nameshield)
  • Creation of alias admin @, administrator @, webmaster @, postmaster @, hostmaster @ (if the MX are those of Nameshield)

If you have any questions, please do not hesitate to call our dedicated SSL service.

A high school student tries to change his grades thanks to phishing

Phishing is cybercriminals’ means of choice to hijack users‘ data, posing as a trusty company and then encouraging them to deliver personal information. We are often more inclined to think that this technique is reserved to hackers who try to steal banking or very sensitive information, and yet!

Source : mohamed_hassan via Pixabay

An American student of Ygnacio Valley High School, in California, had a great time reproducing identically the website on which his teachers connect to enter marks and comments. This same student then emailed his teachers to connect to the fake school’s interface, which looked exactly the same as the original one. Thus, he could retrieve their login ID and passwords, and used them in order to raise his grades but also to lower his classmates’ grades.

Arrested by the police, the student said that what he had done was “as easy as stealing a candy from a baby”. Expelled from school, he was identified thanks to his computer IP address.

Quite light in consequence, this data corruption attempt highlights the simplicity of access to this hacking means. Today, phishing is one of the most popular methods and the easiest to implement. Web users, while unaware and fooled by similarities, consequently provide personal, sometimes very sensitive data.

Webstresser.org, the source of million DDoS attacks have been dismantled

Webstresser.org, the source of million DDoS attacks have been dismantled
Source : typographyimages via Pixabay

The good news just arrived, Webstresser.org, one of the websites most responsible of million DDoS attacks has been dismantled. This shutdown has been possible thanks to Europol’s active intervention.

For reminder, a DDoS is a cyberattack. The operating mode is to saturate queries servers so the websites hosted on these same servers cannot operate for web users anymore.

Many countries hand in hand to dismantle the network

According to the National Crime Agency’s research, Webstresser.org has been used by hackers for the launching of almost 4 million attacks around the world. Among its victims, there are many British banks.

To carry out this large scale operation, five countries, Croatia, Scotland, Canada, Netherlands and Serbia have combined their best policemen to lend a hand to Europol.

Although this is an operation of international concern, the German, Dutch and American authorities were in charge of closing the website definitely. Now, its operators can’t access it anymore and a message left by the American Ministry of Defense serves as the home page.

Heavy penalties for the hackers

The shutdown of webstresser.org also led to a wave of arrests in many countries like Scotland, Croatia and Serbia. According to the French law, a cyberattack is a criminal offence and the penalties are severe. Thus, if the attack aims individuals, the hacker or hackers can be sentenced to 5 years of imprisonment and a fine of 150 000 euros. If the attack touches the State or its institutions, the penalty can go up to 7 years of imprisonment and a fine of 300 000 euros.

Following this great haul, the Europol spokeswoman and operations coordinator, Claire Georges announced that measures will be taken against all users of the website around the world and that arrests will be expected.

Swaziland, the country that changes its name and its extension

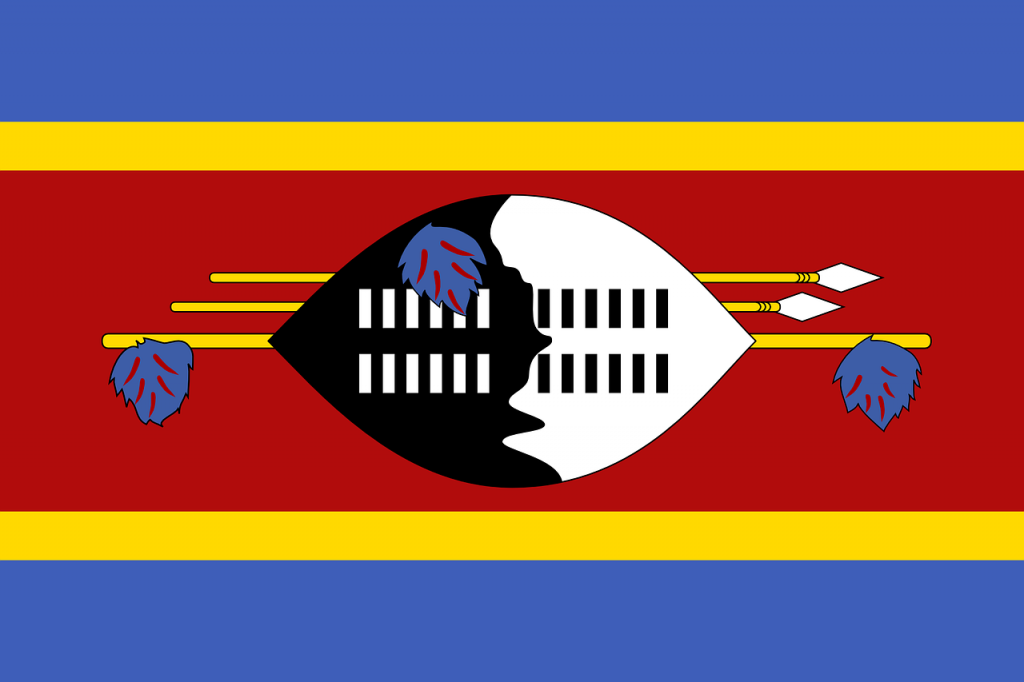
Source : OpenClipart-Vectors via Pixabay

We have learned from the press that Swaziland will change its name at the will of its Monarch.

Indeed, this little South African territory has not changed its name after the decolonization, fifty years ago. It will soon be the case, with the term eSwatini, the country of Swazi. If this information is more of a geopolitical notion, it will have an impact on the country’s abbreviation within the ISO standard 3166-1 alpha 2, and its extension will then change; a similar situation to the one of Kazakhstan, already discussed on this blog.

A new example which highlights the importance of the country’s stability in the choice of an extension used for an active communication.