Can the DNS have an impact on the SEO?

Can the DNS have an impact on the SEO?
Image source : geralt via Pixabay

This is a recurrent question from our customers: does the use of the DNS, whether it is good or bad, have an impact on the websites’ SEO? We have already discussed about the impact of a HTTPS website on the SEO, this is now the occasion to focus on the side of the DNS.

The DNS is an invisible process, implemented in the background, it’s difficult to comprehend why it can help or affect a website’s performance and the ranking in search engines, more particularly on Google.

This article will approach the possible impact of the DNS in response to the following questions:

  • Does the modification of a DNS record affect the SEO?
  • Does the change of the DNS provider affect the SEO?
  • Which part of the DNS plays in a website’s migration?
  • Does the change of a website’s IP address affect the website’s SEO?
  • Quid of the DNSSEC implementation?
  • Can a DNS breakdown affect the SEO?
  • Can a faster DNS increase the SEO?

Does the change at the DNS level affect the SEO?

1. Modification of a DNS record, be careful of the TTL

The domain name’s redirection towards the corresponding web server often passes through the creation of a A type record (IPv4 address). The A record will then direct the traffic towards the IP address of the destination web server. The modification of this record can lead to performance problems.

Indeed, to optimize the response time, the DNS system allows the  information caching with the DNS resolver servers for a given time, the duration of the TTL (Time to live) defined by the technical manager of the domain name, during its configuration. The usual TTL, like the one recommended by ANSSI, is several hours for the usual uses of domain names (websites). In the case of a A record modification, this one could be taken into account only at the end of the TTL. Then web users could still access to the former record configurations for a few minutes or even several hours after the modifications.

Thus it’s important to reduce the TTL, even temporarily during these modifications.

But does that affect the SEO? Yes, it does and no, it doesn’t. In the case of users being sent towards a destination that no longer exists, Google will consider this as a 404 error. Beyond the negative user experience, this is not directly a SEO factor. However be careful of the possible existence of backlinks and the too high numbers of 404 errors. A low TTL allows to limit the impact during these modifications.

2. Modification of the DNS declared for a domain name

A domain name is associated to the name servers (NS/Name Servers) which allow the right DNS resolution. The DNS service searches the information on these NS. These NS can be modified during the change of the provider managing the domain name, or simply to pass from a DNS infrastructure to another. Will the change of the name server affect the SEO?

Depending on the provider and the chosen infrastructure, the resolution time could be more or less short with a possible impact of improvement or decrease regarding the SERP (Search Engine Result Page). Indeed, the resolution time is taken into account by Google (see after).

And like for a record change, it is recommended to reduce the lifespan of the records before modifying the name servers, so the DNS resolvers don’t keep in cache the former information.

3. Risk associated to the DNS during the website’s migration

This is the same principle discussed previously. The modifications of the DNS configurations don’t directly affect the SEO, but can lead to a bad user’s experience. The TTL should also be seen as a useful mean to take into consideration.

Which specific cases to consider?

  • Change of web hosting provider
  • Change of DNS hosting provider?
  • Move the traffic of www. towards a “nude domain” (without www.)
  • Move your domain towards a CDN (content diffusion network)

4. Change of the destination IP address

No. During the modification of a record pointing from a termination point to another, the SEO is not affected. The only (very rare) exception to this rule would be to point a domain towards a termination point that would have been already identified as a spam server (for example, the IP address of a shared server).

However, be careful of the IP address in question, one of the (many) rules of Google’s SEO is that an IP address used for a website should be located near the final user.

5. DNSSEC implementation

DNSSEC allows to authenticate the DNS resolution through a chain of trust between the different DNS servers of this resolution. Just like for the HTTPS, this is an additional security layer to implement. And like for the HTTPS, the pages’ loading time is affected, and therefore potentially the associated SEO. To put this into perspective, DNSSEC is essential to web users’ surfing and it is recommended to implement it.  Most companies that propose security audit regarding domain names consider DNSSEC as necessary and then as a notation criteria.

Do faster DNS increase the SEO?

Google admitted that the loading time of a web page has an impact on the SERP results. The times of the DNS research are in general less than a second, they can nevertheless affect the loading of a webpage in the following cases:

1. Recurring breakdowns on the DNS infrastructure

When a DNS cannot resolve or takes more time than usual, it can add many seconds to the time of a page loading. In case of lack of reliability and recurring unavailability, the impact on SEO is proved… Not mentioning the user experience in front of these repetitive failures (increase of the bounce rate, decrease of customers’ retention and impact on the trust in the brand, if not revenue loss). It is important to rely on a reliable and trustworthy infrastructure.

2. Quality of the network and points of presence

This is purely and simply physics, the nearest a names server is to the final user, the less time is needed to respond to its request. The DNS networks called “anycast” (optimized addressing and routing towards “the nearest” or the “more efficient” server) with many points of presence in the world, allow to optimize the response time depending on the geographical location.

Another important point is to have at least three names servers that are authority (SOA) for a domain name, ideally based on different domain names and TLDs, in order to reduce the risk of SPOF (Single Point of Failure) of an infrastructure. Indeed, if an infrastructure relies on the same domain name, an unavailability of this domain name, for whatever the reason, leads to the unavailability of the DNS infrastructure. Likewise, at the TLDs’ level and even if it is less likely, a problem of registry availability would affect all the DNS infrastructure.

3. Be careful of “extended” DNS configurations

It’s not unusual to have DNS configurations which send towards a final destination through several steps like in the example below.  As a consequence, the resolution time is affected and potentially, the performance in terms of SEO.

fr.wikipedia.org. IN CNAME text.wikimedia.org.

text.wikimedia.org. IN CNAME text.esams.wikimedia.org.

text.esams.wikimedia.org. IN A 91.198.174.232

Conclusion

The SEO is a science to consider as a whole. Thus, as we have seen through the impact of the HTTPS adoption of a website, this is a referencing factor among others and all things being equal, then this is particularly important in order to achieve a competitive edge on the first page of results.

The same applies to the impact of DNS on the SEO. Can the DNS have an impact? Yes, it clearly can in the case of incorrect configurations, or in the case that the DNS infrastructures do not allow response times fast enough. A DNS infrastructure called anycast is essential for any domain name carrying an important web traffic, even more at an international level. This is a data to integrate in a whole, and this thinking should be in a global approach of the SEO with the web marketing team.
Cyberattacks, the companies more and more efficient

Cyber resilience- Cyberattacks, the companies more and more efficient
Image source : VISHNU_KV via pixabay

Last September, Accenture published the research “Gaining Ground On the Cyber Attacker 2018 State of Cyber Resilience” and highlighted the doubling of the cyberattacks number suffered by the companies (232 on average in 2018 versus 106 in 2017 at international level), but also the improvement of the companies’ ability to identify and counter these attacks.

The attacks number has more than doubled between 2017 and 2018…

This research deserves attention as it differentiates from many very alarmist reports. If everything is not perfect, in particular due to the ingenuity and increasing complexity of the attacks, the companies continue to improve their defense capacity, were able to strengthen their cyber resilience and stood efficient despite the threats. The companies are able to defend themselves better, particularly by detecting the attacks much earlier.

… But where a third of the attacks were successful in 2017, the part of successful attacks decreased to 1 on 8 (12,5%) in 2018.

A report that blows hot and cold

Security teams have made great progress but there is still more work to be done. Companies now prevent 87% of all targeted attacks, but are still facing two to three security breaches per month on average.

Companies might be cyber resilient in two to three years, but the pressure and the threats’ complexity increase every day. If 90% of the respondents expect the investment in cybersecurity to increase in the next 3 years, only 31% think that it will be sufficient.

The new technologies are essential, but the investments are lagging behind. If 83% of the respondents agreed that new technologies are essential, only two out of five are investing in AI, machine learning and automation technologies.

Confidence around cybersecurity measures remains high, but a more proactive approach of the cybersecurity is needed. If more than 80% of the respondents are confident in their capacity to monitor breaches, on the other hand 71% said that cyberattacks are still a bit of a black box, they do not know how or when they will affect their organization.

The board of directors and management are more engaged with cybersecurity. 27% of cybersecurity budgets are authorized by the board of directors and 32% by the CEO. The role and responsibilities of the CISO must improve towards more transversality in the company.

5 steps to cyber resilience

Accenture highlights five steps to optimize the companies’ defense and move towards the ultimate aim of cyber resilience in a world that continues to change towards new threats territories (artificial intelligence, omnipresence of the cloud, social networks, smartphones, internet of things) for more and more complex threats difficult to counter and a need becoming strategic: the data protection.

  • Build a strong foundation by identifying high value assets, in order to better protect them including from internal risks. It is necessary to ensure that controls are implemented throughout the value chain of the company.
  • Test the IT security by training cybersecurity teams to the best hackers’ techniques. The role plays staging an attack and defense team with training coaches can allow to bring out the improvement points.
  • Employ new technologies. For a company, it is recommended to invest in technologies able to automate cyber defense and in particular to use the new generation of identity management which relies on multi-factor authentication and the user behavior monitoring.
  • Be proactive and anticipate threats by developing a strategic team (“threat intelligence”) in charge of evolving an intelligent security operation center (SOC) relying on a collect and mass analysis of the data (“data-driven approach”).
  • Evolve the role of the CISO (Chief information security officer). The CISO is closer to professions, they find the right balance between security and risk taking and they communicate more and more with the executive management, which now holds 59% of the security budget versus 33% a year ago.

Conclusion

The Accenture study highlights a real growing awareness on cyber threats by companies, and the implementation of investment to better protect themselves. The race is now launched to tend to cyber resilience, between more and more organized attackers and more and more sophisticated defense system. See you at the end of the year to make an assessment of the forces involved.

Google makes HTTPS encryption mandatory for its 45 new TLDs : .dev / .app / .how…

Google makes HTTPS encryption mandatory for its 45 new TLDs - HSTS
Source : Sean MacEntee via flickr

In a recent article in this blog, we mentioned the arrival of Chrome 68 in July 2018 and the fact that HTTP will be considered “not secure” from then on. Well, this is not the only weapon that Google is planning to use to encourage large-scale adoption of encrypted websites.

You may not be aware, but Google has submitted a number of applications to ICANN as part of the new TLD program, and as a registry, they have secured the management of 45 top-level domains*. Just as the .bank and .insurance extensions have very strict security rules, Google has announced that they will apply HSTS implementation and pre-loading to their new TLDs therefore making HTTPS implementation mandatory.

What is HSTS?

HTTPS Strict Transport Security (HSTS) is a way in which browsers automatically enforce HTTPS-secured connections instead of unsafe HTTP. For example, if the website http://www.nameshield.net is on the list, a browser will never make insecure connections to the website, it will always be redirected to a URL that uses HTTPS and the site will be added to its list of sites that must always be accessed through HTTPS. From thereon, the browser will always use HTTPS for this site, whatever happens, whether the user has accessed the site via a Favorite, a link or simply by typing HTTP in the address bar, he has nothing more to do.

HSTS was first adopted by Chrome 4 in 2009, and has since been integrated in to all major browsers. The only flaw in the process is that browsers can still reach an unsafe HTTP URL the first time they connect to a site, opening a small window for attackers to intercept and carry out such attacks as Man-in-The-Middle attacks, misappropriation of cookies or the Poodle SSLv3 attack which was very much in the news in 2014.

A fully secured Top-Level Domain

HSTS pre-loading solves all this by pre-loading a list of HSTS domains into the browser itself, eliminating the threat of attacks. Even better, this pre-loading can be applied to entire TLDs, not just domains and subdomains, which means that it becomes automatic for anyone who registers a domain name ending in that TLD.

Adding an entire TLD to the HSTS pre-upload list is also more efficient because it secures all domains under this TLD without having to include all of the domains individually. Since HSTS pre-load lists can take months to update in browsers, TLD setup has the added benefit of making HSTS instant for newer websites that use them.

HTTPS deployment will be obligatory for .app and .dev extensions

Google is therefore planning to make HSTS mandatory for its 45 TLDs in the coming months. What does that mean? Millions of new sites registered under each TLD will now be HTTPS (and domain owners will need to configure their websites to switch to HTTPS or they will not work). In order to use a .dev, .app, .ads, .here, .meme, .ing, .rsvp, .fly … domain name, you will need to acquire an SSL certificate and deploy HTTPS.

Our team is at your disposal for any questions related to TLDs, domain names or SSL certificates.

* Google’s 45 TLDs: .gle .prod .docs .cal .soy .how .chrome .ads .mov .youtube .channel .nexus .goog .boo .dad .drive .hangout .new .eat .app .moto .ing .meme .here .zip .guge .car .foo .day .dev .play .gmail .fly .gbiz .rsvp .android .map .page .google .dclk .search .prof .phd .esq .みんな .谷歌 .グーグル

SSL certificates reduction to 2 years maximum

SSL certificates reduction to 2 years maximum

The CAB forum, organization which defines the SSL certificates issuing and management rules approved the SSL certificates reduction to a duration of 2 years against 3 previously. Initiated by the browsers Chrome and Mozilla heading, this decision moves in the direction of an always more secured Internet by forcing the actors to renew more often their security keys and to stay on the last standards of the market.

This decision will be applicable to all Certification Authorities from March 1st 2018. In order to ensure a smooth transition, from February 1st 2018, Nameshield will not propose certificates with a 3 years duration anymore.

What impact for your certificates?

The new certificates will thus have a maximum duration of 825 days (2 years and 3 months to cover the possibility of 90 days early renewal). EV certificates were already under this scenario, so are concerned the DV and OV certificates in all their forms (standard, multi-sites or wildcard). Nothing in particular for these certificates.

For existing certificates, this new duration will have a consequence, since it will apply to all the certificates from March 1st. A 3 years certificate issued recently and which would need to be replaced beyond the 825 days deadline, will then have to be authenticated again. It is then important to know it to prevent urgent reissue, including for the simple SAN adding. You have to check beforehand if the certificate to replace may be impacted, this is the case of DV and OV certificates, the EV are also not concerned here.

Nameshield’s SSL team will inform you regarding the concerned certificates.

The CAA becomes mandatory in the small SSL’s world

Or how to benefit from it to implement a certification strategy specific to your company?

The CAA becomes mandatory in the small SSL’s world

In January 2013, a new type of DNS Resource Record has appeared to improve the control chain in the SSL certificates issuing. This record, called CAA for Certificate Authority Authorization, allows to specify for a given domain name which Certification Authorities are authorized to issue certificates.

It’s an extremely interesting creation, in particular for big companies and groups, which technical teams are scattered in the World and for which it’s often difficult to require a global certification strategy. It’s not unusual for companies to accidentally discover the existence of certificates requested by teams not knowing the processes, by external consultants, issued by Certification Authorities with a bad image, or for certificates of low level of authentication (DV). The implementation of CAA record on your domain names is a good solution to control what the teams are doing and the news on SSL’s world will help you do that.

Indeed, if the CAA has been detailed in the RFC-6844 from 2013, it was not mandatory until today, for a Certification Authority to check if it was authorized or not to issue a certificate on a given domain name, hence a certain uselessness of this and a very low adoption.

September 8th, 2017 – The CAA checking becomes mandatory

We had to wait until March 2017, and a positive vote of the CAB/forum (ballot 187) to make this verification mandatory. Since the 8 September, the Certification Authorities have the duty to do this verification at the risk of sanctions from CAB/forum and browsers, the recent news regarding Google and Symantec has shown us how it’s not in their interests.

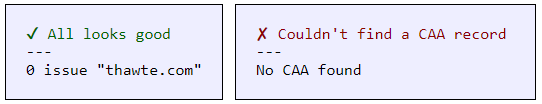
Three scenarios occur during this verification on a given domain name:

  • A CAA record is set and indicates the Certification Authority name, this one can issue the certificate.
  • A CAA record is set and indicates a Certification Authority’s name different, this one CANNOT issue the certificate.
  • No CAA record is set, any Certification Authority can issue a SSL certificate.

The CAA becomes mandatory in the small SSL’s world

It’s important to note that for a given domain name, many CAA records can be declared. A simple tool (among many others) to test your domain name, is available online: https://caatest.co.uk/

How to benefit from CAA for my company?

If it’s not already done, the establishment of the CAA checking is the opportunity for your company to define a certification strategy and to be able to ensure that it is complied with.

Define one (or multiple) Certification Authority corresponding to your values and to your expectations in term of service quality is a first step.

It will require to put around the table the marketing stakeholders to validate the impact on websites display and the technical services to ensure of the chosen provider’s quality. It will then be necessary to declare these CAA records in the different zones of your domain names.

It’s then important to communicate with all the operational staff so they become aware of the rules imposed within the company, in order not to block them in obtaining a certificate.

Indeed, Nameshield’s experience shows that SSL certificates are often requested in a hurry; moreover the browser’s last versions are not kind towards certificates’ errors by ostensibly displaying “not secure”. In consequence, blocking the issuing of a certificate because the communication didn’t get through can be damaging.

Such strategy presents real advantages in the control of certificates, in marketing, technical, risks control and costs associated to certificates. It’s necessary to conduct it with full knowledge and in order to do it, our SSL experts’ team can assist you.