2020 and the SSL, a small prediction exercise

Browsers and Certification Authorities, the battle continues.
Cybersecurity - SSL 2020 - Nameshield Blog
Image source : TheDigitalArtist via Pixabay

2019 was a busy year, with growing differences of opinion between browsers makers and Certification Authorities, an explosion in the number of phishing sites encrypted in HTTPS and significant progress on the depreciation of TLS v1.0.

Discussions on extended validation, more generally the visual display of certificates in browsers, and the reduction of the duration of certificates have taken a prominent place. None of these discussions are over, no consensus seems to be emerging, 2020 is looking like a busy year. Time to look ahead…

Will the fate of Extended Validation be determined?

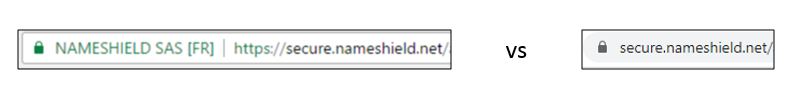
2019 saw the main browsers stop displaying the famous green address bar with the padlock and the name of the company, in favor of a classic and unique display, no longer taking into account the authentication level of the certificates:
SSL 2020 - EV certificate - Nameshield

However, discussions are still ongoing at the CA/B forum level, as well as within the CA Security Council. Both of these certificates regulatory bodies will be looking in 2020 for an intuitive way to display identity information of websites.

Historically approved by everyone, including the financial industry and websites with transactions, EV (the acronym for Extended Validation) was Google’s target in 2019. Other browsers, under the influence of Google, between Mozilla financed by Google and Microsoft and Opera based on Chromium open source, have followed in this direction. Only Apple continues to display EV.

For browsers, the question is whether or not TLS is the best way to present the authentication information of websites. It seems that it is not. Google assumes that it is not up to Certification Authorities to decide the legitimate content of a website and wants the use of certificates for encryption purposes only.

Of course, the Certification Authorities see things differently. One can certainly see a purely mercantile reaction, EV certificates are much more expensive. One can also wonder about the purpose of authentication beyond encryption. The answer seems to lie in the staggering statistics of phishing websites encrypted with HTTPS. Browsers have for the moment imposed an encrypted web indeed… but no longer authenticated!

2020 will therefore be the year of proposals from Certification Authorities: providing better authentication, including identification of legal entities, following the path of PSD2 in Europe… One thing is certain, identity has never been so important on the Internet and it is up to all interested parties to find a solution, including browsers to find a way to display strong authentication of websites. To be continued…

Certificates with a shorter duration: towards one-year certificates

825 days, or 27 months, or 2 years, the maximum duration currently allowed for SSL Certificates. However, since 2017 and a first attempt within the CA/B forum, the industry is moving towards a reduction of this duration to 13 months (1 additional month to cover the renewal period).

Google and browsers came back in 2019 with another vote submitted to the CA/B forum, again rejected but by a smaller majority. The market is on the move. Players like Let’sEncrypt propose certificates with a duration of 3 months, others want to keep long durations to avoid overloads of intervention on servers. One thing is certain, the market does not have the automation systems in place yet to make the management and installation of certificates easier, a delay of one or two more years would otherwise be preferable, or at least judicious.

But all this is without counting on Google threatening to act unilaterally if the regulator does not follow… certainly in 2020.

From TLS 1.0 to TLS 1.3: forced advance

Expected in January 2020, Microsoft, Apple, Mozilla, Google and Cloudflare have announced their intention to depreciate support for TLS 1.0 (a protocol created in 1999 to succeed SSL 3.0, which has become highly exposed) and TLS 1.1 (2006), both of which are currently suffering from too much exposure to security flaws.

While TLS 1.2 (2008) is still considered secure today, the market seems to be pushing for TLS 1.3, the most recent version of the standard, finally released in the summer of 2018. TLS 1.3 abandons support for weak algorithms (MD4, RC4, DSA or SHA-224), allows negotiation in fewer steps (faster), and reduces vulnerability to fallback attacks. Simply put, it is the most secure protocol.

A small problem, however, is that many websites are taking action. At the beginning of 2019, only 17% of the Alexa Top 100,000 websites supported TLS 1.3, while just under 23% (22,285) did not even support TLS 1.2 yet. If the decision to depreciate older versions of the protocol is a good one, the form adopted by the major web players can be criticized, in particular by its unilateral nature. In the meantime, get ready, we are heading there.

The threat of quantum computing

Companies are talking more and more about quantum computing, including Google. But the reality is, while quantum will impact our industry, it certainly won’t be in 2020, or for at least a decade. There are still many questions that need to be answered, such as: What is the best algorithm for quantum resistance? No one has that answer, and until there is a consensus in the industry, you are not going to see any quantum solutions in place.

IoT is growing, but the lack of security remains a problem

IoT is a success, but a number of deployments are being delayed due to a lack of security. In 2020, cloud service providers will provide or partner with security companies to provide a secure provisioning and management of devices, as well as an overall secure IoT ecosystem, for their customers.

The regulatory frameworks for IoT manufacturing and deployments will most certainly be led by the EU, although we will also see an increase in the US. Attacks, compromises and IoT hacking will, unfortunately, continue. In addition, security standards will not be met and we will not even come close to a higher percentage of secure devices. Why is that? Original Equipment Manufacturers (OEMs) are still not willing to pay the costs involved or pass them on to consumers for fear of losing sales.

China’s encryption laws will create a lot of uncertainty

In recent years, part of the digital transformation of the world has led to the codification of rights and restrictions on data in national laws and regional organizations. PSD2, GDPR, CCPA, PIPEDA… a real headache for international companies faced with regulatory standards and compliance.

On January 1, 2020, China’s encryption law was due to come into force. An additional data and… still unclear to those doing business in China. Clarification is still needed on several fronts. For example, commercial encryption for international companies must be approved and certified before it can be used in China – but this certification system has not yet been created. Similarly, there is uncertainty about the key escrow and the data that must be made available to the Chinese government. This has led to a wave of speculation, misinformation and, ultimately, overreaction. Given the opacity of parts of the new Regulation, many companies are opting for a wait-and-see approach. This is a wise tactic, assuming your organization does not have an experienced Chinese legal expert.

In conclusion, the certificates industry continues to change. Nameshield’s certificates team is at your disposal to discuss all these topics.

Best wishes for 2020.
The financial industry, the target of more and more costly attacks on the DNS

The financial services industry, the target of more and more costly attacks on the DNS
Image source: JimBear via Pixabay

Financial services companies are particularly affected by cyberattacks. They possess a wealth of information on the customers, protect their money and provide essential services which must be available day and night. They are a lucrative target. Among the favored lines of attacks: the DNS.

The Efficient IP’s Global DNS threat annual report shows a constant growth of the DNS attacks’ number and the financial impacts, with an average financial loss of 1.2 million euros in 2019. This amount was estimated at 513 000€ in 2017 and 806 000€ in 2018.

If all the industries are affected by cyberattacks, 82% of the companies surveyed have been affected and 63% have suffered a traffic disruption, the financial industry pays a more important price with 88% of impact. Conducted with 900 persons from nine countries of North America, Europe and Asia, the study indicates that financial companies suffered 10 attacks in average during the 12 last months, i.e. an increase of 37% compared to last year.

The increase of the costs is only one of the DNS attacks’ consequences for the financial services industry. The most common impacts are the cloud services’ downtime, experienced by 45% of financial organizations, and internal applications downtime (68%). Furthermore, 47% of financial companies have been the victims of frauds by phishing attacks aiming the DNS.

The survey clearly shows the insufficient security measures implemented for the DNS securing. The delay in applying security patches is a major problem for the organizations of this industry. In 2018, 72% of the interviewed companies admitted that a 3 days’ delay was necessary to implement a security patch in their systems, 3 days during which they are exposed to attacks.

Only 65% of the financial institutions use or plan to integrate a trusted DNS architecture, they seem to be always late and not to be sufficiently aware of the risks associated to this central point of their infrastructure. The evolution of the threats on the DNS is constant, the attacks are many and complex. It is essential to quickly react to better protect yourself.

Industry, trade, media, telecom, health, education, government, service… many others sectors are affected by the attacks. Some solutions exist. ANSSI publishes every year the guide of good practices regarding the DNS resilience, which details many recommendations in order to be protected. Relying on an Anycast network; possessing a protection system against DDoS attacks; having a monitoring of DNS traffic and a team able to take action quickly; possessing an efficient security policy … As many measures essential to the resilience and efficiency of the DNS network against these damaging attacks in terms of financial and image impact.

Hoping to see at last better figures in the 2020 report.

Soon a maximum duration of one year for SSL certificates?

Soon a maximum duration of one year for SSL/TLS certificates?

What is happening?

The industry actors plan to reduce the lifetime of SSL/TLS certificates, allowing the HTTPS display in browsers, to 13 months, i.e. almost half of the present lifetime of 27 months, in order to improve security.

Google through the CA/Browser Forum has indeed proposed this modification, approved by Apple and a Certification Authority, making it eligible to vote. During the next CA/B Forum meetings, if the vote is accepted, the modification of the requirements will come into effect in March 2020. Any certificate issued after the entry into force date will have to respect the requirements of the shortened validity period.

The aim for this reduction is to complicate things for cyber attackers by reducing the duration of the use of the potentially stolen certificates. It could also force companies to use the most recent and the most secured available encrypting algorithms.

If the vote fails, it’s not to be excluded that browsers supporting this requirement, unilaterally implement it in their root program, thus forcing the change to the Certification Authorities. It’s likely that this could be the case, this change follows Google’s precedent initiative that aimed to reduce the lifespan from three years to two years in 2018, period during which Google already wished to reduce it to 13 months or even less.

Who is impacted?

The changes proposed by Google would have an impact on all the users of TLS certificates of public trust, regardless of the Certification Authority that issued the certificate. If the vote passes, all certificates issued or reissued after March 2020 will have a maximum validity of 13 months. The companies using certificates with a validity period superior to 13 months will be encouraged to reconsider their systems and evaluate the impact of the proposed modifications on their implementation and their use.

The TLS certificates issued before March 2020 with a validity period superior to 13 months will stay operational. The public non-TLS certificate, for the code signing, the TLS private code and clients’ certificates, etc. are not concerned.  It will not be necessary to revoke an existing certificate following the implementation of the new standard. The reduction will have to be applied during the renewal.

What do the market players think about this?

It would be a global change for the industry with impacts on all the Certification Authorities. They view this proposition in a negative light. We can see an economic interest above all, but not solely…

The main argument is that the market is not ready in terms of automation system of orders and certificates implementations. Indeed, there would be more human interventions with the risks associated with poor handling, or simply a higher risk of forgetting a certificate renewal.

For Certification Authorities, reducing the certificates’ lifespan to such a short term mainly presents an increase of the human costs related to the certificate portfolio management. If they are not fundamentally against this decision, they would particularly like more time to study what users and companies think.

The position of browsers makers

Be it Google or Mozilla, the spearheads of the native HTTPS massive adoption for all websites and the supporters of the Let’sEncrypt initiative, what is important is the encrypting of all web traffic. A reduction of the certificates lifespan reduces the risk of certificates theft on a long period and encourages the massive adoption of automated management systems. For these two actors, an ideal world would have certificate of maximum 3 months. If they are attentive to the market as to not impose their views too quickly, it is more than likely that in the long term the certificates’ lifespan will continue to decrease.

Nameshield’s opinion 

The market continues its evolution towards shorter and shorter certificates’ validity, as a continual decrease of the authentication levels and consequently a need for management automated solutions that will increase. We will align on these requirements and advise our customers to prepare themselves for this reduction which will, without a doubt, arrive. Our Certification Authorities partners will also follow this evolution and will allow to provide all systems of required permanent inventory and automation.

To be heard

The CA/Browser Forum accepts comments of external participants and all discussions are public. You can directly enter your comments to the Forum distribution list:  https://cabforum.org/working-groups/ (at the bottom of the page). Nameshield is in contact with CA/Browser Forum participants and will inform you of the future decisions.

The Nameshield SSL interface has had a complete makeover

The Nameshield SSL interface has had a complete makeover

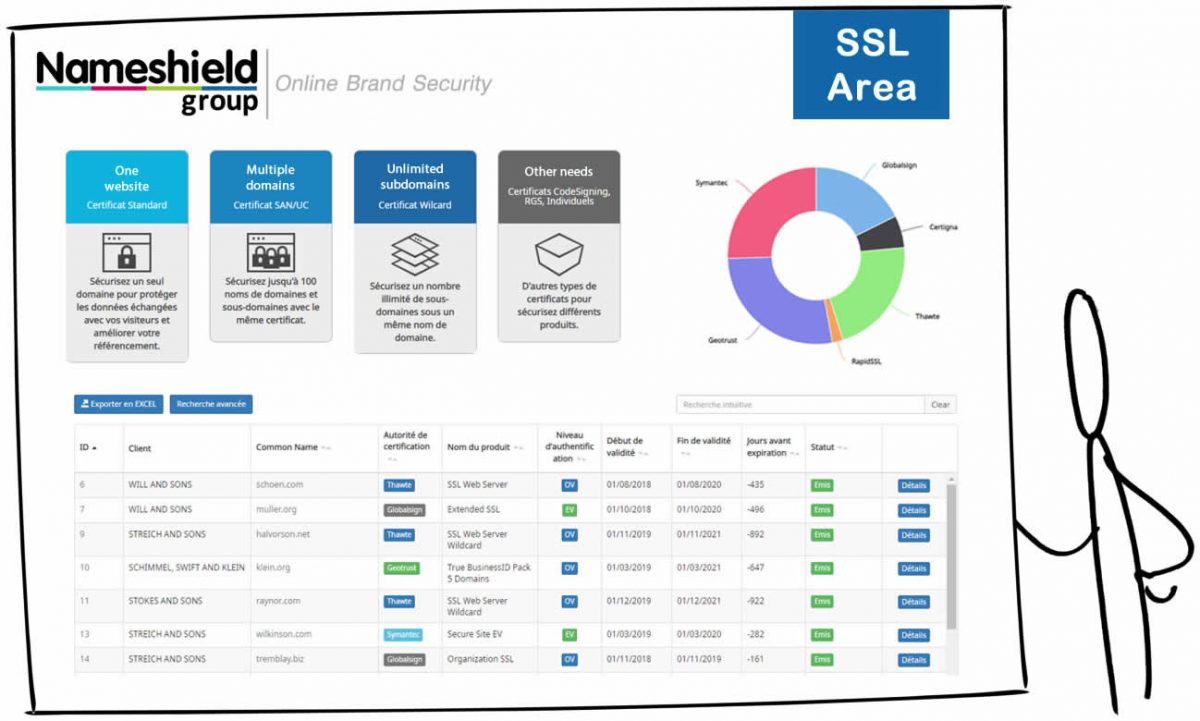
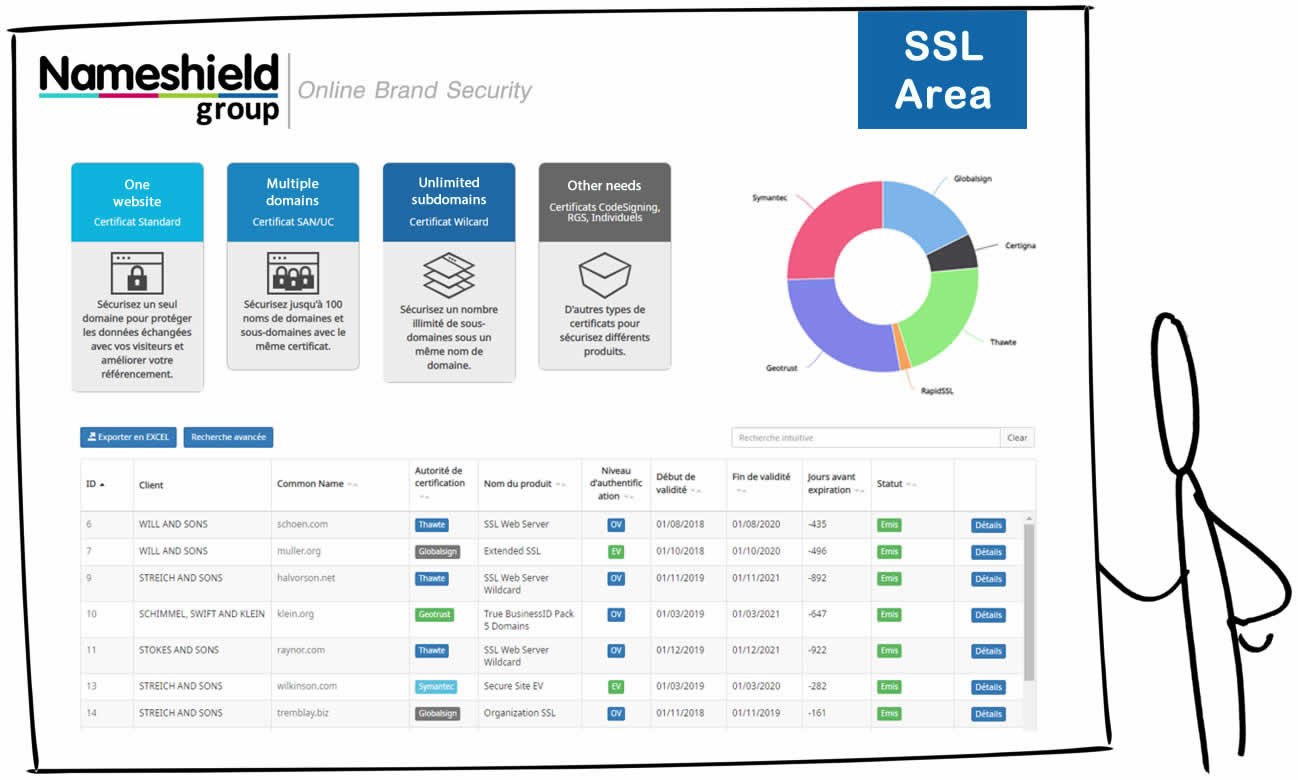
More user-friendly, more comprehensive, more attractive… our brand new and improved Nameshield SSL interface is being launched on Thursday, June 13th allowing you to manage all of your certificates.

You will now have access to key metrics on your certificate portfolio, to different certificate lookup views (such as complete portfolio, detailed overview, certificates nearing expiry, pending orders, expired or revoked certificates), to an Organization and Contact management tool and a redesigned ordering system.

Lastly, a decision support tool has been included in the interface to help you choose the certificate that’s right for your needs.

The certificate range has been updated to cover all types of certificates, SSL, RGS, Code Signing, Individual certificates and with all levels of authentication.

The SSL team remains at your disposal for a demonstration and a complete user guide is available covering all possible operations and actions.

Contact us directly at certificates@nameshield.net.

The Black swan time?

IoT-  The Black swan time?
Image source: abudrian via Pixabay

The actors and utility providers invade the connected world, benefiting from the innovations that the rest of the world opportunely provides them. It wouldn’t be a problem if we didn’t live in an age where hacking a power plant became possible.

In 2015 and 2016, hackers shut down power to thousands of users in the middle of the Ukrainian winter. Since then, the American government openly admitted that foreign powers tried every day to take control of the energy grid control rooms of the United States. And this is important because we are currently connecting decades old infrastructures in an environment which is swimming with threats that it was never designed to protect against.

Engineers have not always played well with computer scientists. These disciplines are different, they are different mindsets with different aims, different cultures and of course, different technologies. Engineers can plan for accidents and failures, while cybersecurity professionals plan for attacks. There are completely different industry standards for each discipline and very few standards for the growing field of the Internet of Things (IoT), which is increasingly weaving its way into utility environments. Those two worlds are now colliding.

Much of the IT used in utilities infrastructure was previously isolated, operating without fear of the hackers, with systems built for availability and convenience, not for security. Their creators didn’t consider how a user might have to authenticate to a network to prove that they are a trusted actor. That might have been acceptable in the past, but now we have a landscape littered with outdated machines weighed down with insecure codes that are unequipped for modern IT threats. The upgrading of these systems and the security afterward, won’t solve all those security problems and replacing them entirely would be too expensive, difficult to envisage and almost utopian for many. And today, this is a real problem to connect them in an environment exposed to threats and adversaries searching for the next easy target.

Today, the world tends to connect more and more, particularly through Internet of Things (IoT), we talk about connected cars, baby monitors connected to a parent’s smartphone and doorbells informing homeowners who is at their doors, fridges, washing machines become connected… and utilities follow the trends, naturally wanting to be part of this world’s evolution towards the increasing computerisation of physical objects.

Exciting as these new innovations might sound, evidence mounts every day of the IoT’s insecurity. Whether it’s hardcoded passwords, an inability to authenticate its outward and inward connections or an inability to update, there is little argument about their security. These products are often rushed to market without a thought for this important factor.

Enterprises and governments are seizing the IoT as a way to transform the way they do business, and utilities are doing the same. Large infrastructures will increasingly be made up of IoT endpoints and sensors – able to relay information to its operators and radically improve the overall function of utilities.

Unfortunately, in the rush to innovation, eager adopters often ignore the glaring security problems that shiny new inventions often bring with them. In an industrial or utilities environment the IoT means something that is similar at a descriptive level, but radically different in real-world impact. A connected doll is one thing, a connected power plant is another entirely!

The risks on utilities are real. There are plenty of examples. Stuxnet, the virus which destroyed the Iranian nuclear program is just one. The aforementioned attacks on the Ukrainian power grid could be another. Furthermore Western governments, including France, now admit that foreign actors are attempting to hack their utilities on a daily basis.

But if this is such a big problem, you might ask, then why hasn’t it happened more often? Why haven’t we heard about such potentially devastating attacks even more? Well, the fact is that many won’t know they’ve already been hacked. Many organizations go for weeks, months and often years without realizing that an attacker has been lurking within their systems. The Ponemon Institute has found that the average time between an organization being breached and the discovery of that fact is 191 days, nearly half a year. This is especially true if one of those aged legacy systems has no way of telling what is anomalous. Others may just hide their breach, as many organizations do. Such attacks are often embarrassing, especially with the regulatory implications and public backlash that a cyberattack on a utility brings with it.

Furthermore, most attacks are often not catastrophic events. They are commonly attempts to gain data or access to a critical system. For most, that’s a valuable enough goal to pursue. Edging into the more destructive possibilities of such an attack would essentially be an act of war and not many cybercriminals want to earn the attention – or the ire – of a nation state.

The theory of the black swan – theorized by Nassim Nicholas Taleb:  a situation that is hard to predict and seems wildly unlikely, but has apocalyptic implications – fits perfectly here. We don’t know when, how or if such an event might happen but we had better start preparing for it. Even if the likelihood of such an event is small, the cost of waiting and not preparing for it will be much higher. The IoT market, particularly in the utilities sector need to start preparing for that black swan.

Public Key Infrastructures (PKI) using certificates will allow utilities to overcome many of these threats, providing unparalleled trust for an often hard to manage network. It’s been built on interoperable and standardized protocols, which have been protecting web-connected systems for decades. It offers the same for the IoT.

PKIs are highly scalable, making them a great fit for industrial environments and utilities. The manner in which many utilities will be seizing hold of the IoT is through the millions of sensors that will feed data back to operators and streamline day-to-day operations, making utilities more efficient. The sheer number of those connections and the richness of the data flowing through them make them hard to manage, hard to monitor and hard to secure.

A PKI ecosystem can secure the connections between devices, the systems and those that use them. The same goes for older systems, which have been designed for availability and convenience, but not for the possibility of attack. Users, devices and systems will also be able to mutually authenticate between each other, ensuring that behind each side of a transaction is a trusted party.

The data that is constantly travelling back and forth over those networks is encrypted under PKI using the latest cryptography. Attackers that want to steal that data will find that their ill-gotten gains are useless when they realize they can’t decrypt it.

Further ensuring the integrity of that data is code signing. When devices need to update over the air, code signing lets you know that the author of the updates is who they say they are and that their code hasn’t been insecurely tampered with since they wrote it. Secure boot will also prevent unauthorized code from loading when a device starts up. PKI will only allow secure, trusted code to run on a device, hamstringing hackers and ensuring the data integrity that utilities require.

The possibilities of an attack on a utility can sometimes seem beyond the pale. Just a few years ago a hack on a power grid seemed almost impossible. Today, news of IoT vulnerabilities regularly fills headlines around the world. The full destructive implications of this new situation have yet to be fully realized, but just because all we see are white swans, it doesn’t mean a black one isn’t on its way.

Users will soon start demanding these security provisions from companies. The Federal Energy Regulatory Commission (FERC) has recently fined a utility company that was found guilty of 127 different security violations $10 million. The company wasn’t named, but pressure groups have recently mounted a campaign, filing a petition with FERC to publicly name and shame it. Moreover, with the advent of the General Data Protection Regulation and the NIS directive last year, utilities now have to look a lot closer at the way they protect their data. All over the world, governments are looking at how to secure the IoT, especially when it comes to the physical safety risks involved. Utilities security matters because utilities hold a critical role in the functioning of society. It is just as important that they be dragged into the 21st century, as they are protected from it. PKIs can offer a way to do just that.

Mike Ahmadi, DigiCert VP of Industrial IoT Security, works closely with automotive, industrial control and healthcare industry standards bodies, leading device manufacturers and enterprises to advance cybersecurity best practices and solutions to protecting against evolving threats.

This article on the publication of Mike Ahmadi, is from an article of Intersec website.