Nameshield signs up the Paris Call in order to actively contribute to the Internet’s stability

Paris Call - Nameshield

Just one year ago, in the context of the first Paris Peace Forum, the French President, Emmanuel Macron, launched the Paris Call for trust and security in cyberspace. This call is a political declaration aiming to express a mobilization on the stability in the cyberspace and strengthens the efforts of the international community and many actors involved in the digital security issues. This text reminds some principles that we think are fundamental, like the application of the international rights and the Human rights in the cyberspace. It also highlights the need of a multi actors’ approach, to create standards which will allow us to fully benefit, i.e. in a reliable and secure way, from opportunities provided by the digital revolution.

Lastly, the Paris Call promotes the strengthening of the digital products and services’ security that we use for example, in our daily lives. The text aims in that sense, to prevent cyberattacks perpetrated by malicious actors, which threaten all the users of the cyberspace.

Aware that our Society’s development, on the economic, cultural and democratic fronts, requires a strengthened trust of the information that flows through the Internet, Nameshield, which has worked for 25 years to protect the digital identity of its clients; companies, local collectivities and administrations through the use of their domain names, wished to join this initiative and sign the Paris Call.

Its job consists in ensuring the integrity and resilience of the identity of individuals and organizations on the Internet, represented today by the domain name. By highly protecting data on domain name identity cards (Whois) and by providing a high availability and high performance service through the associated Domain Name System (DNS), Nameshield contributes to a large extent to the second principle of the Paris Call: Protecting the Internet. To prevent activity that intentionally and substantially damages the general availability or integrity of the public core of the Internet.

Cornerstone of the Web, the Domain Name System (DNS) serves as the Internet directory. This protocol translates a domain name into an IP address, based on a database distributed on thousands of machines. If the DNS falls because of data corruption or a denial of service attack, all your websites and emails would become inaccessible, which is completely unthinkable nowadays! The DNS must be protected and must stay highly available.

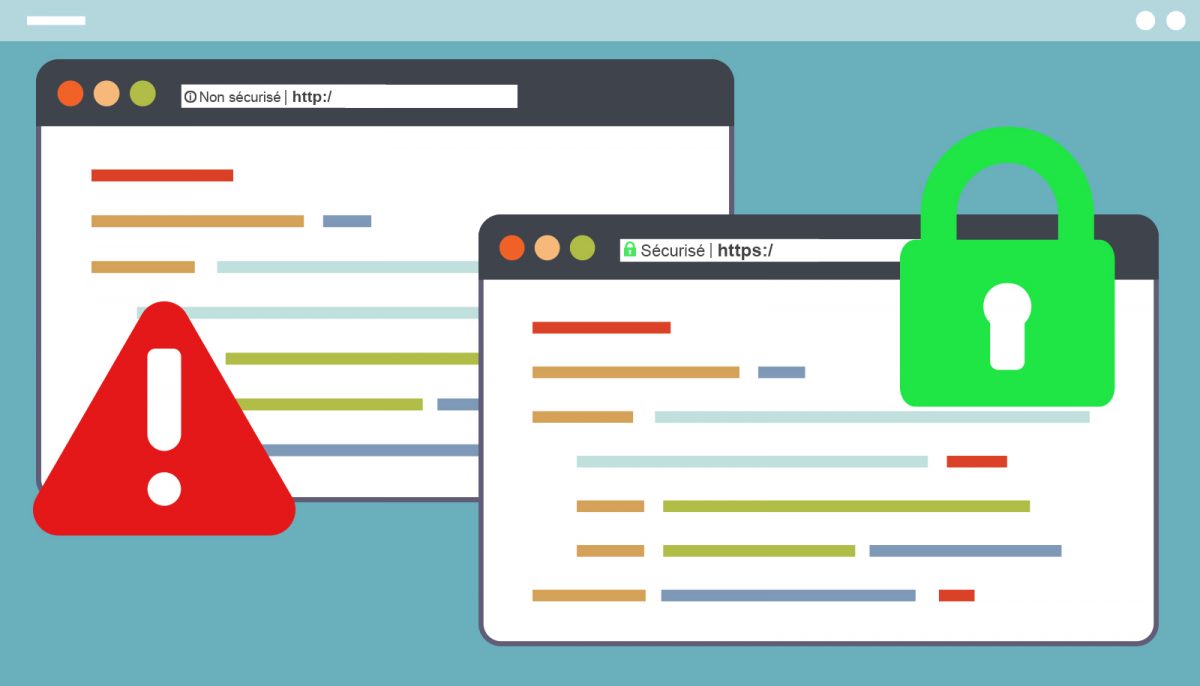
Protocol created in the 1980’s, security flaws regarding the usual functioning of the DNS have been identified since its creation. That is why, a new secured protocol, DNSSEC, has thus been developed to ensure the authenticity of the exchanges through a certified signature. Other solutions can complete the resilience of your identity on the Internet: the registry lock, SSL certificates…

The security solutions proposed by Nameshield, an independent French company that stores its data in France and possesses its own anycast and resilient DNS infrastructure, certified ISO 27001 on all its domain names activity, are compliant with the ANSSI recommendations on the good practices regarding the domain names’ acquisition and exploitation.

In the context of the 2nd Paris Peace Forum, the Ministry of Foreign Affairs wished to illustrate the second principle of the Paris Call: Protect the Internet by highlighting the services proposed by Nameshield. The company is proud to be able to collaborate, at its level, with the actors implicated in digital security issues in order to make the Internet more reliable and thus contribute to the security of the cyberspace.
https://pariscall.international/en/principles

Soon a maximum duration of one year for SSL certificates?

Soon a maximum duration of one year for SSL/TLS certificates?

What is happening?

The industry actors plan to reduce the lifetime of SSL/TLS certificates, allowing the HTTPS display in browsers, to 13 months, i.e. almost half of the present lifetime of 27 months, in order to improve security.

Google through the CA/Browser Forum has indeed proposed this modification, approved by Apple and a Certification Authority, making it eligible to vote. During the next CA/B Forum meetings, if the vote is accepted, the modification of the requirements will come into effect in March 2020. Any certificate issued after the entry into force date will have to respect the requirements of the shortened validity period.

The aim for this reduction is to complicate things for cyber attackers by reducing the duration of the use of the potentially stolen certificates. It could also force companies to use the most recent and the most secured available encrypting algorithms.

If the vote fails, it’s not to be excluded that browsers supporting this requirement, unilaterally implement it in their root program, thus forcing the change to the Certification Authorities. It’s likely that this could be the case, this change follows Google’s precedent initiative that aimed to reduce the lifespan from three years to two years in 2018, period during which Google already wished to reduce it to 13 months or even less.

Who is impacted?

The changes proposed by Google would have an impact on all the users of TLS certificates of public trust, regardless of the Certification Authority that issued the certificate. If the vote passes, all certificates issued or reissued after March 2020 will have a maximum validity of 13 months. The companies using certificates with a validity period superior to 13 months will be encouraged to reconsider their systems and evaluate the impact of the proposed modifications on their implementation and their use.

The TLS certificates issued before March 2020 with a validity period superior to 13 months will stay operational. The public non-TLS certificate, for the code signing, the TLS private code and clients’ certificates, etc. are not concerned.  It will not be necessary to revoke an existing certificate following the implementation of the new standard. The reduction will have to be applied during the renewal.

What do the market players think about this?

It would be a global change for the industry with impacts on all the Certification Authorities. They view this proposition in a negative light. We can see an economic interest above all, but not solely…

The main argument is that the market is not ready in terms of automation system of orders and certificates implementations. Indeed, there would be more human interventions with the risks associated with poor handling, or simply a higher risk of forgetting a certificate renewal.

For Certification Authorities, reducing the certificates’ lifespan to such a short term mainly presents an increase of the human costs related to the certificate portfolio management. If they are not fundamentally against this decision, they would particularly like more time to study what users and companies think.

The position of browsers makers

Be it Google or Mozilla, the spearheads of the native HTTPS massive adoption for all websites and the supporters of the Let’sEncrypt initiative, what is important is the encrypting of all web traffic. A reduction of the certificates lifespan reduces the risk of certificates theft on a long period and encourages the massive adoption of automated management systems. For these two actors, an ideal world would have certificate of maximum 3 months. If they are attentive to the market as to not impose their views too quickly, it is more than likely that in the long term the certificates’ lifespan will continue to decrease.

Nameshield’s opinion 

The market continues its evolution towards shorter and shorter certificates’ validity, as a continual decrease of the authentication levels and consequently a need for management automated solutions that will increase. We will align on these requirements and advise our customers to prepare themselves for this reduction which will, without a doubt, arrive. Our Certification Authorities partners will also follow this evolution and will allow to provide all systems of required permanent inventory and automation.

To be heard

The CA/Browser Forum accepts comments of external participants and all discussions are public. You can directly enter your comments to the Forum distribution list:  https://cabforum.org/working-groups/ (at the bottom of the page). Nameshield is in contact with CA/Browser Forum participants and will inform you of the future decisions.

NBA: Phishing doesn’t spare sports institutions

NBA: Phishing doesn’t spare sports institutions
Image source: mohamed_hassan via Pixabay

On last May 10th, in a press release, the Pacers Sports & Entertainment (PSE) organization, owner of the NBA’s basketball team the Indiana Pacers, revealed that they were the victim of a sophisticated phishing attack at the end of 2018.

For reminder, phishing is a technique used to obtain personal information in order to commit an identity theft.  This is a «social engineering» technique, i.e. consisting in exploiting not an IT flaw but a «human flaw» by deceiving web users through an e-mail seemingly coming from a trustworthy company, typically a bank or a business website.

Pacers Sports & Entertainment victim of a phishing attack

At the end of 2018, the company PSE has then been the target of a phishing emails campaign resulting in the unauthorized access to emails containing personal information related to a limited number of individuals.

This cyberattack affected a limited number of individuals but the amount of the stolen information is important: name, address, date of birth, passport number, driver’s license, state identification number, account number, credit/debit card number, digital signature, username and password and for some individuals, the Social Security number.

The American company has quickly implemented measures to secure the affected email accounts and investigate the incident with the assistance of forensic experts. This investigation then revealed that the hackers had access to the accounts of a limited number of persons between October 15th and December 4th, 2018. The press release doesn’t give any details regarding the identity of the targeted persons.

PSE individually notified each victim whose information has been stolen and assures that “to date, PSE has no evidence of actual or attempted misuse of any personal information”. The organization offered to the victims of the cyberattack an access to credit monitoring and identity protection services at no cost.

Some simple rules against phishing

Phishing attacks are increasing. Above all, they are becoming more and more sophisticated, and target all kinds of industries. Each and every one of us must be extra vigilant.

Lastly, for reminder, here are some simple rules to protect yourself against phishing attempts:

  • Do not reply when someone asks for your personal data by email;
  • Do not ever open an attachment from an unknown sender, or from one who is not entirely trustworthy;
  • Check the links by hovering the cursor over them (without clicking) to ensure that they link to trustworthy websites;
  • Do not trust the name of the mail’s sender. If there is any doubt, contact the sender through another method.

ANSSI annual report – The 5 cyber threats observed in 2018

ANSSI annual report – The 5 cyber threats observed in 2018
Image source: TheDigitalArtist via Pixabay

On April 15, 2019, ANSSI (the National Cybersecurity Agency of France), unveiled its annual report during a press conference. The agency identified 1869 alerts, 391 incidents without counting critical importance operators, 16 major incidents and 14 cyber defence operations for 2018. ANSSI also identified 5 major trends in terms of cyber threats observed in France and in Europe in 2018.

Analysis of cyber threat in 2018 – The 5 major trends

1.Cyber-espionage

Major concern for ANSSI in 2018, according to the agency, cyber-espionage represents the highest risk for the organizations.

Extremely discrete, benefiting from important financial resources, the attackers plan for many years highly targeted and highly sophisticated attacks. In 2018, it was noted that the cyber attackers are increasingly interested in vital activity sectors and specific critical infrastructures like the defence, health or research sectors.

2.Indirect attacks

According to ANSSI, indirect attacks have known an important increase in 2018. Indeed, to avoid the security measures implemented by big companies, which are more and more aware of the cyber risk, the attackers aim intermediaries, like providers, who are more vulnerable, to reach their final targets.

Compromising one partner is enough to reach many companies. So it is essential to choose partners that place their information system’s security at the top of their concerns.

3.Destabilization and influence operations

Because of the nature of the targets and the claims, these attacks though technically moderate, have often an important symbolic impact. An increase has been observed in 2018.

4.Cryptojacking

For reminder, cryptojacking is a cyberattack that consists in using the computer’s power of its victim to mine cryptocurrency.

In 2018, many attacks of this kind were observed. The more and more organized attackers benefit from the security flaws to compromise their victims’ equipment by placing cryptocurrencies’ miners without them knowing it.

5.Online frauds

Online frauds represent as much of a constant cyber threat for the companies and the big organizations as for the individuals. ANSSI noted an important growth of online frauds last year. Big operators are becoming more concerned about cybersecurity, so the attackers turn towards targets less exposed but more vulnerable, like territorial authorities or actors in the health sector which thus were the targets of many phishing attacks in 2018.

Conclusion

The multiplicity and the magnitude of the attacks observed during 2018, prove that it is essential to implement security measures to prevent these cyber threats, within big organizations, big groups as well as small companies.

“The conclusion is clear: 2018 proves once again that digital risk, far from being ethereal, must be at the heart of our concerns. Not only those of ANSSI! The cyberattacks affect all of society. That is why we must all seize the matter.” explains Guillaume Poupard, ANSSI’s General Director.

Cybersecurity overview – CESIN’s barometer

Cybersecurity overview
Image source: TheDigitalArtist via Pixabay

The CESIN (Club of Information and digital security experts) just published the fourth edition of its annual barometer realized with OpinionWay within its 174 members, 84% are CISO (Chief information security officer) of big French companies. This annual study allows to better define the perception and reality of cybersecurity and its issues within the companies which are members of CESIN.

The most common cyberattacks and their impacts

During these twelve last months, although the attacks number tends to stabilize, 80% of the interviewed companies have been the victims of at least one cyberattack, and the consequences on the business (stopping of the production, unavailable website, revenue loss…) are more important than in 2017.

Each year, companies face five kinds of cyberattack on average.

Among the attacks suffered, phishing is the most frequent with 73% of companies affected, followed by the “Fake President” fraud with 50% of the respondents affected, then in third position is the ransomware and the malware infection.

Regarding cyber risks, Shadow IT is the most frequently encountered risk, 64% of the interviewed CISO estimate that this is a threat to deal with. Indeed, the implementation and use of non-approved and often free applications can escape the control of the Information systems department.

Cloud and IoT: the impact of the digital transformation on the security of Information systems

For 98% of the companies, digital transformation has a real impact on the security of Information and data systems and increases the cyberattacks’ perimeter. Particularly through the important use of Cloud, used by 87% of the companies, of which 52% store their data in public Clouds.

This use of Cloud represents an important risk because of the lack of control from the hosting provider regarding the company’s data (through administrators or others), or regarding the subcontracting chain used by the hosting provider, or even regarding the data not deleted. For 89% of the CISO, these issues imply the use of complementary securing tools to the ones proposed by the service provider in order to secure the data stored in the Cloud.

Concerning IoT (Internet of Things), the race for innovation and the increasingly common use of connected things lead to the apparition of new cybersecurity threats, notably due to security flaws in these devices.

A cyber resilience to develop

To face these cyber risks, the CISO develop many technical solutions.

However, despite all these solutions, the CISO are less confident comparing to last year regarding the company’s capacity to face these cyber risks, and less than one out of two estimates that their company is prepared to manage a large scale cyberattack. And yet, only 12% have implemented a real cyber resilience program, it is in process for 33% and 34% are planning to implement one.

Three essentially human issues for the future of the cybersecurity

  • Awareness of the user

According to 61% of the interviewed CISO, the main issue for the future of the cybersecurity is the training and the awareness of the users to the cybersecurity issue. According to the respondents, “even if the employees are aware, they are still not involved enough and do not necessarily follow the recommendations. An important education work remains.”

  • Governance of the cybersecurity

For 60% of the respondents, the governance of the cybersecurity needs to be placed at the right level. Although the compliance to the GDPR allowed the companies to be aware of the data protection issues, the confidence in the ability of the executive committee to take into account the cybersecurity issues stays uneven depending on the activity sectors.

  • Human resources

The lack of Information system security profiles observed by 91% of the CISO, is a real challenge for the companies while 50% of these companies plan to increase the workforce allocated to cybersecurity.